David Gerarddavidgerard@circumstances.run
Oct 21, 2026, 9:07 PMthat PHP fix is 13k lines
5k apparently of non-tests
that's all human written, right? I wouldn't want to speak out of turn about sprawling quick fix diffs
that PHP fix is 13k lines
5k apparently of non-tests
that's all human written, right? I wouldn't want to speak out of turn about sprawling quick fix diffs
@davidgerard oh god, it could yet get funnier
 Oct 21, 2026, 9:12 PM
@davidgerard just a quick 13kloc fix for my personal homepage tools
@zzt @davidgerard "13,000 lines of code for my family."
@zzt
Fun fact: in Polish “kloc” can be translated to “log”, with more than one meaning.
@davidgerard ha
@davidgerard Even if this isn't that, at *some* point we're going to see a quick "everyone panic! Keystone tool XYZ is compromised!" 13kloc fix that fixes … something … then deliberately adds three more well-obfuscated backdoors.
@cstross if we haven't seen it yet we haven't noticed it
vibe code is a playground for the bad guys
@davidgerard We've spent more than 75 years trying to keep code and data separate and vibe coding just drunk-drove a bulldozer through a lifetime of hard-learned lessons about best practices.
@cstross @davidgerard Everyone knows the solution to in-band signaling is more in-band signaling with a lot of extra begging and pleading on top.

@theorangetheme @cstross @davidgerard my context window is nothing but "Please don't make mistakes. Pretty please don't make mistakes. Pretty please with a cherry on top don't make mistakes..."
@cstross @davidgerard vibe coding: what do you think would happen if we FA'd *at scale*
@djmitche @cstross @davidgerard it’ll be too big to fail, government bailout time
@djmitche @cstross @davidgerard Move fast and break things.
 Oct 21, 2026, 10:10 PM
We have and we haven't:
Every time we mix code and data, it becomes a festering wound in the flank of information security. We've had ample opportunities to learn the lesson, and still we run headlong in the wrong direction.
@cstross @davidgerard
Vibe Coding should be added to George Carlin's list of "words that do not go together"
Joining other famous phrases like
Jumbo Shrimp
Occasional Irregularity
And
Military Intelligence
@cstross @davidgerard We couldn't even make 'don't use modal dialogs' stick, why would we think that actually IMPORTANT structural things would stay with anyone?
@cstross @davidgerard Once the bubble pops/deflates a bit, LLMs may still be a long term good. Because while they absolutely *suck* at coding and anything where you have to be right all the time, they seem to be pretty good at red teaming and other things where you only have to be right once.
 Oct 22, 2026, 4:36 AM
@neoluddite @cstross @davidgerard There's a world of difference in effectiveness between a pure random generator and a fuzzer. And a similar world of difference between a fuzzer and an LLM.
@cstross @davidgerard@circumstances.run
Attack of the Von Neumanns
@cstross @davidgerard The practical leftover is still useful: treat the generated diff as untrusted input. Read it the way you would a patch from a stranger, and don't merge it until someone on the team can explain what it changes.
@cstross But *handwavey* guardrails will save us! Dark software factories are the future! When nobody looks at the code, nobody knows how terrible it is (until shit explodes and people die).
@cstross @davidgerard Having used coding agents, I'll say that is not a hard rule... but I also wouldn't trust anything I couldn't personally review.
 Oct 22, 2026, 1:09 PM
@cstross @davidgerard Their entire philosophy, soup to nuts, derives from Sutton's Bitter Lesson, which (paraphrased and somewhat corrupted) says that no result of human study can ever match the accuracy of a learning algorithm with sufficient compute.
Sutton meant it as an engineering approach, but Silicon Valley believes it as a religious tenet.
 Oct 22, 2026, 1:39 PM
@cstross @davidgerard Code has a genre. I am not convinced the slop machine can write in the obj-cap genre.
I just got a weird flashback to early 90s UK "Whose Line Is It Anyway?" with Mike McShane and Josie Lawrence trying to imitate... stochastic parrots.
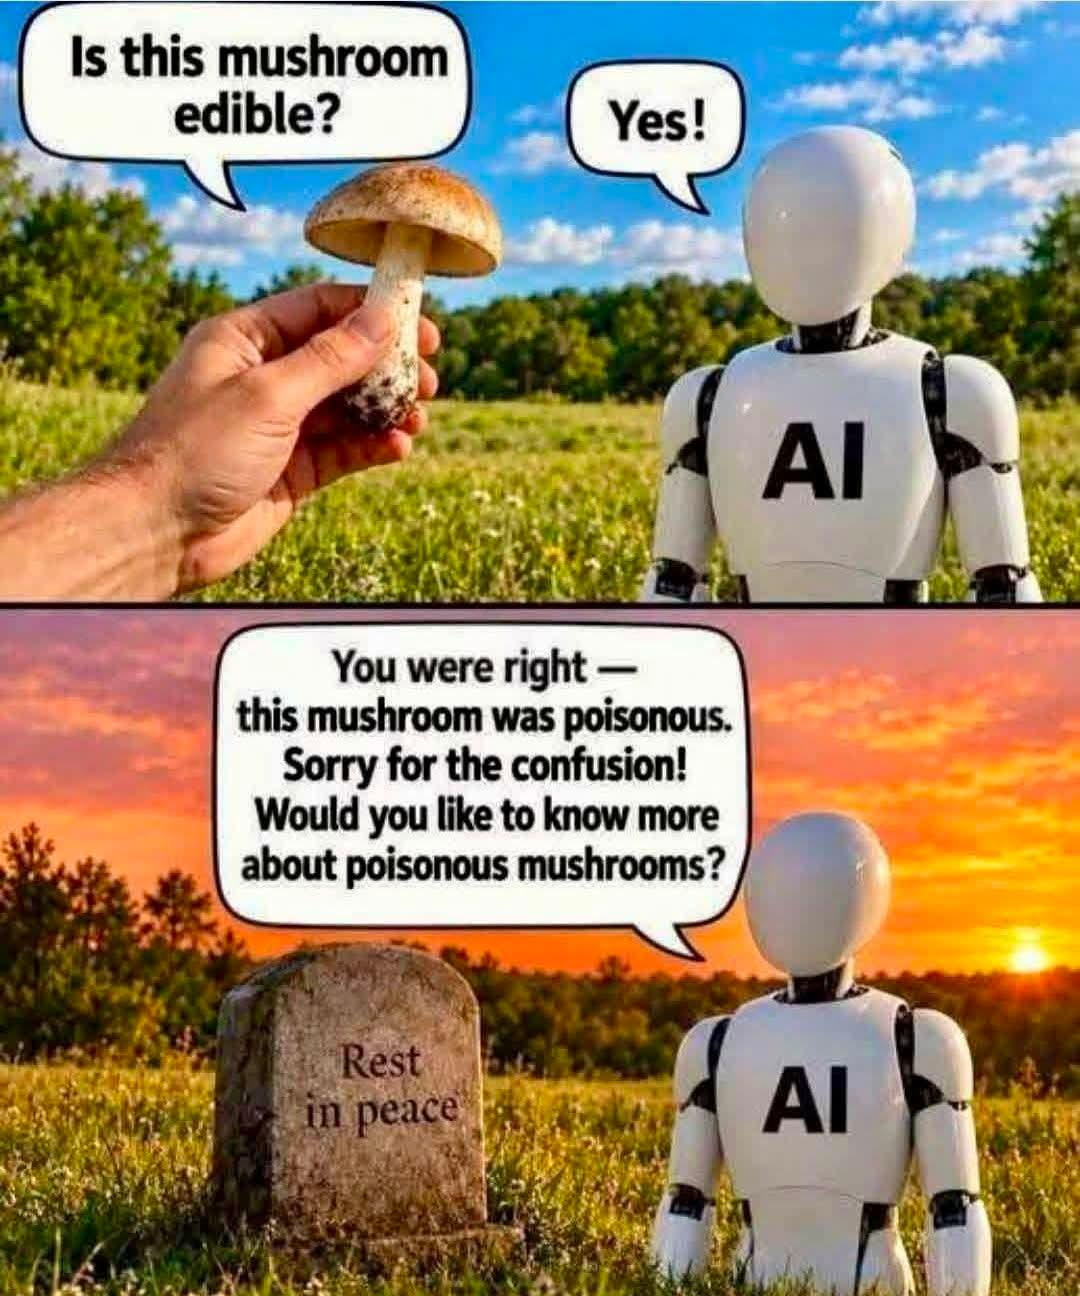
An entire generation of dumb people being told "You're absolutely right!".
That's going to turn out well.
 Oct 22, 2026, 6:57 AM
I prefer to think of it as a nice shift away from the outsourcing and offshoring trend of previous decades. Now we can bring supply-chain attacks back in house.
 Oct 21, 2026, 9:37 PM
@cstross @davidgerard they've apparently been working on it in different teams for an extended period of time.
@cstross @davidgerard bingo

@davidgerard Probably just as vetted as the September Windows Updates were (aka not at all / RDS crashed and burned)
 Oct 21, 2026, 9:16 PM
@davidgerard php team busy at work

 Oct 21, 2026, 9:20 PM
@davidgerard according to the blog post that went with this security release, they've been working on this patch for about 2 MONTHS, so this gigapatch may very well likely be human
Oct 21, 2026, 10:29 PM@davidgerard after seeing some more detailed analysis on the patch I may need to retract my previous toot...
@techokami wondering which human put a little juicing in their code
Oct 21, 2026, 10:32 PM@davidgerard I feel like retreating to the one language not rotted with slop... Motorola 68000 assembly
@techokami @davidgerard “68K, why I haven’t heard that name spoken in years. Takes me back to the 90s, a world where the blue meanies left Easter eggs in code for the underdog platform known as Macintosh, System 7 was still a thing, OS2 was something everyone knew someone who used it but never used it themselves and IE blink was a blight on the world. Ah those halcyon days when CompUSA was a playground of wired mice and $500 CD-R writers…”
 Oct 21, 2026, 9:21 PM
@corbet i just spent my entire day and missed doing today's post/episode because of it, so i'm not enamoured of PHP
i expect the PHP team is not having the greatest day either
 Oct 21, 2026, 9:23 PM
The fix for EOL versions are ~300 lines.
- 7.4: https://github.com/php/php-src/commit/712e60f9edfd03f0960fc4fc3c2c375f42b90aa2
- 8.0: https://github.com/php/php-src/commit/82f8f31b16a035c1b67cc253e79f7cc288f4cc20
- 8.1: https://github.com/php/php-src/commit/1d7dec178a094e6e75b229ce22754045f8c6070a
 Oct 21, 2026, 9:27 PM
@davidgerard It doesn't look LLM generated at first blush, but I'm no longer confident in my ability to tell to be honest. Either way, you could not possibly pay me enough to sign off on +11k -1k over 423 files with most of it being random branches and gotos...
@ne_ @davidgerard It wasn't done in a day, or week, or...
Oct 21, 2026, 10:25 PM@derickr @davidgerard I should hope this wasn't reviewed as one giant change internally. It certainly looks like a lot of human effort went into this. At the same time, could you possibly say to what extent LLM assistance was used? There are some odd-looking comments here and there. session.c:958, oom_rfc1867_mb_encoding.phpt:17,65 and some others.
@ne_ @davidgerard I can't say, because I don't know that.
@ne_ sorry boss, it took a while because I had to wait for the new token billing cycle to roll over
 Oct 21, 2026, 9:39 PM
@davidgerard On an extremely cursory look at the patch diff, the code is of course awful because it's in C, but it looks like human-writen awful C. No obvious AI "tells" have jumped out at me. The tests even appear to test the fixes rather than just print "yeah, everything's just fine, ship it".
It looks like several people have in fact put in quite a heroic effort to fix this, for which they should get a commendation, but it's a shame that they have to waste their talents on this unmaintainable mudball.
@pndc @davidgerard it's awful human written slop like God intended. It brings a tear to my eye. It's beautiful
@pndc @davidgerard oh I have plenty of obvious AI ones when I looked through earlier:
- changed test cases to something different for no reason. I talked about this earlier https://chitter.xyz/@JennyFluff/117479752875775371
- out of memory checks on each iteration of a loop instead of growing the thing first, checking it and then coping over the data
random function return type changes for no reason
- several function return types were changed from void to bool for no apparent reason.
- gates on the newly added return type changed function return true or SUCCESS depending on the file (when if you'd even do that return false at a failed gate!)
- sometimes they handle OOM errors with a goto, sometimes with returns. Sometimes goto statements jump to different labels instead of just oom, like oom_function_name
- sometimes they gate OOM error handling with some other condition that makes no sense
This is a dumpster fire of a patch.
Oct 21, 2026, 10:03 PM@JennyFluff @davidgerard I defer to your greater ability to spot AI, but back in the before times, I saw enough human-written patches that were also all over the slop shop in how they fixed things at each call site.
@pndc @davidgerard yeah I've done 10 years of php in my early IT days, I know and have seen especially bad human slop code
@pndc @davidgerard the thing a human wouldn't do is to change fundamentally what *unrelated* tests test
@pndc @davidgerard I don't understand enough of the structure but pretty sure you could implement a central OOM handler that doesn't return back to your previous code and just crashes.
Trying to add OOM checks on every function (and I cannot verify if they actually managed to do that in a reasonable time) is insane.
Not having the checks standardized is insane.
Just changing some code for no apparent reason in some files that seems to not have anything to do in one security patch commit is insane.
@JennyFluff Even if this isn't straight out of the LLM firehose (lol), this just seems like a complete fucking sprawling incomprehensible mess to throw at a vuln.
+11k lines?!
How is anyone supposed to actually read and understand what's going on?
(oh, right, yeah. feed the code from one text generator, into another text generator for it to generate a "LGTM!")
@Tamber I tried to and the auto-generated fiel by a tool made the most sense
@JennyFluff I'm glad I only have to be stressed about this recreationally.
💭 There I am still pottering about like an amateur, trying to make the most compact, atomic commits I can...
@JennyFluff @pndc @davidgerard time to remake the patch anyone? :p
Oct 22, 2026, 8:40 AM@esoteric_programmer @JennyFluff @davidgerard Sure, I'll just ask Claude. How much worse can it get?
@pndc @JennyFluff @davidgerard the answer, without asking claude
much, much worse. The php interpretor could be forced to emit rendering with a huge html canvass instead of regular elements, for maximum security, speed and blah blah blah,
<insert AI fluff here>