CTI.FYICTI_FYI
1s ago🚨New ransom group blog post!🚨
Group name: Helix
Post title: Sonoco
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/victims/sonoco.html
#ransomware #cti #threatintelligence #cybersecurity #infosec
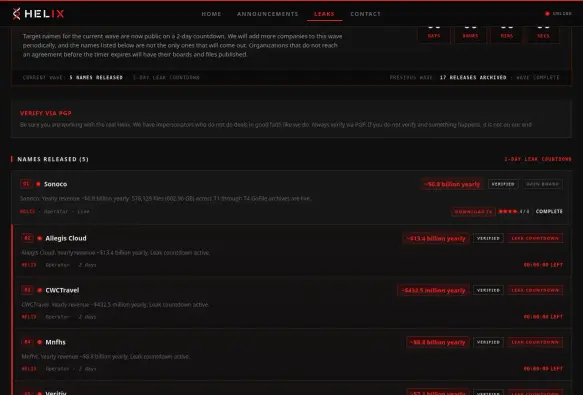
🚨New ransom group blog post!🚨
Group name: Helix
Post title: Sonoco
Location: 🇺🇸 US
Sector: Manufacturing
Info: https://cti.fyi/victims/sonoco.html
#ransomware #cti #threatintelligence #cybersecurity #infosec
Do researchers have to go through an ethics committee for Rorschach tests?
I did one the other day and the pictures they gave me were just filth

current #wallpaper

After Black October, OffSec Turns PHPH2Shell and Other New Vulnerabilities Into Hands-On Labs
New York City, United States, 17th November 2026, CyberNewswire...
🟠 HOCH · Joplin Server: Umgehen von Sicherheitsvorkehrungen möglich
CERT-Bund (BSI)
https://alerts.neonotu.com/de/joplin-server-wid-sec-2026-4605/
⚠️ Exploited in the wild: CVE-2026-115731
Perforce Puppet Enterprise Deserialization of Untrusted Data Vulnerability
Added to CISA KEV · Critical 9.4
Impacted if: Perforce Puppet Enterprise < 2023.8.13 · < 2025.12.1 · < 2026.0.1
https://ax-news.com/cve/CVE-2026-115731
#CVE #KEV #infosec

I will stand athwart history

If you've had glasses made at Lens Crafters, how many times did you have to have them redone?

RE: https://fed.brid.gy/r/https://bsky.app/profile/did:plc:tzy4hibtkautrntsz5f3ns37/post/3n2jc3egnmk2h
Love this: “The point of human society is not business, and it can't be run that way.”
Loi Résilience votée à l’Assemblée : ce qui change vraiment, et ce qui ne change pas encore
L'Assemblée nationale a adopté la loi Résilience, qui transpose NIS2, par 464 voix contre 64. Ce que les députés ont ajouté, les points qui fâchent et ce qu'il reste à attendre.
 3m ago
RE: https://infosec.exchange/@esecurityplanet/117633304028131169
Neither both are shit

fixed!

Another FUD about an OpenJDK RCE vulnverabillity just came out - how do you deal with it?
A title about a 10/10 CVE comes out,
everyone's hands on desk, mapping, chasing people with permission, trying to apply work around or patch if available.
Working like this consumes a lot of time, man-power, stressful, and pushes regular work off.
This method does not feel very sustainable or working for a long run.
Like, what if a new RCE pre-auth was released every-day now? we couldn't work at all.
How do you deal with this scene in your workplace?
Is there a way to escape the race?
I'm seriously asking. I'm quite new at my SecOps Engineer position and it takes all our time and effort every time this comes out.
I'm sure there's some better way to approach this type of issues?
Before that I was Detection Engineer so it was less of an issue for me. Also we just didn't really care.
RE: https://flipboard.social/@newsguyusa/117633248992194330
Last week Microsoft, today Apple...

CVE-2026-84869 in ScreenConnect Exploited to Run Malicious Files on MSP Technician Accounts https://packetstorm.news/news/view/48216 #news

Polygon: The Game Awards announces Game of the Year 2026 nominees https://www.polygon.com/game-awards-2026-nominees-list-game-of-the-year/ @polygon

Don’t just DoS maintainers with raw outputs from your AI vulnerability scanner. In this collaborative work with Microsoft, we filtered 9,791 raw findings down to 99 verified, high-impact, private reports, each with a suggested fix. https://github.blog/open-source/maintainers/maintainers-dont-need-more-ai-bug-reports-they-need-fixes/
Le monde se divise en deux catégories :
- les faibles d'esprit asservis au capital et
- les autres.
— Métapsyché
*giggle* #badvolf

Notion Discloses Third-Party Data Breach Exposing AI Chat Transcripts
Notion confirmed a data breach involving its third-party AI provider, Fireworks AI, that exposed customer AI chat transcripts and sensitive credentials. The company disconnected from the provider, revoked exposed API keys, and notified affected customers.
****
#cybersecurity #infosec #incident #databreach
https://beyondmachines.net/event_details/notion-discloses-third-party-data-breach-exposing-ai-chat-transcripts-r-t-m-5-j/gD2P6Ple2L