Login
You're viewing the discuss.systems public feed.
  • Sep 8, 2026, 12:52 PM

    Here’s the blog post I promised y’all on how I recommend switching password managers in 2026! It covers:
    - why your iPhone or iPad, and not your Mac, might be the place to start your switch
    - when to make the switch and how to treat your “old” app going forward
    - tips and tricks for switching to Apple Passwords, if that’s where you’re going (can be skipped!)
    - the recent controversy in password management and some thoughts on values

    rmondello.com/2026/09/07/switc

    💬 45🔄 337⭐ 480

Replies

  • 💬 0🔄 0⭐ 1
  • 💬 0🔄 0⭐ 1
  • Sep 8, 2026, 1:06 PM

    @rmondello

    Ricky, if I was going to leave #1Password (which I am) and needed a Multiplatform password manager that could sink across all them, what would you pick?

    Current front runner for me is Proton since I'm using their mail and VPN platform.

    (lots of folks giving their opinions lately but I would love your take on who you'd pick )

    💬 2🔄 2⭐ 0
  • 💬 0🔄 0⭐ 2
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 2
  • Sep 8, 2026, 1:18 PM

    @rmondello I ended up, after lots of testing of various alternatives, on Strongbox (Apple friendly front-end for Keepass).

    💬 1🔄 0⭐ 3
  • 💬 0🔄 0⭐ 5
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 8, 2026, 1:42 PM

    @rmondello I was not aware of the secure transfer on iOS. That makes it easy for me switch to Apple Passwords once the 27 OSes are out (still running 15 on my Mac which misses new features there I need)

    💬 0🔄 0⭐ 1
  • Sep 8, 2026, 1:48 PM

    @rmondello
    > Your credentials are yours to take and manage. [...] We just needed to figure out how to enable that in a phishing-resistant way. [...] I’m talking about manually exporting an unencrypted file and [...] that was going to be a non-starter for passkeys because a threat actor could trick someone into exporting their data and then uploading it to them. That’s called phishing.

    So, they're _NOT_ mine to take and manage? I do understand the need for the general population to have these bulletproof anti-foot-gun mechanisms, but, and I don't like having to export to an unencrypted file, but the point about being locked in & controlled by your password manager is still valid because, I don't think 1P or Apple Passwords will give me my passkeys outside of an Apple Approved transfer. If I, a sufficiently savvy user device that, I do in fact want to upload my passkeys to a sketchy website, that should be my own mistake. Computer should not say no.

    💬 0🔄 0⭐ 3
  • 💬 1🔄 0⭐ 3
  • Sep 8, 2026, 3:15 PM

    @leo @tay Computers shouldn’t say no to taylor. But there are so many people losing accounts and money every day due to phishing scams. As a society, we need to protect those people.

    The workaround that vriska describes is available to you.

    💬 1🔄 0⭐ 5
  • Sep 8, 2026, 4:28 PM

    @rmondello @leo Yeah - I don't disagree. And I'll assume you've heard all this before, probably by people who claim this is all some big conspiracy by Big Tech or whatever, which I am not going to do.

    And honestly, I think this is generally me just venting frustration with not being trusted to make my own mistakes, and the greater industry wide concern around power & control, with Passkeys coming about in a time decisions the industry as a whole makes are so often, (often unintentionally) servicing those who wish to seize control from users, and being conveniently useful for those types.

    I do believe that as those who have the power to craft technology, with its great ability to impact humanity for good & bad, we have a duty to serve greater humanity, and I genuinely can & want to believe that the people behind Passkeys et all genuinely have the best of intentions (and have done great work so far), I don't think we, as programmers have done the best job at critically examining & resisting power structures.

    💬 1🔄 0⭐ 1
  • Sep 8, 2026, 4:30 PM

    @rmondello
    For example, recently, the US Administration sanctioned the organisation Autistici/Inventati, for "support[ing] the operations of far-left terrorist networks" - I am not going to discuss the validity of that - but, as a result, their primary domain was seized, and due to the implementation of Passkeys taking away that agency from users, served conveniently to enforce the USGov's decision, as, anyone who set up FIDO based authentication found themselves needing to recover their account

    And of course, yes, requiring account recovery would have been worth it just for the sake of, if it was a phishing site the user went to, would only be given a new (hopefully nowhere-else-used) password.

    And yes, it would be unreasonable to expect your password manager to magically know that this domain is actually the same as another - but with standard passwords,a user was given the freedom to bypass the 'This is the wrong site' warning and hit 'Fill anyway', or just manually copy and paste their password.

    💬 1🔄 0⭐ 1
  • Sep 8, 2026, 4:33 PM

    @rmondello For another example, it used to be common for a website or app to ask for your password for a different site. Of course, I am not going to frame this if it was a good idea, but even now - if an OAuth API is not provided or not sufficient for what a user wants to achieve, acting as the user with their credentials, is literally the only option to make the computer act in the user's favour, but because this is also the way genuinely malicious actors interact with a service, it's easy to lump together all this kind of adversarial behaviour into 'malicious' or 'fraudulent'. And of course, Netflix aren't too happy about user's sharing their password, but I don't think it should be the job of my password manager to protect Netflix' business model.

    And, another thing given the whole Recent Current Event Cycle: I can't backup my 1P vault with Passkeys, so if 1P (or the friend who's family plan I leech off, or the company they work for who provide said plan) suddenly close my account - I'm SOL.

    💬 1🔄 1⭐ 1
  • Sep 8, 2026, 4:36 PM

    @rmondello I understand I'm probably asking a lot for you to even read my wall of text (I could probably have summarised this a lot better than I have) and like. Thinking about this can be very draining (trust me this line of thinking is most definitely not helping my burn out), I don't say all this to be a hater or devalue the work done by the people at FIDO, or anywhere - even with its current flaws it's a great option that I do with I could champion more

    but god. I kinda hate the hole we've dug ourself, and I wish we all (ie. everyone who builds software for a company) were willing to be a bit more proactive in trying to prevent that

    💬 0🔄 0⭐ 2
  • Sep 8, 2026, 2:00 PM

    @rmondello i recently switched from Bitwarden to Apple Passwords. i learned firsthand about the iOS-native transfer functionality when i started off with the “old way” and realized that none of my passkeys moved over 😅

    it bums me out that there’s no Linux or Android support, but right now those OSs are secondary experiences for me and i’m fine leaving them out

    good post!

    💬 1🔄 0⭐ 1
  • Sep 8, 2026, 3:13 PM

    @QuietMisdreavus I recommend Bitwarden for folks who spend non-trivial amounts of time on Linux and Android. Cross-platform, but they put the effort in to be a good platform citizen.

    💬 1🔄 0⭐ 1
  • Sep 8, 2026, 7:20 PM

    @rmondello we’ve moved to Bitwarden at work and I must admit I am *not* inclined to migrate to it. The search only looks for the literal string you type, there are no search operators at all, and it doesn’t search all fields, making it useless for whole swathes of use cases.
    My search for a better alternative continues.

    💬 0🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • Sep 8, 2026, 3:12 PM

    @leo I can’t comment on future plans, but if that’s something that’d make your life better, you are not best served by Apple Passwords today. (I’m personally a fan of Bitwarden because of their cross platform flexibility while being a good citizen on platforms..)

    💬 0🔄 0⭐ 1
  • Sep 8, 2026, 2:43 PM

    @rmondello just tried moving the Apple Passwords (thanks for article). It feels very sluggish and I don't have a crazy amount of things to justify it.

    I miss some features (e.g. archiving instead of deleting), but I could live without it.

    Will try it out some more. Thanks again!

    Image attached toot
    💬 1🔄 0⭐ 0
  • Sep 8, 2026, 7:54 PM

    @fnando @rmondello I switched over from 1P maybe six months ago and have a similar number of passwords, and it is very sluggish, both on iOS and macOS. I like the simplicity of the app compared to 1P, but it feels like molasses.

    💬 0🔄 0⭐ 0
  • Sep 8, 2026, 2:52 PM

    @rmondello omg I had no idea about the iOS thing.

    Oddly my export seems to fail. It doesn’t advance past the screen to choose a compatible app and then when I dismiss I get a “Failed to decode exported credential data” error in 1Password. I wonder if it’s something incompatible in my 1P data.

    💬 1🔄 0⭐ 2
  • Sep 8, 2026, 10:54 PM

    @knowler @rmondello I’ve been working on a (macOS) tool that takes a 1Password export file and does some analysis to help find the edge cases, as well as some audit capabilities to check what has made it over. Early days, but let me know if you want to give it a run. Might help.

    💬 0🔄 0⭐ 0
  • 💬 1🔄 0⭐ 1
  • kΔkDelta@ieji.de
    Sep 9, 2026, 4:47 PM

    @cwalkatron @rmondello Why would you want ‘Trump’ Passwords on Linux? 🤔 I’m no longer using anything like that under the jurisdiction of the USA.

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 8, 2026, 3:45 PM

    @rmondello this is wonderful; thank you!

    I have started the migration away from 1Password to Apple Password. This should be fine in the interim.

    The two things that I don’t necessary like are that, 1.) the idea of the password manager updates tied to OS updates; to me that is a coupling that does not make sense. And 2.) Apple Password is bad at cross browser (Safari is not my primary browser) and cross platform interoperability.

    Again, not really a deal breaker in the short term; but more than likely I will be looking at another migration to something that works better cross platform and cross browser.

    💬 0🔄 0⭐ 2
  • Sep 8, 2026, 3:45 PM

    @rmondello

    Thank you for this!

    I was delaying and thinking too hard about how to transfer.

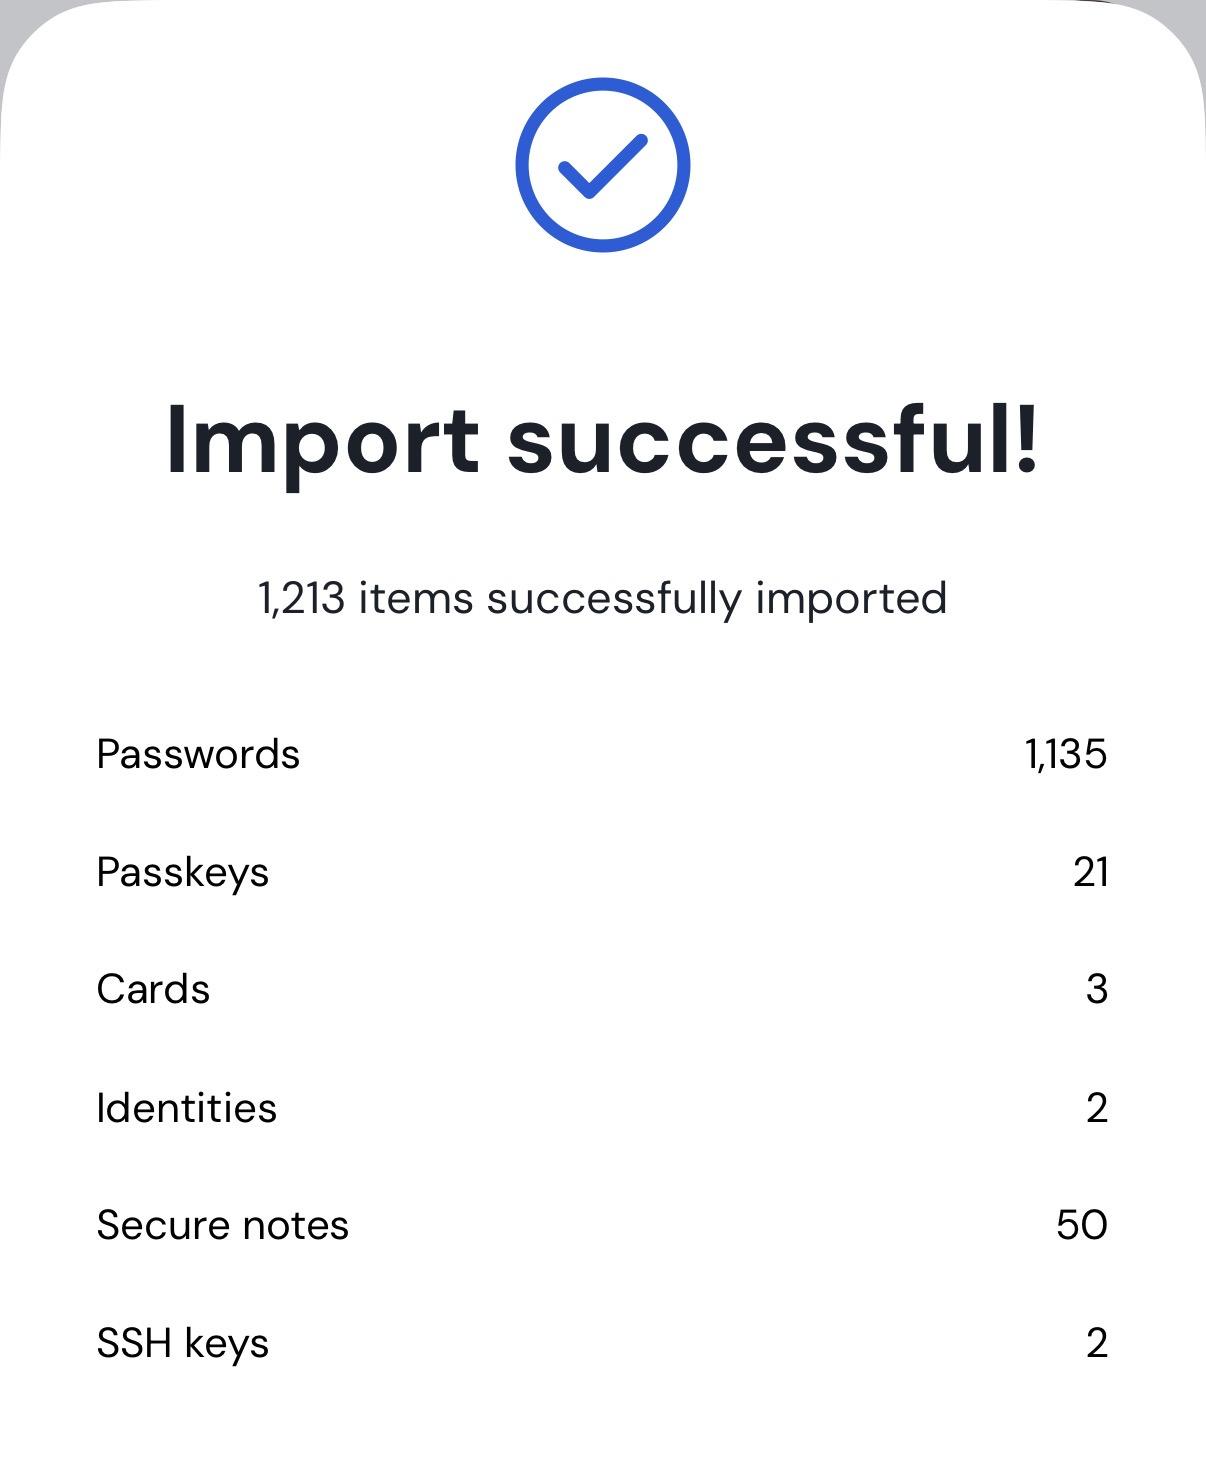
    I had no idea. But this really did make it easy and indeed covered passkeys too.

    Thanks as well for your work making this possible and for sharing your thoughts. Technology, just as society, isn’t morally neutral, agree. (Hence, why I’m interested in this.)

    Bitwarden Screenshot

Import successful!
1,213 items successfully imported
Passwords 1135
Passkeys 21
Cards 3
Identities 2
Secure notes 50
SSH keys 2
    💬 0🔄 1⭐ 2
  • Sep 8, 2026, 3:49 PM

    @rmondello Talking about features, also of other PW managers: 1. There’s an iOS feature that forces Face ID or Touch ID for some access on stolen devices, disabling the device code. Does this extend to the Apple Passwords app? 2. Any chance of getting attachments on a list of possible features? That’s the one reason I use an extra local non-synced keepass db for some secret information.

    💬 0🔄 0⭐ 0
  • Sep 8, 2026, 3:58 PM

    @rmondello I signed up for a year of NordPass and then was immediately blocked from using with work machines due to security policy. NO VPNs. Which is enforced by blocking the authentication websites for VPN services. NordVPN uses the same authentication site for NordPass so blocked. I was advised to use a service that did not offer a VPN service as well 🤦‍♂️

    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • Sep 8, 2026, 5:52 PM

    @rmondello I kept it and told them to provide me with an approved service for work devices. Now they get annoyed because I insist on waiting until I get home to do work that uses my own personal accounts. Which means if I get challenged for my password on GitHub, I have to find alternative things to do until I get home. Stuff gets delayed.

    💬 0🔄 0⭐ 1
  • Sep 8, 2026, 5:59 PM

    @rmondello feature request: a way to have apple password work on Linux. (And maybe make it just a browser extension without local installation)

    💬 0🔄 0⭐ 0
  • Sep 8, 2026, 6:32 PM

    @rmondello I've mostly switched over from 1password 7 installs, just some secure notes/text fields didn't seem to make it over from whatever export file format I outputted from 1password

    Now I just have to sit down and either use iCloud for windows for my windows firefox usage at work, or maybe figure out a way to regularly sync the work entries from Apple Passwords to Firefox's password manager....

    💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 8, 2026, 6:34 PM

    @rmondello Thank you for publishing this. I will probably use it soon.

    As I emailed 1Password, I’m giving it another week, then switching over to Apple Passwords. Would rather not patronize a business that gives DHH money.

    💬 0🔄 0⭐ 1
  • Sep 8, 2026, 6:55 PM

    @rmondello Thanks for this post. How are duplicates handled when importing to Passwords? I have quite a few credentials that exist in both 1P and in Passwords

    💬 0🔄 0⭐ 0
  • Sep 8, 2026, 7:23 PM

    @rmondello Thank you, Ricky, for this post and insight. Great write up.
    I was an early adopter of 1Password, like 2.x. I hated the way they were going and the loss of native iOS and Mac apps settled it. I was on Bitwarden for a while, then switched when Apple released Passwords. I use Uplock and Notes secured with a different password than my Apple Account (ID). However, like you, I still have an old version of 1Password hanging around.

    💬 0🔄 0⭐ 1
  • 💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 2
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 1
  • Sep 8, 2026, 7:38 PM

    @rmondello great post, thanks! I am considering this move for my family. How does Apple passwords handle one-time passwords that update every ten seconds?

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 8, 2026, 8:21 PM

    @rmondello thank you Ricky! Who would have thought that I am now, in the nick of time, motivated to update to iOS 26!

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 8, 2026, 9:36 PM

    @rmondello This is an issue for me: The Passwords app unlocks using Face ID, Touch ID, or your device passcode or Mac login password. You cannot set a different “master” password.

    My 1P master passphrase is much stronger than my device passcode or login password. Is there a sound argument for why it doesn’t need to be?

    💬 1🔄 0⭐ 4
  • Sep 13, 2026, 7:09 AM

    @jpallas @rmondello
    Because (my understanding):
    - if you Mac gets hacked it’s game over (key loggers, screen loggers)
    most
    - account recovery is usually via e-mail, and if the attacker has access to email on your device…

    💬 0🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 1
  • Sep 8, 2026, 10:52 PM

    @rmondello Is there any chance of getting Apple Passwords to provide a list of items imported and items skipped, with a reason as to why? I’ve found that I’ll send (say) 100 items, 50 are added to Passwords and 50 just vanish. I then have to manually audit to work out why.

    On the Apple side of the CXF fence, it would also be amazing if it could handle things like credit cards (automatically add to Wallet Autofill) and secure notes (add to Notes).

    Actually expand that last bit: take anything textual and add to Notes, and tag it with the source data type.

    💬 0🔄 0⭐ 2
  • Sep 8, 2026, 11:48 PM

    @rmondello this is great! I love the tone and the humility of it. I can share this with my family and not feel weird. Nice work!

    💬 0🔄 0⭐ 1
  • 💬 0🔄 0⭐ 1
  • Sep 9, 2026, 5:43 AM

    @rmondello great blog post. My question if there is a good and secure solution to make a backup of your passwords? My horror is if something happens and I’m locked out of my Apple account…..

    💬 1🔄 0⭐ 1