Login
You're viewing the functional.cafe public feed.

Replies

  • Nov 3, 2026, 6:00 PM

    Root-based remote attestation of client devices against the user's interests should simply be illegal in any liberal democracy, just like how selling user data without consent or exfiltrating user data to hostile foreign countries is. There is legitimate use for this technology for the user to attest a server, or for one of your devices to verify the other (as e.g. GrapheneOS allows you to do), but this kind of use of the tech must stop.

    💬 4🔄 48⭐ 103
  • Nov 3, 2026, 6:02 PM

    If the web were (re-)invented in 2026, I bet every website would just restrict which browser you can use to access their site for "security" with remote attestation (because, I guess, Servo doesn't support secure secrets storage, or something). That's not a world we should have to live in.

    💬 6🔄 22⭐ 87
  • Nov 3, 2026, 6:21 PM

    @pojntfx And we will soon be in it, as "Passkeys" allow for precisely that and "everyone" is pushing them now.

    💬 2🔄 0⭐ 2
  • 💬 0🔄 0⭐ 0
  • Nov 3, 2026, 7:43 PM

    @divVerent @pojntfx

    I'm sorry to say but this is already starting to happen with Google's new reCaptcha system, and worse because instead of passkeys you have to use your Android or iOS device - cybersecuritynews.com/google-r

    > The reliance on this specific application suite means the verification process heavily utilizes hardware attestation, tying basic web accessibility directly to Google’s proprietary mobile ecosystem rather than simple behavioral analysis.

    💬 1🔄 8⭐ 11
  • Nov 4, 2026, 4:19 PM

    @futureisfoss @divVerent @pojntfx exactly this. They don't need any standards like fido to tie everything to remote attestation. The whole anti passkey propaganda is so infuriatingly missing the point and focusing and the wrong thing.

    💬 0🔄 0⭐ 2
  • 💬 0🔄 0⭐ 2
  • Nov 3, 2026, 6:46 PM

    @pojntfx It's a bit different for browsers because you can freely install an actually good browser on any device (a check for a certain API or feature would go by engine not browser), you can't freely relock your bootloader on most phones and no custom OS can freely get verified by Google.

    Edit: also, secure cookie storage is kind of a big deal, nobody should use browsers that can't store session data properly.

    💬 1🔄 0⭐ 2
  • Nov 3, 2026, 8:09 PM

    @asterisk Agree re:you not using an insecure browser, obviously. Remote attestation of the device running a browser was actually attempted by Google as something to be introduced as a web standard but thankfully failed, to work around this they are now doing it via reCaptcha (which requires an Android device with a locked bootloader, Google account, and OS image signed by Google)

    💬 1🔄 3⭐ 4
  • Nov 4, 2026, 3:13 AM

    @pojntfx And Mozilla wants to bring it back to life but using your activity on other sites instead (judged by a third-party moderator): hacks.mozilla.org/2026/06/pact

    the reCAPTCHA thing isn't quite true, the bootloader only needs to be locked and Play Services needs to be installed, it works on GrapheneOS. It's also a bit iffy and you're still not asked to mobile verify very often (if the automated half thinks you're not a bot you won't be asked), plus reCAPTCHAv2 is being phased out and replaced with Cloudflare Turnstile and hCAPTCHA.

    💬 0🔄 0⭐ 1
  • Nov 3, 2026, 8:41 PM

    As I wrote on a certain "professional networking" site 4 days ago:

    "...big commerce is now trying to persuade us to use proprietary apps on the desktop.

    I'm calling it now: under web 4.0 there will be no major generic web sites, and the browser's principal function will be to download and install a site's dedicated application and give it the freedom to mine the device and offload as much of the site processing costs onto the user as it can."

    @pojntfx

    💬 0🔄 3⭐ 6
  • Nov 3, 2026, 11:00 PM

    @pojntfx it depends on who reinvented it. if it were me:
    - no client-side javascript; use CSS or do the work server-side, you lazy sods.
    - real end to end encryption; i'm sure we can somehow do better than trusting certificate issuers. "4", right, well done.
    - trivial self hosting and federation of simple web pages; back to little blogs.

    💬 1🔄 0⭐ 1
  • Nov 3, 2026, 11:31 PM

    @fishidwardrobe @pojntfx TLS *is* E2EE in that only you and the recipient server can read the message. "4" played no role in the encryption part, but in the identification part, which E2EE doesn't solve in any way

    💬 0🔄 0⭐ 5
  • Nov 4, 2026, 11:05 AM

    @pojntfx
    I mean, in a way the "lite" version happens on all the pages that use chromium-exclusive features that break on all non-chromium browsers. To be fair, there aren't that many of them, but it still happens on occasion.

    "Your browser is not supported, please use a browser like Google Chrome, Edge or Opera and try again" is a message that frustrates me to no end.

    💬 0🔄 0⭐ 0
  • Nov 5, 2026, 4:48 AM

    @pojntfx @joepie91 We are already good on our way of having this! We already have these licenses you need to renew every month to be allowed to operate a website. I think it’s called TLS certificate or something. They can be issued by any organisation authorised to do so by a few American companies.

    💬 0🔄 0⭐ 0
  • Nov 3, 2026, 7:16 PM

    @pojntfx

    > Root-based remote attestation of client devices against the user's interests should simply be illegal in any liberal democracy

    Oh my god this! I've been screaming about this ever since I learned about this practice. A lot of what Android and iOS are doing these days are straight up anticompetitive practices and should be illegal.
    1/2

    💬 1🔄 1⭐ 7
  • Nov 3, 2026, 7:16 PM

    @pojntfx

    I would also like to mention Google's developer verification policy on Android, this will kill off alternative app distributors like f-droid and make Google the sole arbiter who can decide which apps you're allowed to run on your phone, see more info here - keepandroidopen.org

    Also their new plan for the reCaptcha system - cybersecuritynews.com/google-r

    If implemented then every website using Google's reCaptcha system would be inaccessible to anyone who doesn't use Android or iOS

    2/2

    💬 0🔄 1⭐ 5
  • Nov 4, 2026, 8:27 AM

    @pojntfx In Austria for the id app, they do the remote attestation, but if it fails they don't block you from using it but just give you a big warning once that something is weird about your device and you should only continue if you know what you are doing.

    💬 0🔄 0⭐ 1
  • Nov 4, 2026, 4:20 PM

    @pojntfx

    Apparently no digital drivers license on GrapheneOS. @AwetTesfaiesus I think I saw you tooting about using it some time ago so this might be interesting to you.

    💬 1🔄 0⭐ 1
  • Nov 4, 2026, 5:09 PM

    @soeren @pojntfx i Do.

    But as with payment I am having trouble to see the use in using the Phone for this in the first place really. I tend to believe that we should emphasize/safeguard the use of offline methods of interaction. Not a set in stone opinion though.

    💬 0🔄 0⭐ 1
  • 💬 0🔄 0⭐ 2
  • 💬 0🔄 1⭐ 3
  • 💬 1🔄 0⭐ 4
  • Nov 3, 2026, 6:55 PM

    @pojntfx
    Off topic a bit but with digital IDs, Germany can kiss its sovereignty goodbye. I believe digital IDs and cashless societies to be a complete submission to transnational corporate tech evilcorps. Even if run on EU servers by todays good guys, it is still irresistible totalitarian power on a silver platter for tomorrow's dictators.
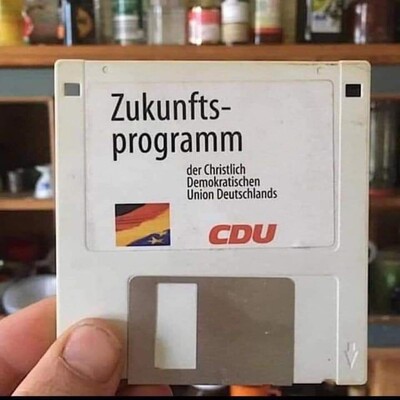
    If we let society do away with all things physical and blindly trust corporate databases, i will bet everything i have on this incredible power being so deeply abused, we enter a new dark age. With a few clicks from our future dictators, anyone can be utterly erased from existence and the thugs sent out to burn the evidence. Nobody will even know it happened because journalism wont exist. How could it anyone speaking truth to power can be so efficiently erased?

    Use real things people. A plastic ID card is proof that you existed. Cash is freedom from surveillance. When they say "card payment only" walk away.

    💬 0🔄 4⭐ 9
  • 💬 0🔄 0⭐ 1
  • 💬 0🔄 0⭐ 1
  • Nov 3, 2026, 7:23 PM

    @pojntfx because people with an Android or Apple phone should not be allowed to have a digital drivers license and let Apple/Google wallets dominate? That would be even worse.... I am all for getting rid of Bigtech but that transformation takes time...

    💬 2🔄 0⭐ 1
  • Nov 3, 2026, 11:54 PM

    @ErikJonker @pojntfx why is “people are not allowed to use it on these two OS” the only alternative to “people are only allowed to use it on these two OS”?

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 2
  • 💬 0🔄 0⭐ 0
  • Nov 3, 2026, 7:38 PM

    @pojntfx Why do politicians rant about physical borders and sovereignty but fail to understand digital sovereignty? Google and Apple backed by a rogue US govt are far more dangerous than a few thousand impoverished immigrants seeking refuge.

    💬 0🔄 3⭐ 8
  • Nov 3, 2026, 7:59 PM

    @pojntfx my Brazilian digital driver's license works with LineageOS, not sure if it was working before or after installing MicroG tho.

    💬 1🔄 0⭐ 0
  • Nov 3, 2026, 8:05 PM

    @Lodhal Yeah this is less about Google Play services (which are a bummer to require too, tbc, but like you say that can be solved w/ MicroG), it's about remote attestation with the Google signing keys not being a gate that any OS that's not allowlisted can pass, including much more secure ones than the default Android OS vendored by e.g. Google or Samsung (such as GrapheneOS)

    💬 0🔄 0⭐ 2
  • 💬 0🔄 0⭐ 1
  • 💬 2🔄 0⭐ 3
  • Nov 3, 2026, 8:23 PM

    @pojntfx

    How wonderful! 🤨🤦‍♂️

    The UK keeps threatening to release an app for ID cards and Licences but it never seems to happen.

    💬 0🔄 0⭐ 2
  • Nov 5, 2026, 7:35 AM

    @pojntfx @simonzerafa the whole system is really bizarre...
    If the attestation is remote, a valid request should be accepted and validated: so they grant a result no matter who's asking. Like a server side verification.
    If the attestation is local you need to certify the whole system otherwise it can be manipulated.
    If you need both... the server side is not secure enough?

    And then, I really do not believe that the German government does not have good enough engineers to deploy such a system.

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 3
  • Nov 3, 2026, 8:30 PM

    @pojntfx Denmark made a similar choice with the national digital ID, MitID. Lots of talk about digital sovereignty, but in the end they still let Google be the gatekeeper.

    At least they also included the option of a physical key generator, but it's nowhere near as convenient.

    💬 0🔄 0⭐ 0
  • Nov 3, 2026, 8:31 PM

    @pojntfx

    Google & Apple have fossil fuel funded fascist overlords ... ahem... "investors" to placate

    businessinsider.com/saudi-arab

    bloomberg.com/news/articles/20

    The German government handed #PrinceBonesaw the reins of their democracy to the oil industry

    "Joint projects" lol
    english.alarabiya.net/amp/News

    Oil oligarchs & tax-evading technofascists in charge of government infrastructure; such a bad idea

    They don't want to be taxed because taxes involve compliance reporting & transparency on the money

    1/

    💬 1🔄 4⭐ 3
  • Nov 3, 2026, 9:42 PM

    2/

    Germany is forgetting that anything using an American tech platform is a national security vulnerability.

    What happens if Putin invades & EU identity confirmations are hacked, altered, or shut down?

    What happens if Putin invades German airspace & Musk shuts down starlink again?

    What happens if Trump, on a whim and in a fit of pique, imposes sanctions on Germany's officials?

    The oil industry, Russian, Middle Eastern, & Koch Network are engaging in economic warfare & influence peddling

    💬 1🔄 8⭐ 9
  • Nov 4, 2026, 9:23 AM

    @Npars01

    I no longer believe that our German government is "just" ignorant.

    I'm starting to think they are actively sabotaging German sovereignty in favor of the tech bros and the fossil fuel industry.

    💬 0🔄 3⭐ 2
  • Nov 3, 2026, 8:33 PM

    @pojntfx

    > Alternative Android-Systeme ohne nachinstallierte Google-Dienste wie LineageOS oder GrapheneOS unterstützt die App offenbar nicht, auf Huawei-Geräten und älteren Motorola-Modellen läuft sie laut BMV ebenfalls nicht.

    Lol, yea okay so just not for use!

    CURRENTLY I own and use an Android-Phone with play services but I do not want to be dependend to those.

    So dear Kraftfahrbundesamt: Just do it again, this time in FLOSS!

    💬 0🔄 0⭐ 2
  • 💬 0🔄 0⭐ 1
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Nov 3, 2026, 10:39 PM

    @pojntfx when this stuff eventually rolls around to my country, I'll just not have a smart phone (or any phone). The assumption that a device I own can be forced to be used by anyone else than myself at my choice, is bonkers.

    Wife's work rolled out MFA and everyone had to install thw Microsoft 2FA app.
    Wife refused; its her personal device.
    Everyone at her work thought she was making big deal about it at the time, then months later realised they have this thing that means they have to take their phone to work because it is tied to them be able to do their job.

    💬 0🔄 0⭐ 0
  • Axeltetrapyloctomist@muenchen.social
    Nov 3, 2026, 11:35 PM

    @pojntfx
    Haven't you what Merz told the German public the other day?

    You're failing to realize that just because it's based on Google's cloud services, it doesn't mean that it's not a souvereign system! :mastoface_with_rolling_eyes:

    💬 0🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Nov 4, 2026, 7:45 AM

    @pojntfx das Gute an dieser "digitalen" Fahrerlaubnis ist, dass sie nur auf mit Spyware von Google ausgestatteten Handys läuft und man sie letztendlich nicht braucht. Interessant wäre hingegen, wenn sie derart mit der Spyware des Autos verknüpft wäre, dass die Karre sofort am Straßenrand anhält, sobald wer auf dem Display herumtippt, und die Fahrerlaubnis dann automatisch erlischt.

    💬 0🔄 0⭐ 0
  • 💬 1🔄 0⭐ 1
  • Nov 4, 2026, 8:18 AM

    @Saupreiss @pojntfx

    Most likely they had no ideas at all except "it has to be digital", and tech lobbyism did the rest. This is all so deeply, frustratingly, dangerously unserious ... I could scream.

    💬 0🔄 0⭐ 1
  • Nov 4, 2026, 8:29 AM

    @pojntfx true that we must not tie this to the two big platforms, and we must do our best to open that up. However, in the meantime, there still is an alternative: "Für Fahrten ins Ausland bleibe die bisherige physische Version jedoch erforderlich."

    💬 0🔄 0⭐ 0
  • Nov 4, 2026, 9:20 AM

    @pojntfx denmark did this a year or two ago, as well as a digital version of the national health card

    fortunately the digital versions are still optional (de facto as well as on paper) for now

    💬 0🔄 0⭐ 0
  • Nov 4, 2026, 10:09 AM

    @pojntfx Anything we could do to ban such a practice? If Microsoft has been sued for preferring Edge, and Apple has been forced to allow other browser engines... This is vastly more serious and far reaching

    Anything we could do under anti-competitivity laws? Maybe with @noybeu or @edri

    To be clear :

    Server attests server - > 🆗
    Device attests server - >🆗
    Device attests device - >🆗
    Server attests device - > 🙅⛔🚫

    💬 0🔄 0⭐ 0
  • 💬 0🔄 1⭐ 0
  • Nov 4, 2026, 11:12 AM

    @pojntfx I'm currently having a long e-mail discussion with my Dutch bank ASN (trying to get beyond boilerplate answers) because they are switching from iDEAL to Wero and require remote attestation for Wero transfers.

    Play Integrity-based attestation seems to get adopted very rapidly (also: the Volkswagen app, IKEA SmartHome, etc). And the @EUCommission and DMA team seem to be sleeping.

    I fear the only way to make progress is if someone sues Google for anti-competitive practices.

    💬 1🔄 0⭐ 0