BrianKrebsbriankrebs@infosec.exchange
Nov 5, 2026, 4:39 AMNew, from me:
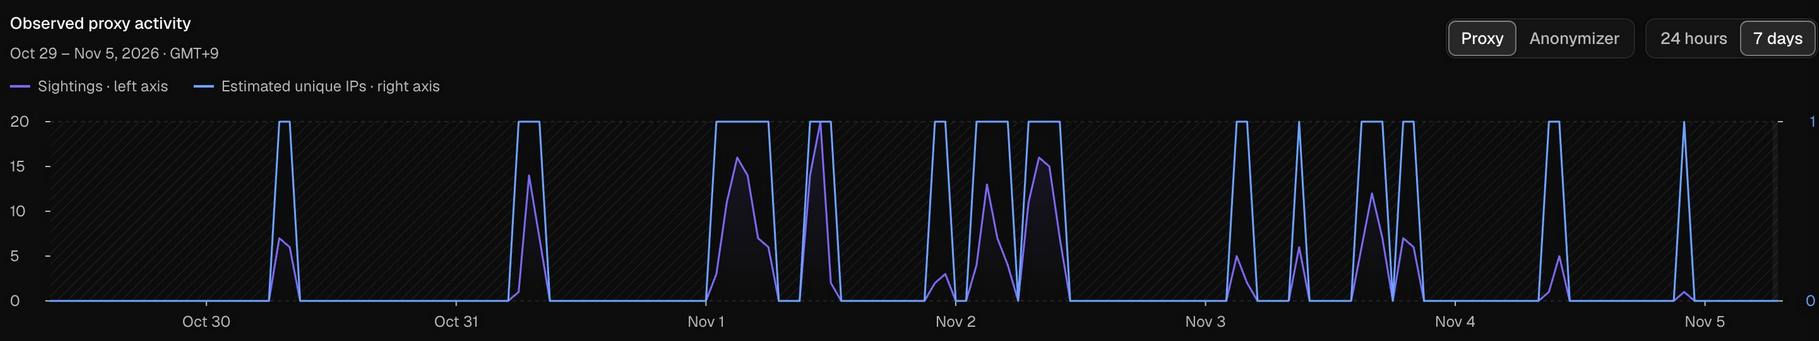
Several staffers at the White House are using computers or mobile devices equipped with residential proxy services that render their internet address available for others to rent, security experts warned today. One of the proxy services is a Russian company whose founder’s web hosting business was ground zero for cyberattacks against election systems in Arizona and Illinois in 2016.
https://krebsonsecurity.com/2026/11/want-to-rent-an-internet-address-at-the-white-house/