So this Nightmare Eclipse / MSNightmare FastUnlock is sort of a neat code-free parlor trick. But at the end of the day, just another semi-yawn-worthy demonstration of CERT/CC VU#789985.
The gist is:
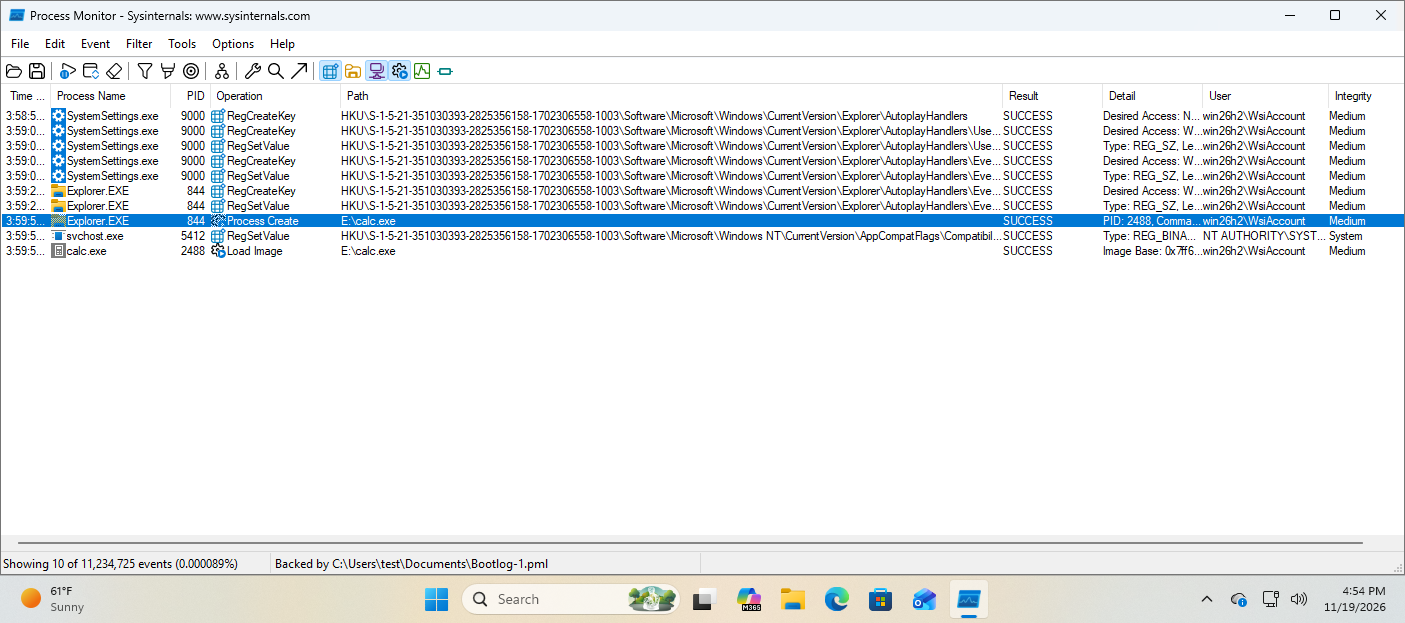
The ephemeral WsiAccount Windows account that is created/used during Windows login-screen login prompts is accessible via Windows Narrator. What makes it abusable is that when Narrator is launched, its focus is on the off-screen components of itself. That is, while you can't see the WsiAccount things running, they're indeed there. Using a bit of Narrator-style navigation through these off-screen dialogs, we can:
- Launch Windows
SystemSettings.exe - Set the preference for the
WsiAccountto automatically display in Explorer the contents of newly connected USB mass storage devices. - Run any program in this new Explorer window that has popped up.
The writeup states:
this breaks the guarantee that a properly secured bitlocker machine cannot be accessed even if the attacker has physical access
But I can't really find any record of Microsoft promising such things. If you have a TPM-only BitLocker configuration, Windows automatically decrypts the hard disk so that it can load. I don't think there's anybody who believes that bitlocker is still in play at the point where Windows is prompting you for credentials. So to suggest that this is a BitLocker bypass is a bit misleading.
What it is is a way to run arbitrary code on a Windows system without needing to log into it, provided that the account has at least one Microsoft Account configured on it. And as a medium-integrity WsiAccount user. BitLocker is completely irrelevant to anything used in the attack.