Login
You're viewing the mastodonapp.uk public feed.
  • Oct 21, 2026, 10:13 PM

    If this had been a woman in a senior dev, security or SRE position, she would not have concluded this with an inspiring LinkedIn post about "not always getting it right".

    This guy is the CEO of Chainguard by the way.

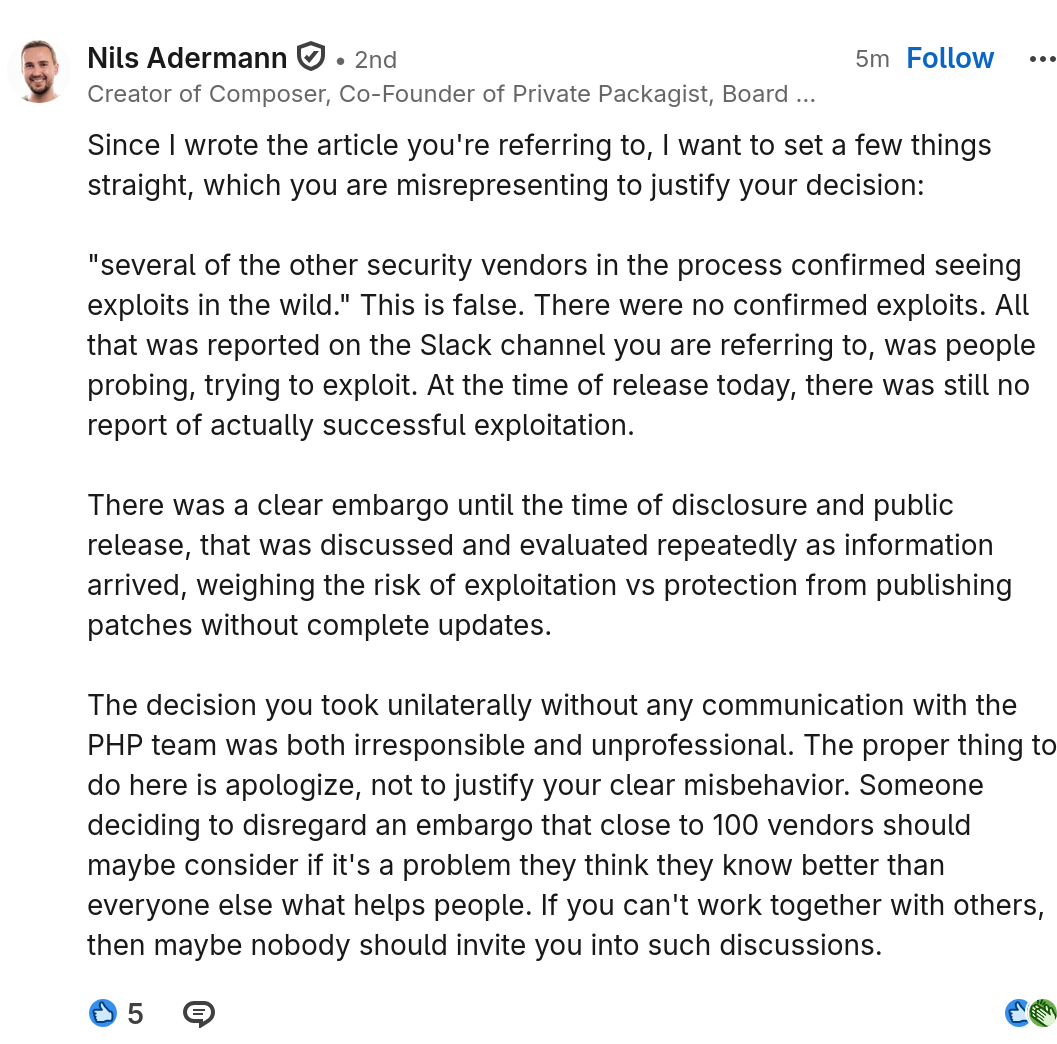
    I hope that this causes Chainguard to be kept away from any security related embargoes until trust has been properly restored.
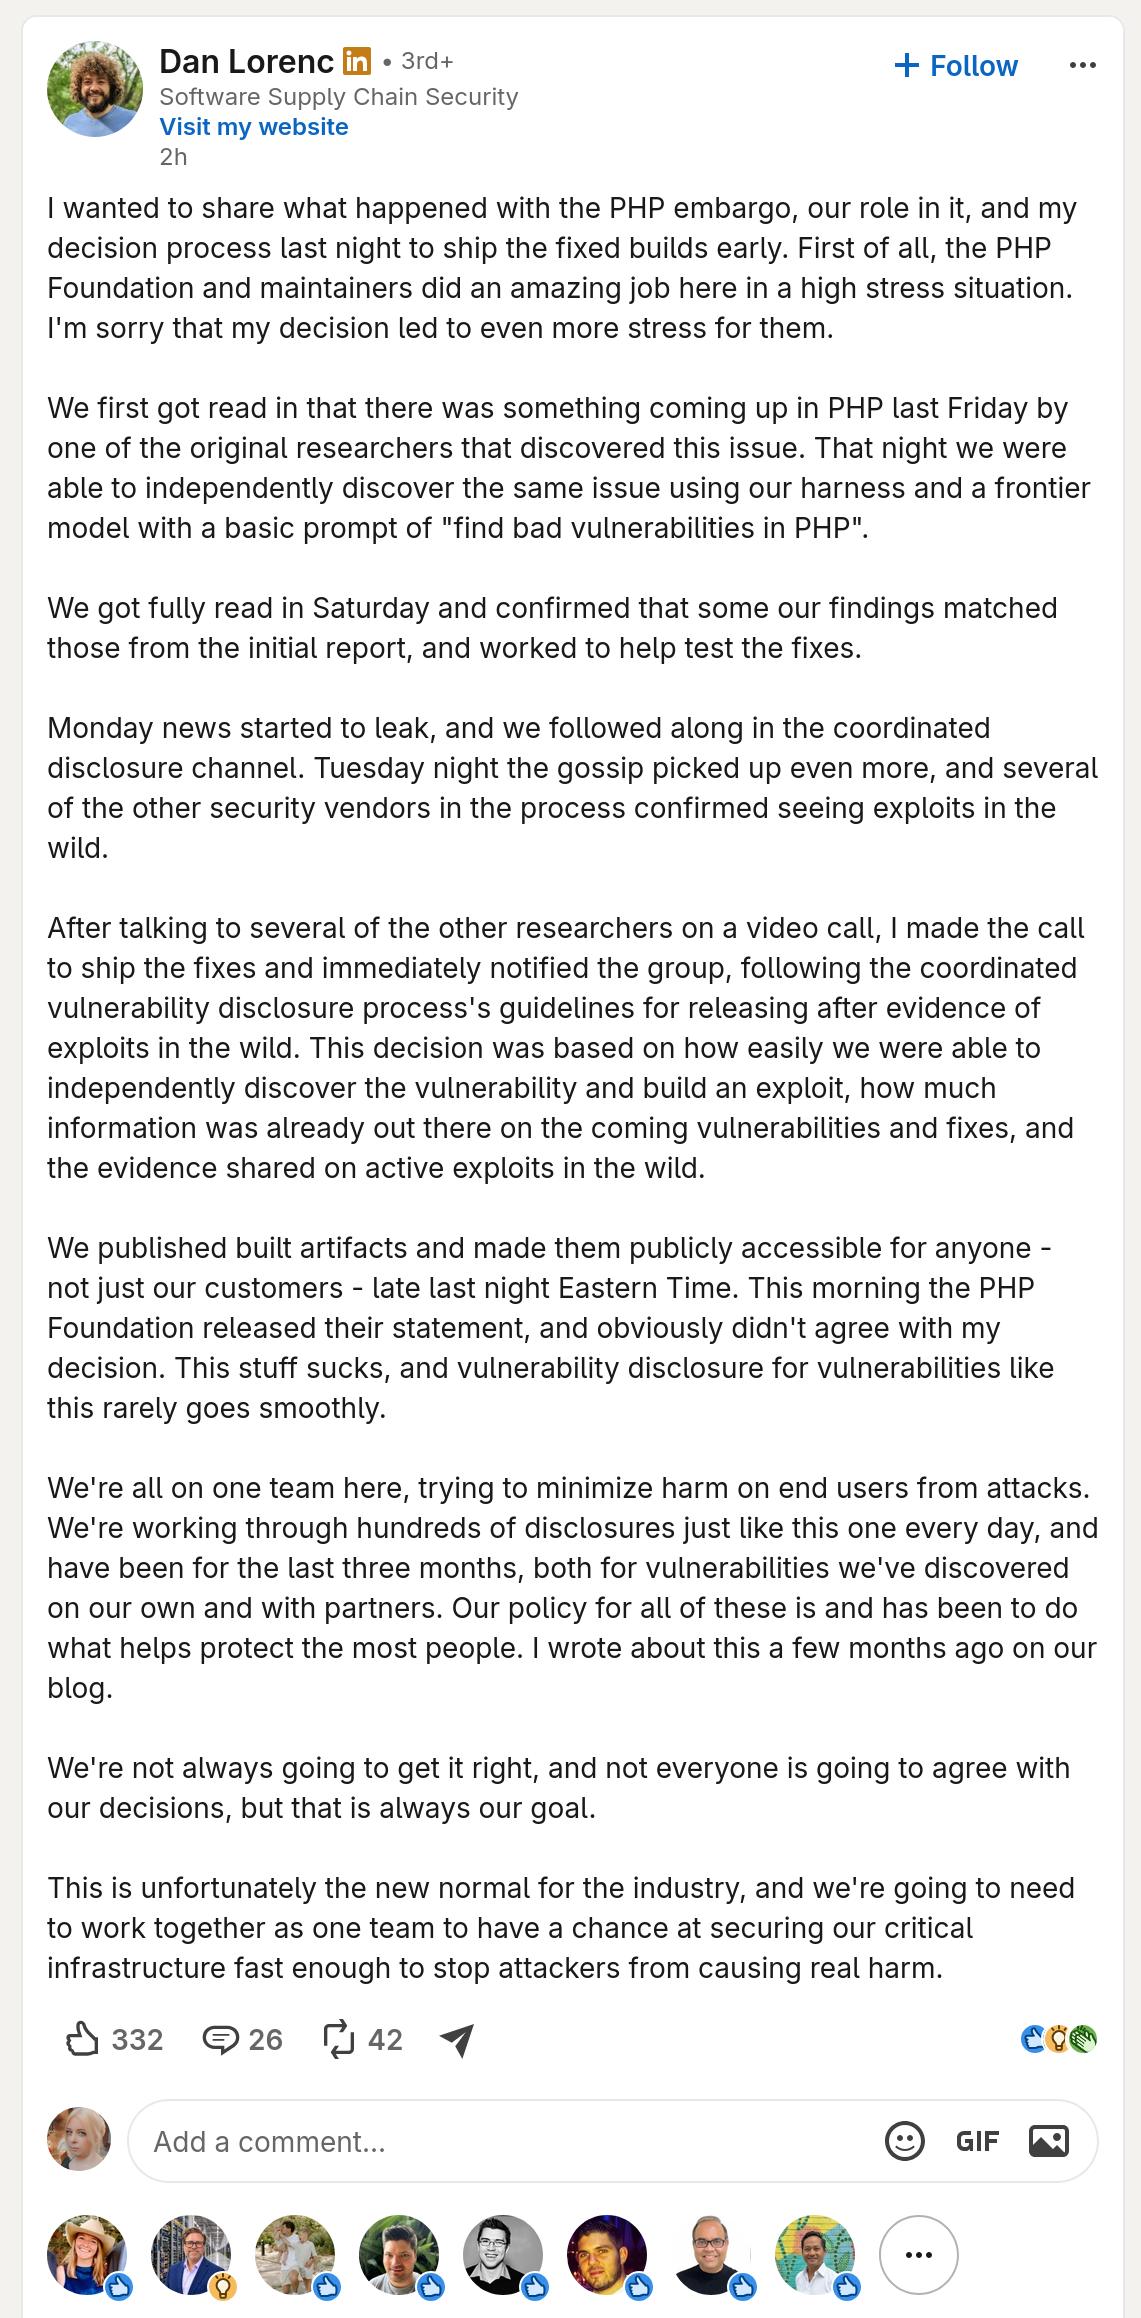
    A screenshot from a LinkedIn post from Dan Lorenc:

I wanted to share what happened with the PHP embargo, our role in it, and my decision process last night to ship the fixed builds early. First of all, the PHP Foundation and maintainers did an amazing job here in a high stress situation. I'm sorry that my decision led to even more stress for them.

We first got read in that there was something coming up in PHP last Friday by one of the original researchers that discovered this issue. That night we were able to independently discover the same issue using our harness and a frontier model with a basic prompt of "find bad vulnerabilities in PHP".

We got fully read in Saturday and confirmed that some our findings matched those from the initial report, and worked to help test the fixes.

Monday news started to leak, and we followed along in the coordinated disclosure channel. Tuesday night the gossip picked up even more, and several of the other security vendors in the process confirmed seeing exploits in the wild.

After talking to several of the other researchers on a video call, I made the call to ship the fixes and immediately notified the group, following the coordinated vulnerability disclosure process's guidelines for releasing after evidence of exploits in the wild. This decision was based on how easily we were able to independently discover the vulnerability and build an exploit, how much information was already out there on the coming vulnerabilities and fixes, and the evidence shared on active exploits in the wild.

We published built artifacts and made them publicly accessible for anyone - not just our customers - late last night Eastern Time. This morning the PHP Foundation released their statement, and obviously didn't agree with my decision. This stuff sucks, and vulnerability disclosure for vulnerabilities like this rarely goes smoothly. 

We're all on one team here, trying to minimize harm on end users from attacks. We're working through hundreds of disclosures just like this one every day, and have been for the last three months, both for vulnerabilities we've discovered on our own and with partners. Our policy for all of these is and has been to do what helps protect the most people. I wrote about this a few months ago on our blog.

We're not always going to get it right, and not everyone is going to agree with our decisions, but that is always our goal.

This is unfortunately the new normal for the industry, and we're going to need to work together as one team to have a chance at securing our critical infrastructure fast enough to stop attackers from causing real harm.
    💬 10🔄 47⭐ 25

Replies