Login
You're viewing the mastodonapp.uk public feed.
  • Sep 26, 2024, 8:02 PM

    So this "CVSS 9.9" "unauthenticated RCE vs all GNU/Linux systems (plus others)" thing...

    - Does NOT affect all GNU/Linux systems.
    - Is not CVSS 9.9. I put it at a 6.3

    It also requires:
    1) The victim system has no active firewall to block incoming connections.
    2) A user on the victim system must print something to a printer that mysteriously appears on the system that has never been there before.

    If these two things happen, then command execution can happen as the "lp" user.

    <yawn>

    We get it. You found a vulnerability.
    Lying about it to try to stir up interest in it is not appreciated by anybody who takes themselves seriously in this industry.

    CVE-2024-47176, CVE-2024-47076, CVE-2024-47175, and CVE-2024-47177 have been assigned.

    evilsocket.net/2024/09/26/Atta

    Image attached toot
    Image attached toot
    💬 16🔄 80⭐ 0

Replies

  • Sep 27, 2024, 1:27 PM

    This CUPS thing is a great example of how not to do vulnerability coordination/disclosure.

    Even the CVE assignment is a failure. An independently fixable vulnerability gets a CVE. It's quite simple. It's a number that you assign to a vulnerability.
    cve.mitre.org/cve/list_rules_a

    GitHub (the CNA) for CVE-2024-47176:
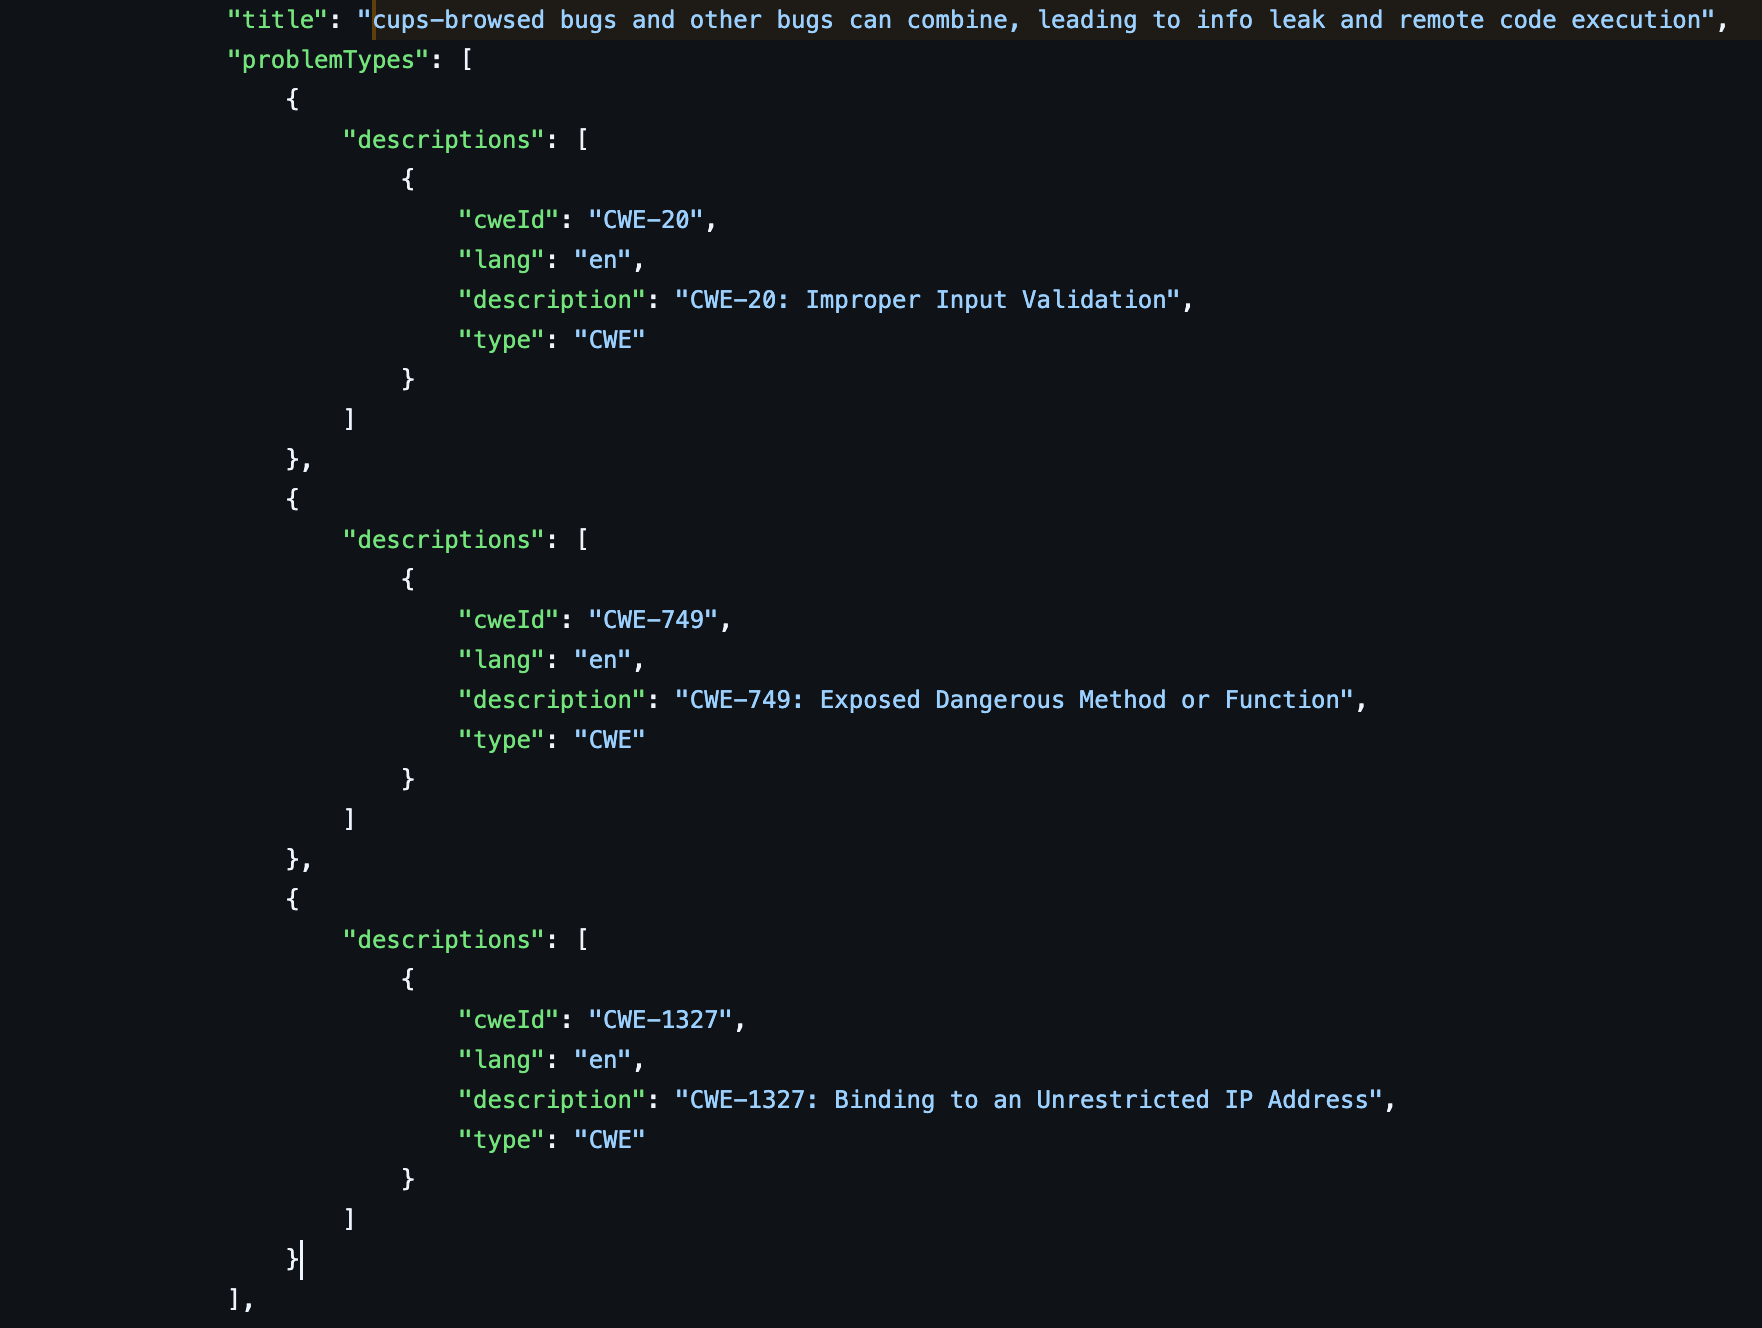
    "cups-browsed bugs and other bugs can combine, leading to info leak and remote code execution"
    (lists three COMPLETELY UNRELATED CWEs)

    You don't just assign a meta CVE for a set of different vulnerabilities because it's easier. 🤦‍♂️

    Image attached toot
    💬 1🔄 6⭐ 0
  • Sep 27, 2024, 2:09 PM

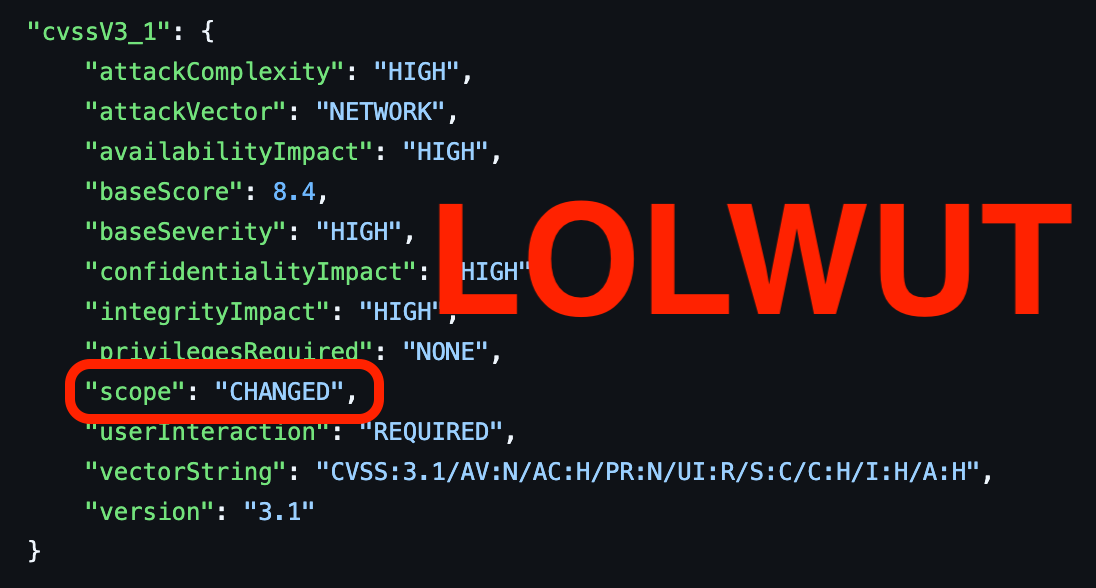
    Or even the CVSS part of the CVE is highly inaccurate. GitHub gives it a 8.4, but I give it a 6.3 to the entire attack chain. Or if we follow CVE rules and have only one vulnerability per CVE, I'd give it a 5.3.

    "scope": "CHANGED" ?

    Get real! That sort of thing gets assigned to hypervisor escapes and the like, where resources beyond the security manager of the affected component can be modified. This vul allows assisted command execution as the "lp" user.

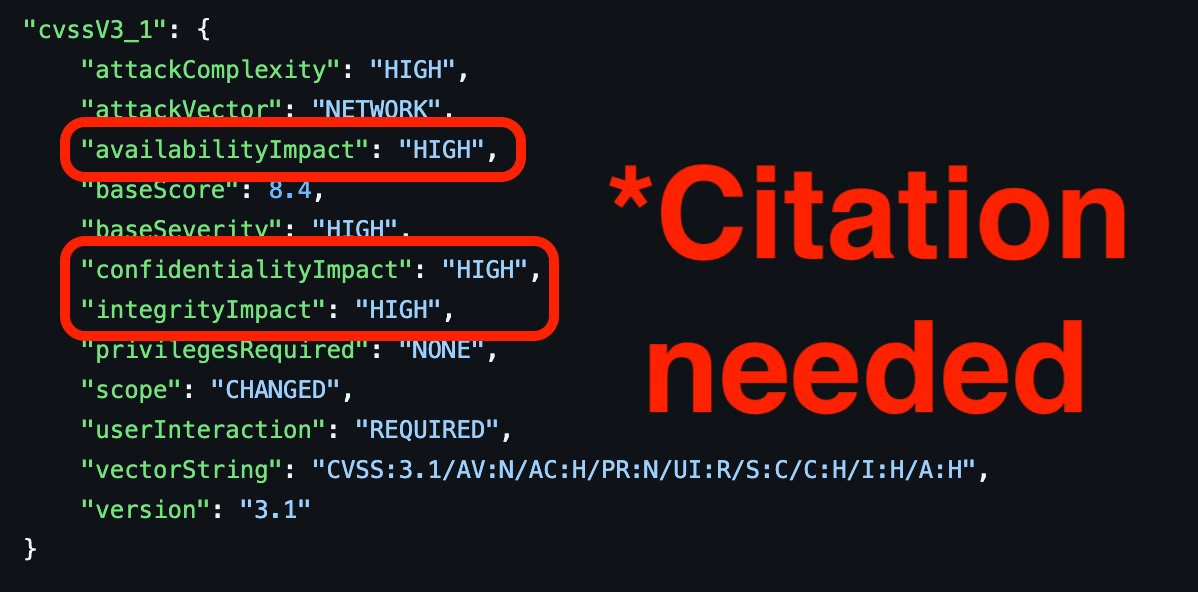
    Even the Confidentiality, Availability, and Integrity ratings of "HIGH" by GitHub are highly suspect. Can I modify cupsd.conf with this vulnerability? No, it's owned by root.

    Was this handled by somebody at the CNA who was unfamiliar with both CVE and CVSS?
    Do better.

    "scope": "CHANGED",
    "availabilityImpact": "HIGH",
"confidentialityImpact": "HIGH",
"integrityImpact": "HIGH",
    💬 3🔄 3⭐ 0
  • Sep 27, 2024, 5:21 PM

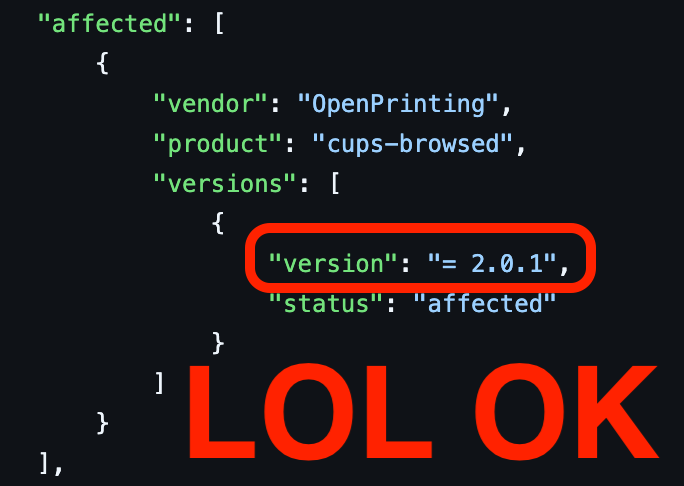
    Even the affected CUPS versions are wrong in the CVE entries. It currently says that ONLY version 2.0.1 is affected, and therefore all other versions of CUPS are NOT affected.

    Do we win a prize if every single field in a CVE entry is wrong?

    Image attached toot
    💬 0🔄 5⭐ 1
  • Sep 26, 2024, 8:12 PM

    @wdormann sometimes I wonder if inflated CVE severity isn't doing the same thing as social media disinformation, desensitisation and fuzz

    💬 2🔄 0⭐ 0
  • Sep 27, 2024, 5:58 AM
    yup. If you're wondering, it's probably happening.


    ...something something, boy that cried wolf...

    😕
    💬 0🔄 0⭐ 0
  • Sep 27, 2024, 7:21 PM
    @Bredroll @wdormann it very much is, and I hope this dude gets put on the DO NOT HIRE list by security companies for being such a prick and stoking worldwide panic. I don't think this guy has any idea how many millions of dollars were probably spent looking into this only for it to be nothing
    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 2🔄 0⭐ 0
  • Sep 27, 2024, 7:33 PM

    @feld @Bredroll
    He allegedly got the 9.9 from somebody at Red Hat.
    However, despite being the one who was intimately familiar with the vulnerabilities, he didn't bother to check the scoring himself. (It's not terribly tricky)
    nvd.nist.gov/vuln-metrics/cvss

    Instead, he chose to amplify the wrong information and kick start the rumor mill process. Because more fame is better than less fame, apparently. 🤦‍♂️

    💬 1🔄 0⭐ 0
  • 💬 2🔄 0⭐ 0
  • Sep 27, 2024, 7:39 PM

    @feld @wdormann I'd not really want to work for those. I'm not sure not getting a job would motivate me like that. Who knows..

    💬 0🔄 0⭐ 0
  • Sep 27, 2024, 7:43 PM

    @feld @Bredroll
    Gee, I wonder if publicly treating people like garbage and behaving like a psychopath might have a negative effect on one's employability? 😂

    💬 0🔄 0⭐ 0
  • Sep 27, 2024, 7:36 PM

    @feld @wdormann I think a lot of this needs to be laid at the door of printing in general, its ubiquitous but boring, so cups is the only game in town and nobody is motivated enough really to do it cleanly from scratch. The hype is one thing, but the bugs are pretty awful. They've got a 1990s "nobody will bother to attack this" feel about them.

    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • Sep 27, 2024, 7:55 PM

    @wdormann @feld only in recent years have I truly come to understand how much psychology is involved in computer software architecture and security, I used to relish the idea that it was you vs the problem and the code. But really, you can basically fail instantly or just be ignored because you lack the skills of persuasion or confidence in communicating. Sometimes it feels like wading through molasses

    💬 0🔄 1⭐ 0
  • Sep 26, 2024, 8:13 PM

    @wdormann Somehow my gut instinct was correct on this one. I guessed it would be a dramatic overplay of whatever had been found. Tomorrow morning at work will be endless fighting the bullshit this type of nonsense creates as the execs see the 9.9…

    💬 1🔄 0⭐ 0
  • Sep 26, 2024, 8:17 PM

    @pmelon
    I would hope that the execs are taking CVSS scores from a reputable source as opposed to a JPEG in a Tweet. 😬

    💬 1🔄 0⭐ 0
  • Sep 26, 2024, 8:21 PM

    @wdormann Ha ha. I do hope so. The Register and Bleeping Computer are amongst their favourites. It’s not helped that people within the org have been hyping it due to the Twitter dribbles.

    💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 2🔄 0⭐ 0
  • Sep 26, 2024, 8:19 PM

    @ecn
    Indeed. When I first saw the post, I noticed that I had his account blocked on Twitter.

    I can't recall when/why I did the blocking, but I see that they're unsurprisingly still a horrible person.

    💬 0🔄 0⭐ 0
  • Sep 26, 2024, 9:05 PM

    @ecn @wdormann I thought strange, why do I seem familiar with his username? Turns out he maintains openSnitch. A GUI App firewall for linux.

    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 26, 2024, 8:27 PM

    @wdormann

    A user on the victim system must print something to a printer that mysteriously appears on the system that has never been there before.

    i'm kinda wondering about this part - it makes sense from the vuln description, but on evilsocket's demo it happened automatically, did he actually omit the part where the exploit requires active input from the user? lol

    💬 1🔄 0⭐ 0
  • Sep 26, 2024, 8:30 PM

    @ptrc
    Somebody wanting to make something seem more important than it is will hand-wave over the part that they don't like.

    💬 0🔄 0⭐ 0
  • Sep 26, 2024, 8:49 PM

    @ptrc @wdormann

    On this evil guy’s write up he mentions print job being sent twice before he shows the video.

    “Wait for a print job to be sent to our fake printer for the PPD directives, and therefore the command, to be executed.”

    ‘Inject the *cupsFilter2 : "application/pdf application/vnd.cups-postscript 0 foomatic-rip line directive to instruct CUPS to execute /usr/lib/cups/filter/foomatic-rip when a print job is sent.’

    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 26, 2024, 9:04 PM

    @wdormann thus far my favorite conversation about this was someone who asked if I'd seen all the articles about the crazy Linux RCE and i told them about the CUPS vuln and they went "okay well let me know if we hear about the one from the article it sounds bad"

    💬 1🔄 2⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 27, 2024, 5:03 AM

    @wdormann Some researchers believe that over exaggerating their findings impact earns them a good reputation in the industry, because THEY FOUND SOMETHING CRITICAL!!!! 🙄 Yeah.

    💬 0🔄 0⭐ 0
  • Sep 27, 2024, 7:19 AM

    @wdormann do many Linux installs default to a firewall yet? I can say I've seen one, and in fact have hardly used a firewall on Linux.
    Still seems a low scoring cve

    💬 0🔄 0⭐ 0
  • 💬 1🔄 1⭐ 0
  • 💬 0🔄 1⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 27, 2024, 12:13 PM

    @privateger
    Combine a toxic researcher with a fantastic CVSS 9.9, and I suspect that this leaking ahead of schedule was perhaps the best way to put out the fire.

    💬 1🔄 1⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 27, 2024, 12:23 PM

    @privateger
    Eh it indeed a network-reachable vul.
    1) Attacker on your LAN connects to 631/udp to create a malicious printer, assuming there's no firewall present to block it.
    2) User on victim system selects this new mystery printer and prints to it. (Suuuuuure...)

    Red Hat allegedly telling the toxic reporter that one of the vuls has a CVSS 9.9 will surely result in this employee getting a talking to. 😂

    💬 0🔄 1⭐ 0
  • Sep 27, 2024, 2:12 PM

    @wdormann I wrote the CVSS v3 specification and I agree, that’s not how these metrics should be applied

    (Edited bc while a funny riff on the message at the end of US political campaign ads, I shouldn’t speak to the entirety of Will’s post bc reasons)

    💬 0🔄 1⭐ 0
  • 💬 0🔄 1⭐ 0
  • 💬 0🔄 1⭐ 0