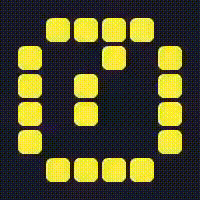
Login
You're viewing the functional.cafe public feed.
  • Nov 9, 2026, 9:41 PM
    Base64 is somewhat limiting for ASCII art, but I present a quantum proof™ RSA certificate:
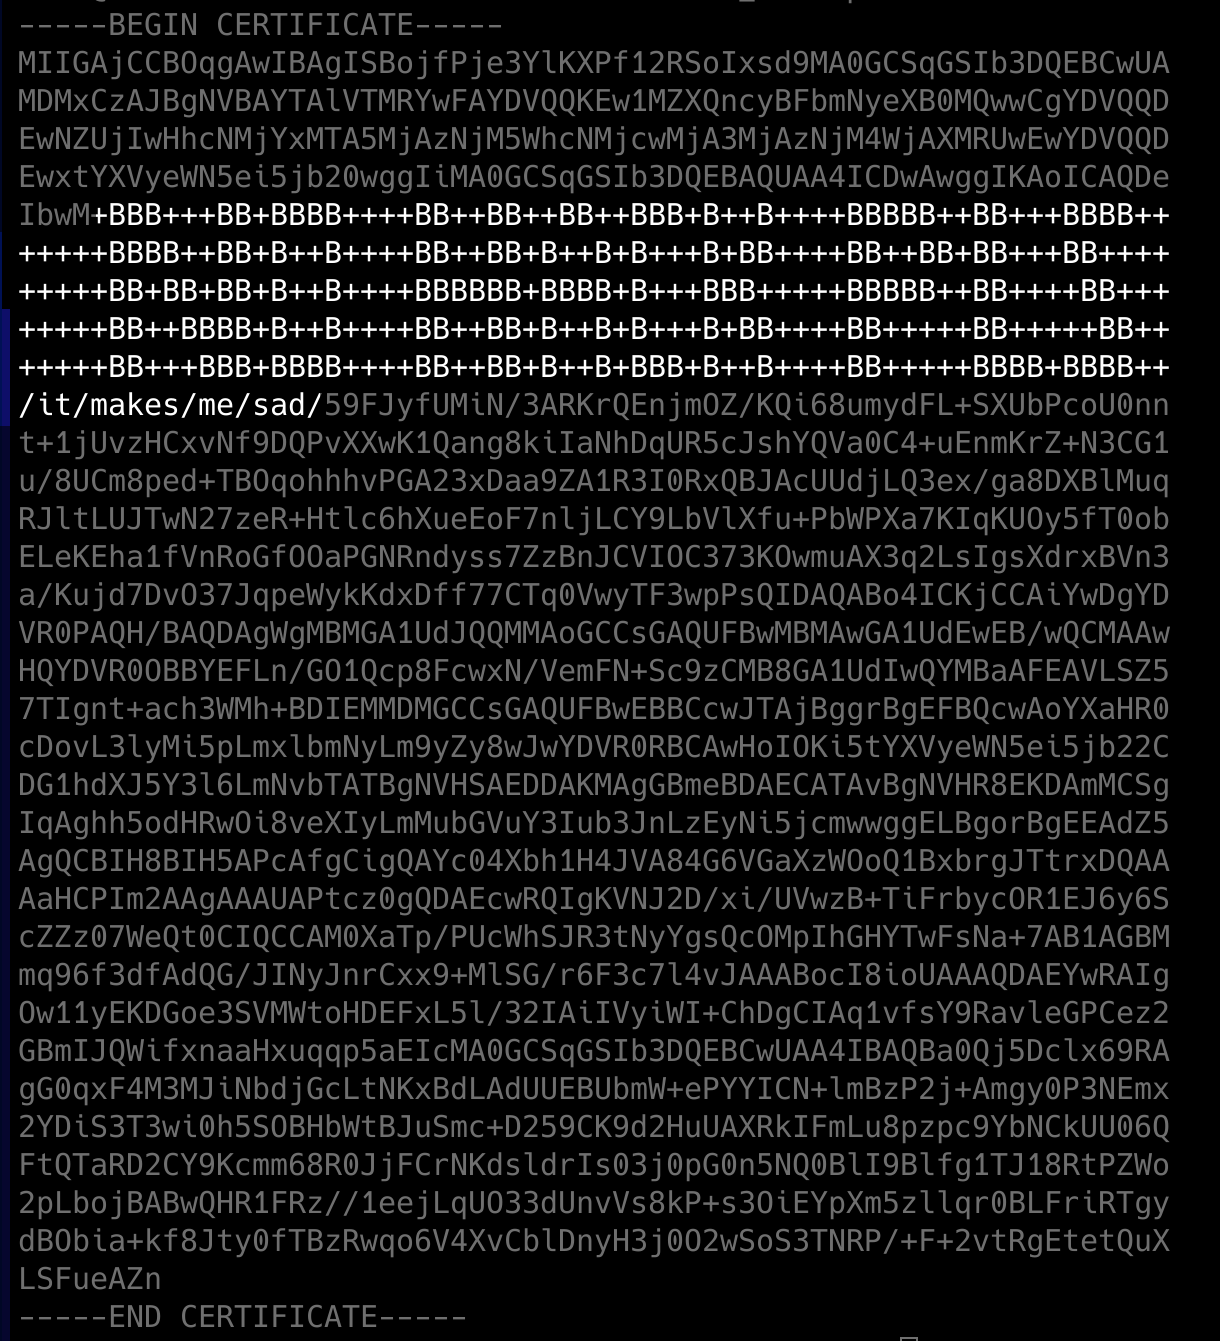
    A long (4000-bit) RSA certificate where the public key was crafted such that it's base64 encoding draws "NO HACK PLS" in ascii art.
    💬 9🔄 41⭐ 0

Replies

  • Nov 9, 2026, 9:51 PM
    Best viewed with
    openssl s_client -connect funnies.maurycyz.com:443 2>/dev/null < /dev/null | sed -n /BEGIN/,/END/p | grep --color=yes -z "[B]"
    💬 0🔄 3⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Nov 10, 2026, 7:21 AM
    @sodiboo@gaysex.cloud The key asks nicely for people to not hack it. The hope is that anyone with a quantum computer will feel bad and go factor someone else's key.

    /s

    My server does support post-quantum key exchange (X25519MLKEM768) so it's safe against quantum store-now-decrypt-later attacks. This is not a concern for signature schemes, so there's no real need to upgrade certificates until after quantum computers become realistic threat.
    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Nov 10, 2026, 11:19 PM

    @nothacking @davidgerard @bigiain Sorry, not sorry. I had to. Here's a handy private key to go with it (this is a valid key, hence the messy bits where the ASN.1 structure requires things like the header for each sequence specifying the modulus, exponent, etc)

    Alt text contains the key as ASCII as well
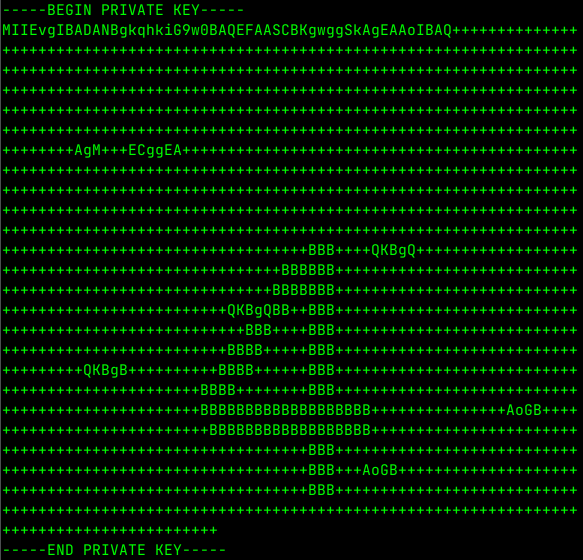
    a valid RSA private key where the base64-encoded content has an ASCII representation of a large digit 4.

The actual private key is as follows (warning for screen readers: you are about to sit through a LOT of ++++++):

-----BEGIN PRIVATE KEY-----
MIIEvgIBADANBgkqhkiG9w0BAQEFAASCBKgwggSkAgEAAoIBAQ++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++AgM+++ECggEA++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++BBB++++QKBgQ++++++++++++++++++
+++++++++++++++++++++++++++++++BBBBBB+++++++++++++++++++++++++++
++++++++++++++++++++++++++++++BBBBBBB+++++++++++++++++++++++++++
+++++++++++++++++++++++++QKBgQBB++BBB+++++++++++++++++++++++++++
+++++++++++++++++++++++++++BBB++++BBB+++++++++++++++++++++++++++
+++++++++++++++++++++++++BBBB+++++BBB+++++++++++++++++++++++++++
+++++++++QKBgB++++++++++BBBB++++++BBB+++++++++++++++++++++++++++
++++++++++++++++++++++BBBB++++++++BBB+++++++++++++++++++++++++++
++++++++++++++++++++++BBBBBBBBBBBBBBBBBBB+++++++++++++++AoGB++++
+++++++++++++++++++++++BBBBBBBBBBBBBBBBBB+++++++++++++++++++++++
++++++++++++++++++++++++++++++++++BBB+++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++BBB+++AoGB++++++++++++++++++++
++++++++++++++++++++++++++++++++++BBB+++++++++++++++++++++++++++
++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++
++++++++++++++++++++++++
-----END PRIVATE KEY-----
    💬 0🔄 96⭐ 227
  • 💬 1🔄 0⭐ 0
  • Nov 11, 2026, 4:53 AM
    @jupiter@mastodon.gamedev.place It is. See:
    openssl s_client -connect funnies.maurycyz.com:443
    (it's not actually terribly difficult. Crafting the vanity keys is mostly just a matter of division, and to get a signed cert, I used the fact that the certificate layout is consistent provided I use a similar CSR. This makes it possible experimentally determine the proper (mod 3 bytes) alignment for the base64 to come out right. Then, create a vanity certificate with a simple pattern (i.e. "AAAABBBBCCCC...") and use that determine the proper alignment so the ASCII art looks good in final cert.)
    💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • 💬 0🔄 1⭐ 0