Login
You're viewing the techdon.dev public feed.
  • Nov 14, 2026, 3:19 PM

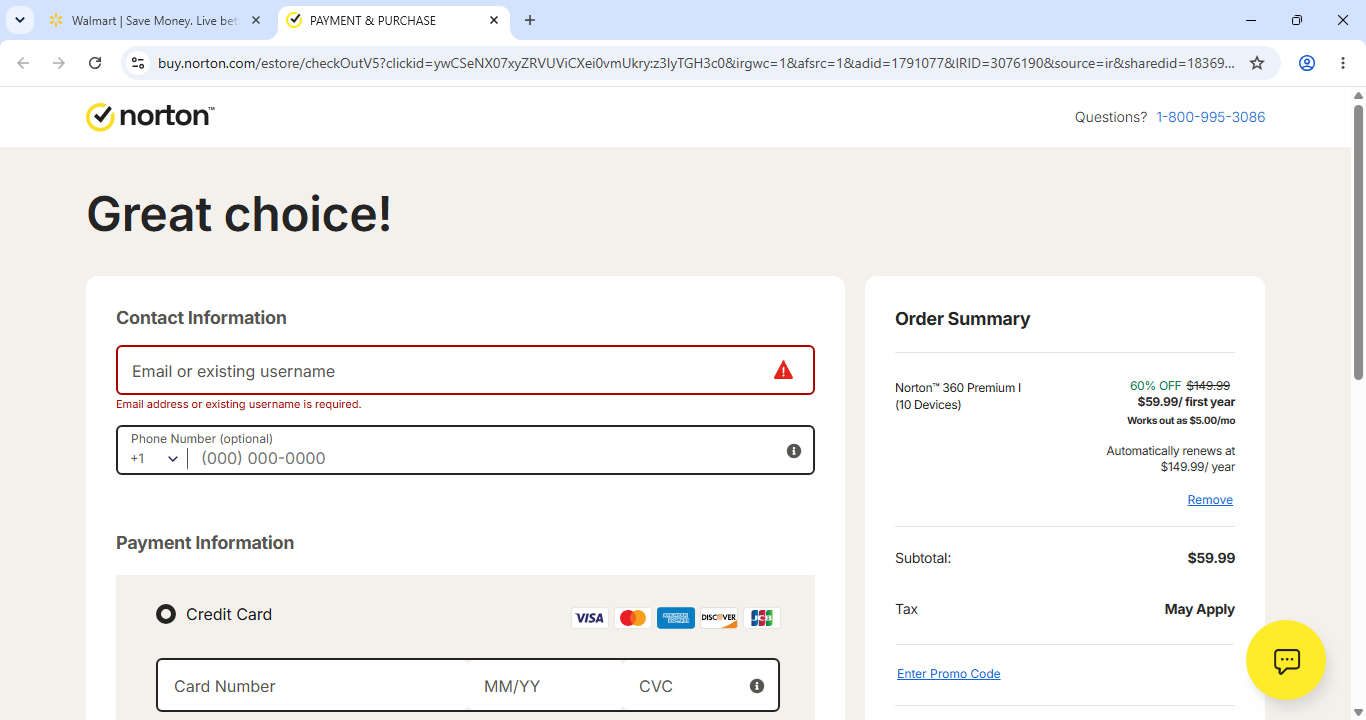
    After several scary steps, the final outcome is:

    Open real Walmart page tab
    Open real Norton purchase page, with affiliate identifier in the URL.

    Seriously?! All of this and no malware at the end? Just the hope to get an affiliate payment if the victim purchases the actual Norton Antivirus product?

    I feel like somebody wasn't paying close attention in the "Scam people on the internet" class. 🤦‍♂️

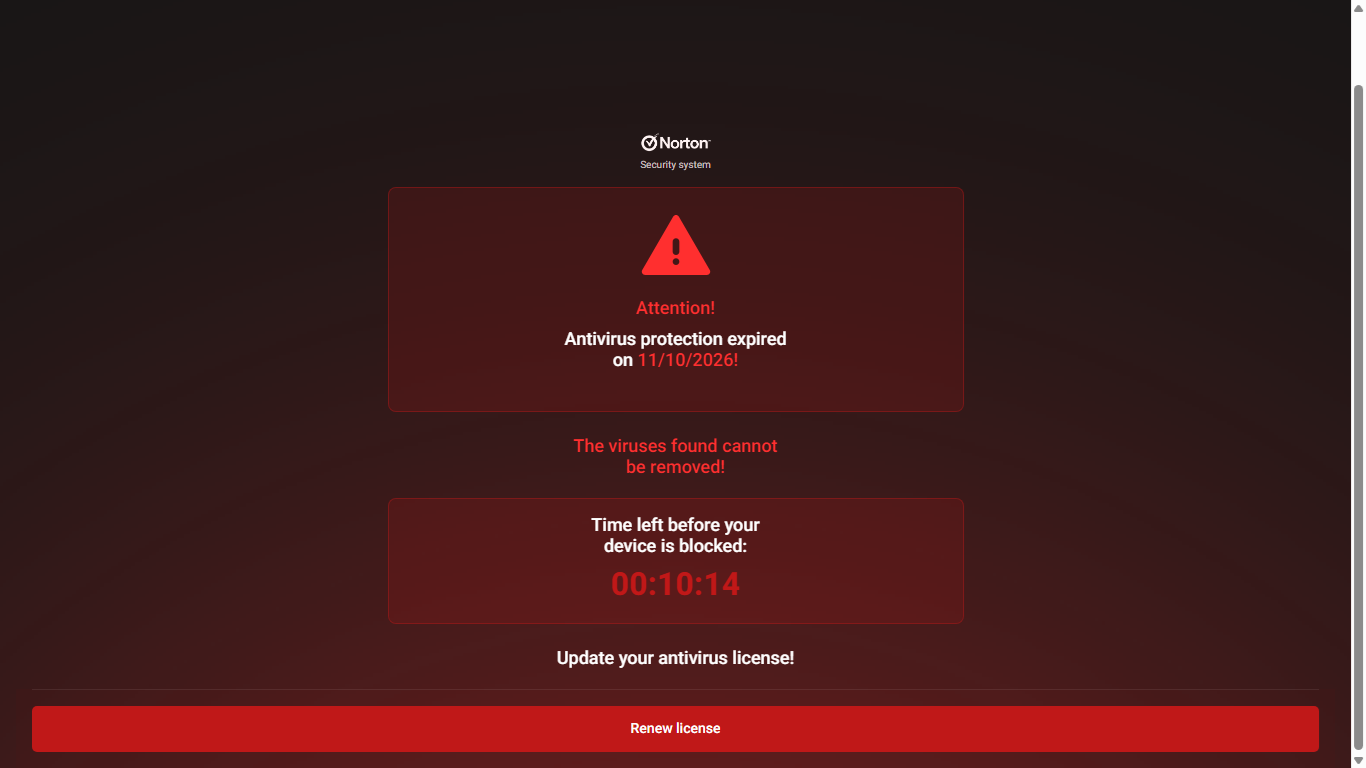
    Attention!
Antivirus protection expired on 11/10/2026!

The viruses found cannot be removed!

The time left before your device is blocked: 00:10:14

Update your antivirus license!

[Renew license]
    Web browser has two tabs open:
- Real Walmart page
- Real Norton Antivirus page on order page
    💬 1🔄 0⭐ 0

Replies

  • Nov 14, 2026, 3:44 PM

    @wdormann I don't know as much as I'd like about the scammer ecosystem; but it wouldn't be entirely surprising if that was intended.

    Affiliate payments are fairly 'clean' as money goes; and behavior that sure smells like fraud is widely tolerated(yes, looking at you "Paypal Honey" browser extension); so while the earnings are presumably tepid compared to the 'download a RAT and get scammed by "tech support"' model; it's the sort of thing that might even be legal, little civil case at most.

    💬 1🔄 0⭐ 0
  • Nov 14, 2026, 4:06 PM

    @fuzzyfuzzyfungus
    True. I suppose with that with this model, the advertiser could possibly keep the ad up on non-compromised, non-malicious ad networks. That is, it's the cutting edge with what one could get away with. 😂

    💬 1🔄 0⭐ 0
  • Nov 14, 2026, 4:32 PM

    @wdormann @fuzzyfuzzyfungus malvertising sites and traffic redirection systems profile victims heavily and may even send them to completely benign destinations if the IP or environment fingerprints suggest analysis or unwanted locale. Try the same without VM 🌶️

    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0