JayFjay
3/11/2026RE: https://cosocial.ca/@mhoye/116210288884252762
All the scrip you can eat!
RE: https://cosocial.ca/@mhoye/116210288884252762
All the scrip you can eat!
Every gun that is made, every warship launched, every rocket fired signifies, in the final sense, a theft from those who hunger and are not fed, those who are cold and are not clothed.
Medical provider phone calls are phish-suspicious as hell.
How many people have experienced this: "I'm calling from $doctor, I need to speak to Jay" "This is he" "What's your last name and date of birth?"
I usually require an innoculous piece of validating info that only they would know, like my PCP's name or a recent addition to my file before I give away PII... but someone in security there needs fix their process and stop training people to give up their birthdate.
In 2025, the home delivery program at https://efoodnet.org -- which I've been working with for years -- delivered 395,200 pounds of food to families and shut-ins across the county. This is just a small piece of the good they do.
If you've got a buck or two to spare and toss it their way, I'd be immensely grateful.
Being an example of kindness, care, and compassion for your neighbors is a primo form of resistance, and shows contrast with the heartless folks spreading hate and violence.
Behind the scenes at the GR-OSS OUT podcast. Just got finished taping a chat with Kevin Hannon about some of the cool back end enhancements he's been working on in kubernetes.
It won't be out for a month or more, but in the meantime you should have a listen to my chat with Aeva Black: https://podcast.gr-oss.io/18-security-and-resilience
It's extremely weird to read media written about you on the internet from 16 years ago you never knew existed.
https://www.usenix.org/blog/real-world-insights-how-secure-and-route-your-linux-network
I enjoyed giving this training, and really should revive it with a modern twist.
A personal OSS rule of thumb: The amount you criticize another project or contributor should be tempered by the amount of willingness *you personally* have to replace the impact of that project or person in the ecosystem.
It's much, much harder to build something than to tear it down.
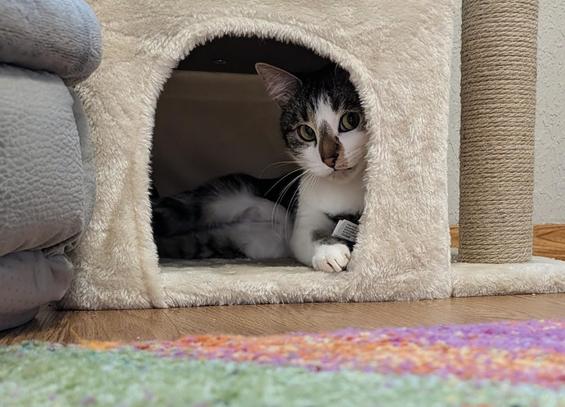
Our new cat (for a few weeks now), Juno!
Myself and some GR-OSS colleagues will be guests at the Major League Hacking panel tomorrow around noon -- come check it out! https://events.mlh.io/events/13144
The definition of simple, especially when talking about software or tech, is personal.
September's GROSS-OUT podcast has landed!
Priyanka Ravi and I talk about the history of DevOps (it didn't start with Kubernetes), how automated infrastructure has enabled "vibe coding" and taking open source concepts and applying them to internal corporate repositories.
Come listen to the latest episode here:
- https://www.youtube.com/watch?v=T86st3YsZ6o
- https://podcast.gr-oss.io/14-inner-source-devops
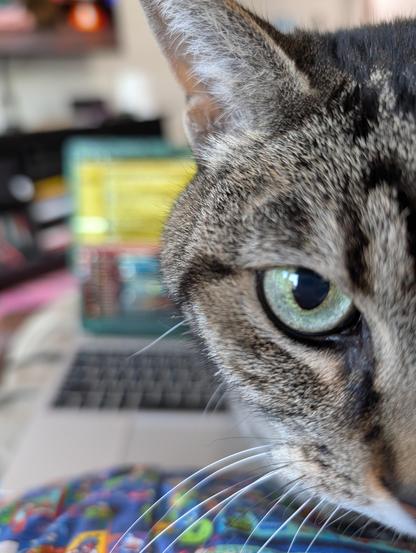
Laptop kitty
Eventlet migration is about more than just migrating code -- it's about keeping the lights on and coordinating people. https://www.youtube.com/watch?v=RIc-Tut95YM
Always nice to see more folks getting into using video to communicate about the OpenStack project. Thanks to Herve for the update!
re: https://www.newsobserver.com/sports/spt-columns-blogs/luke-decock/article311662058.html
I started out my career working at a small newspaper, the Spring Hope Enterprise, as a Sports Editor.
The memory of being able to see the Carolina Mudcats play via a press pass is still strong. Many nights, I went just so I could eat the press meal because I didn't have food or money until payday.
Now that AA baseball franchise is closing down, and the stadium with it, I find myself feeling quite melancholy :(.
Goodnight, Muddy.
https://9to5google.com/2025/08/25/android-apps-developer-verification/
Well, what platform is it time to change to now? Anonymous computing, and publishing software anonymously, is a feature -- not a bug. I don't need Google to big brother me when I already have to go through an arcane ritual to enable sideloading.
The internet is becoming less and less open.
The culprit this time? Akamai-based reputation/security software is consistently blocking use of Firefox and Chrome on linux, and blocking Firefox on Android. This is via different IPs, too, so it's not a reputation thing.
I have, in the past, had similar problems with Cloudflare, but they are less pervasive than with Akamai.
GOOGLE CHROME-BASED BROWSERS ARE NOT THE ONLY WAY TO ACCESS THE INTERNET, DAMMIT.
Wanna run Ironic without eventlet? Checkout the master branch :D
Important to remember that hype curves can be outta whack even on good technology.
I sat beside *multiple* Rackers a decade ago who ran the "cloud-to-butt" extension because they were tired of the cloud hype. Ten years later, I write this toot in a house paid for (mostly) by my work on/in the cloud.
Keep this in mind as people try to polarize the AI/LLM debate. Once the hype cools down, the tools will be there for those who know how to use them correctly.
I have a HUSBZB-1 dual z-wave/zigbee USB controller that needs a good home. I replaced it with one that supported S2 security; then successfully did the hardmod+firmware update on the HUSBZB-1 to get it to support S2 as well (I wasn't brave enough to do this until I had migrated).
If you want it, I'm happy to send it somewhere in the US. I don't want it to go to waste and cloud-free smart home is cool. It can be the first piece for your home assistant :).
My first introduction to @dgl was finding https://dgl.cx/2023/09/ansi-terminal-security on my own and then being surprised he was a co-worker!
I got to sit down with him and chat about the recent git CVE he discovered and a lot more in our recent podcast episode.
If you don't have time for that, here's 5 minutes on the vulnerabililty specifically, cut from that interview: https://youtu.be/XZHxE3iWPMU