DutchDudejeroensky@mastodon.social
Oct 4, 2026, 12:49 PM@Tutanota @GrapheneOS
Does this also has impact on #Murena /e/OS ? (that is Android without google)
@Tutanota @GrapheneOS
Does this also has impact on #Murena /e/OS ? (that is Android without google)
@jeroensky @Tutanota @GrapheneOS Android is a Google product - there is no "Android without Google".
@pino @Tutanota @GrapheneOS
But their is a Android without phone home activity to google: /e/OS.

@jeroensky @pino @Tutanota That's completely untrue. /e/ adds a bunch of Google services to the OS with privileged access compared to the Android Open Source Project (AOSP). It also adds other privacy invasive services including their own.
Their supposed tracking protection is a small list of filtered domains for DNS lookups. It can't block the vast majority of the privacy invasive behavior by apps and services due to dual purpose domains. Apps can also trivially evade DNS filtering regardless.
@GrapheneOS @jeroensky @Tutanota
@GrapheneOS @jeroensky @Tutanota
Yeah, sorry for these inaccuracies. I am an /e/OS user (before that, I was a cyanogenmod user (before that was only the HTC Dream)).
These are some nice additions.
But the OS itself is still completely a Google product, right? Once AOSP disappears, there's no way these custom ROMs could still make sense, right?
@pino @jeroensky @Tutanota /e/ drastically reduces privacy and security compared to the Android Open Source Project. It isn't at all a safe option, especially on end-of-life devices lacking kernel, driver, HAL and firmware updates, but it's far behind everywhere.
/e/ lags years behind on updates to new major releases with the full set of privacy and security patches. A large portion of privacy and security patches are not backported. New privacy/security protections aren't backported at all.
@pino @jeroensky @Tutanota Android Open Source Project (AOSP) is an open source OS and alternative operating systems based on it are forks of it similarly to each Android fork made by an OEM for their devices. The terminology custom ROM is inaccurate on a technical level and propagates many misconceptions about these. These are not modifications of the stock OS on devices but rather a fork of AOSP which runs on the hardware too with firmware and typically also userspace driver code from the OEM.
@pino @jeroensky @Tutanota AOSP can be forked and developed further without Google, but currently Google are the ones doing most of the development. It would be a massive amount of work to take over developing the whole OS.
It would be far better for Android to be split away from Google into an independent company by regulators due to Google's anti-competitive and fraudulent behavior in many areas. They use their monopolies for coercive control over Android OEMs and go back on commitments.
@GrapheneOS @jeroensky @Tutanota
Ahh, sry, now I read it slowly enough... You are saying that /e/ is not even that good.
Well, yeah, might absolutely be true. Personally, I will not spend lots of efforts into migrating to another Google-based OS, though. I WOULD spend money and effort for a system that is ACTUALLY free and not depending on Google at all.
All these custom ROMs - the good ones and the worse ones - are just a cat and mouse game.
@pino @jeroensky @Tutanota AOSP is an actual open source OS and be developed without continued releases from Google. That would be an enormous amount of work and very difficult to do but it's entirely possible. It's certainly easier than starting over or trying to turn the desktop Linux software stack into a viable mobile OS with similar usability, compatibility and especially privacy/security. Desktop operating systems are extremely far behind on privacy and security, especially outside macOS.
@GrapheneOS @jeroensky @Tutanota
That will only work for some time, up to the point you've largely lost compatibility to actual recent Android versions.
But, yeah, fine for me. As soon as this fictitious OS is actually there, I'd take a look.
But I want to see that new mode of procedure actually working before I'd invest much effort. I don't believe in it at all.
@pino @jeroensky @Tutanota You're using an OS without standard privacy/security patches and protections. Even the standard Android patches and protections are far from adequate to keep users safe, especially with AI models accelerating exploit development.
Currently, your data is up for grabs by any app which wants to abuse known privacy and security vulnerabilities along with remote attacks. It isn't a theoretical problem. There are public exploits on GitHub which you don't have patched.
@GrapheneOS @jeroensky @Tutanota
Thank you for your hint. Yes, there's probably some risk. I'm not saying it's ideal. But, I think, the actual danger is manageable for me. I would absolutely take action, as soon as anything fundamentally better is available. And spend money. But any other AOSP fork isn't what I'm waiting for. It's still the "Google OS" (unless you manage to split it away from them). Even if you cleverly sell it as "operating system with Android app compatibility".
@GrapheneOS @pino @Tutanota
Why should mac OS be safer then Linux?
Read only OS does not mean it is safer then Linux (read/write), assuming they both uptodate. I think Open source (Linux distro) is more secure then proprietary (OSX, Windows), because with open source their are way more people who can check for and fix security issues.
@lispi314 @jeroensky @Tutanota @pino Linux is becoming higher quality due to the use of AI models rather than worse. It was already filled with low quality code riddled with bugs including vulnerabilities. The slop was written by the human kernel developers and now AI models are finding the massive number of holes in it. It's true they're merging low quality code from AI models but you have to bear in mind they've been merging low quality code from humans with minimal code review all along.
@lispi314 @jeroensky @Tutanota @pino Linux kernel is probably a dead end in terms of making a high security OS because they aren't at all fully on board with using Rust and converting it into a hybrid kernel with a lot of isolation instead of only being a monolithic kernel. They're still putting tons of stuff into kernel space simply due to project organization. If they had a way to ship closely tied userspace components without ABI compatibility for those it would help security quite a lot.
@GrapheneOS @lispi314 @jeroensky @Tutanota
Sure it's not perfect. But it sounds like we are awaiting some great Rust-based new OS, designed and implemented by AI, without all the legacy garbage from the last half century. And still powerful enough to be practically usable for various tasks.
I mean, yeah, nobody would be sad. At least if it would be FOSS (otherwise you again have to trust some dodgy US corp).
But when will that be available?
@GrapheneOS @lispi314 @Tutanota @pino
I choose Fairphone with /e/OS, because it was the only option on a fairphone with less google as possible.
I ask Proton Lumo about if their is a Smartphone with #GrapheneOS preinstalled (so warranty@ GrapheneOS) and no Pixel device. Lumo mention something interesting:
#Motorola announced a partnership with the GrapheneOS Foundation at MWC 2026 to ship phones with GrapheneOS starting in 2027. This will be the first major OEM to pre-install it officially.
@jeroensky @lispi314 @Tutanota @pino /e/ has extraordinarily bad security and awful privacy. One of the main things they do is build in a whole bunch of privileged Google services into AOSP along with a bunch of their own problematic services. It isn't anything close to the OS option for Fairphones with the least Google services.
Fairphones don't have decent secure features or updates regardless of OS choice. Those aren't reasonably secure devices. GrapheneOS won't be using insecure devices.
 Oct 4, 2026, 2:20 PM
@pino @jeroensky One might as well say there is no Linux desktop without Red Hat.
(News bulletin: RH has supplied most if not all of the new desktop subsystems because 1) they rejected the projects that actually innovated 2) the community wanted to choose what big business chose, which is RHEL.)
OTOH, Google has no more power to place constraints on Android forks than Red Hat has over other distros.
Okay, fine, then you are one of these guys I address here:
https://social.cologne/@pino/117382657335218296
What are we discussing here then? Everything is fine!
What you say is terribly oversimplified in various ways and you know that! ;)
Whatever RH does tomorrow - it will not stop Linux desktops to exist.
But AOSP will just stop to exist as soon as Google decides. It starts with hardware support (but doesn't stop there), right? It actually is already difficult to get particular apps running
Oct 4, 2026, 2:34 PM@pino @jeroensky Actually, RH could do a lot to stop other distros from existing and arguably have already done the same thing as Google in terms of cutting the community off from any modifications which are "only" distributed to paying RHEL customers.
I think the situation with Google is actually a lot more workable, for now. The lions' share of Google dependency is located in Play Services, which the Android-fork community has demonstrated they can replace or live without.
What can RH do to hurt my Debian desktop? What modifications do they only distribute to paying RHEL customers? As soon as people get aware of that happening, for relevant stuff, it e.g. will surely make the systemd discussion pop up again - and this time they'll lose.
I have a veeery hard time being optimistic about free Android for the future. If Google wants it to be non-free, it will eventually be. And they want. They just waited for that all the time.
PS: I'm not saying that I love RH. I liked them back then, but that's a long time ago.
And surely they contributed all kinds of modules that are fundamental to nowadays Linux desktops - for better or for worse.
And it will lead to some friction if RH tomorrow decides to be maximum malicious.
But it's ridiculous to compare that to Google and Android, isn't it?
Oct 4, 2026, 3:11 PM@pino It ridiculous to suggest that the billions of people in the Android ecosystem aren't worth fighting for, esp. because you're riding in on your white horse offering a mishmash of completely different UIs and package formats all called "Linux".
(but, I mean, why not - APIs for Android application development aren't Linux-specific).
...yeah, whoops! The UI and API are what's more important to users, and those have already been forked by the community.
Speaking of whoops, here's a chart for you (we've been here before...)
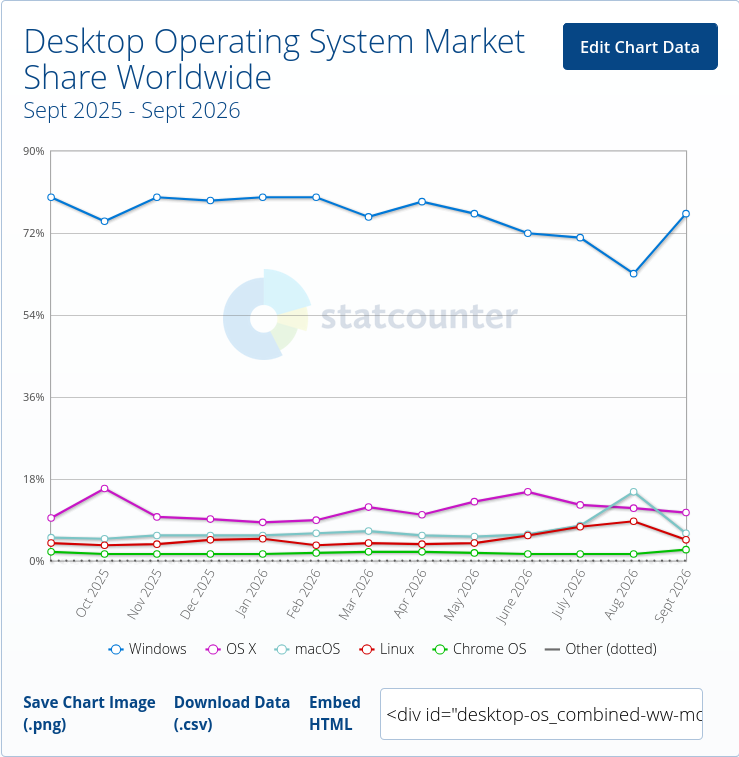 Oct 4, 2026, 3:16 PM
@pino Interestingly, Android 17 introduces a desktop UI.
If it were included in this chart it would probably surpass Windows in another 6-12 months.
@tasket Well, you started a discussion about Linux here. I don't even get the point that you are trying to make tbh. For me it's absolutely fine if you dislike Linux. I explicitly tell people to stay where they are, all the time. I don't need the masses being on Linux at all. But again, you came up with Linux!
(I don't see a #byelinux in your chart though. Even not if it wouldn't be a silly one year time range)
Oct 4, 2026, 2:59 PMAs soon as people get aware of that happening, for relevant stuff, it e.g. will surely make the systemd discussion pop up again - and this time they'll lose.
Dude, the calvary isn't showing up for 0.3 million moblin users. Red Hat's dominance has withered consumer interest, and the Linux community is fine with that.
OTOH, some large phone brands (Huawei and Xiaomi) have already demonstrated in their mainline products that the Android framework can run apps successfully on non-Linux kernels (kernels that are head-and-shoulders more secure than Linux will ever be).
@tasket They run Android on non-Linux kernels? That's interesting (but, I mean, why not - APIs for Android application development aren't Linux-specific).
But how is that related to the original discussion? Sry, I don't get it.
@jeroensky @Tutanota /e/ is highly unsafe due to lack of important standard privacy/security updates and features. Murena is also heavily pushing anti-privacy propaganda including repeatedly claiming highly private and secure devices are mainly beneficial to criminals and pedophiles. It's not a legitimate privacy OS on either a technical level or the fact they're siding with highly anti-privacy policies. Don't be fooled into using it. It isn't what it claims.
@jeroensky @Tutanota /e/ is a poorly maintained fork of LineageOS reducing privacy and security patches/protections far more than LineageOS compared to AOSP. It takes years to ship full patches despite misleading users. It also adds many privacy invasive services.
More information:
https://eylenburg.github.io/android_comparison.htm
Two examples of Murena pushing anti-privacy propaganda: