TIL: Brazil's flag says "Ordem e Progresso" in the middle, meaning "Order and Progress".
Would seem like a bad flag if Brazilians had elected the son of the jailed out-of-order and non-progressive guy.
TIL: Brazil's flag says "Ordem e Progresso" in the middle, meaning "Order and Progress".
Would seem like a bad flag if Brazilians had elected the son of the jailed out-of-order and non-progressive guy.
I can't believe I'm saying this, but it's done. It's finally done. After 14 YEARS Serbia is finally free.
Student-lead coalition won >50% of the votes in national elections.
It looks like the students beat authoritarian Vucic in the Serbian elections!!
https://www.theguardian.com/world/live/2026/oct/25/europe-serbia-elections-aleksander-vucic-student-list-protests-bulgaria-latest-news-updates
One of the challenges now is that anytime something bad happens in the tech world AI companies are incentivised to claim they did it. As their currency is publicity and relevance, not details.
It doesn’t help that it’s a zero-consequence environment. If somebody did a NotPetya and wiped 10k PCs, it wouldn’t surprise me if people discuss saying Claude did it - as there’s currently no downsides, it just makes you look powerful to C level execs.
If anybody reads this OpenAI post and thinks AI found a zero day - no. This one was patched months ago, not found by OpenAI, and reported by an old-school fuzzer.
Best feeling in the world!!
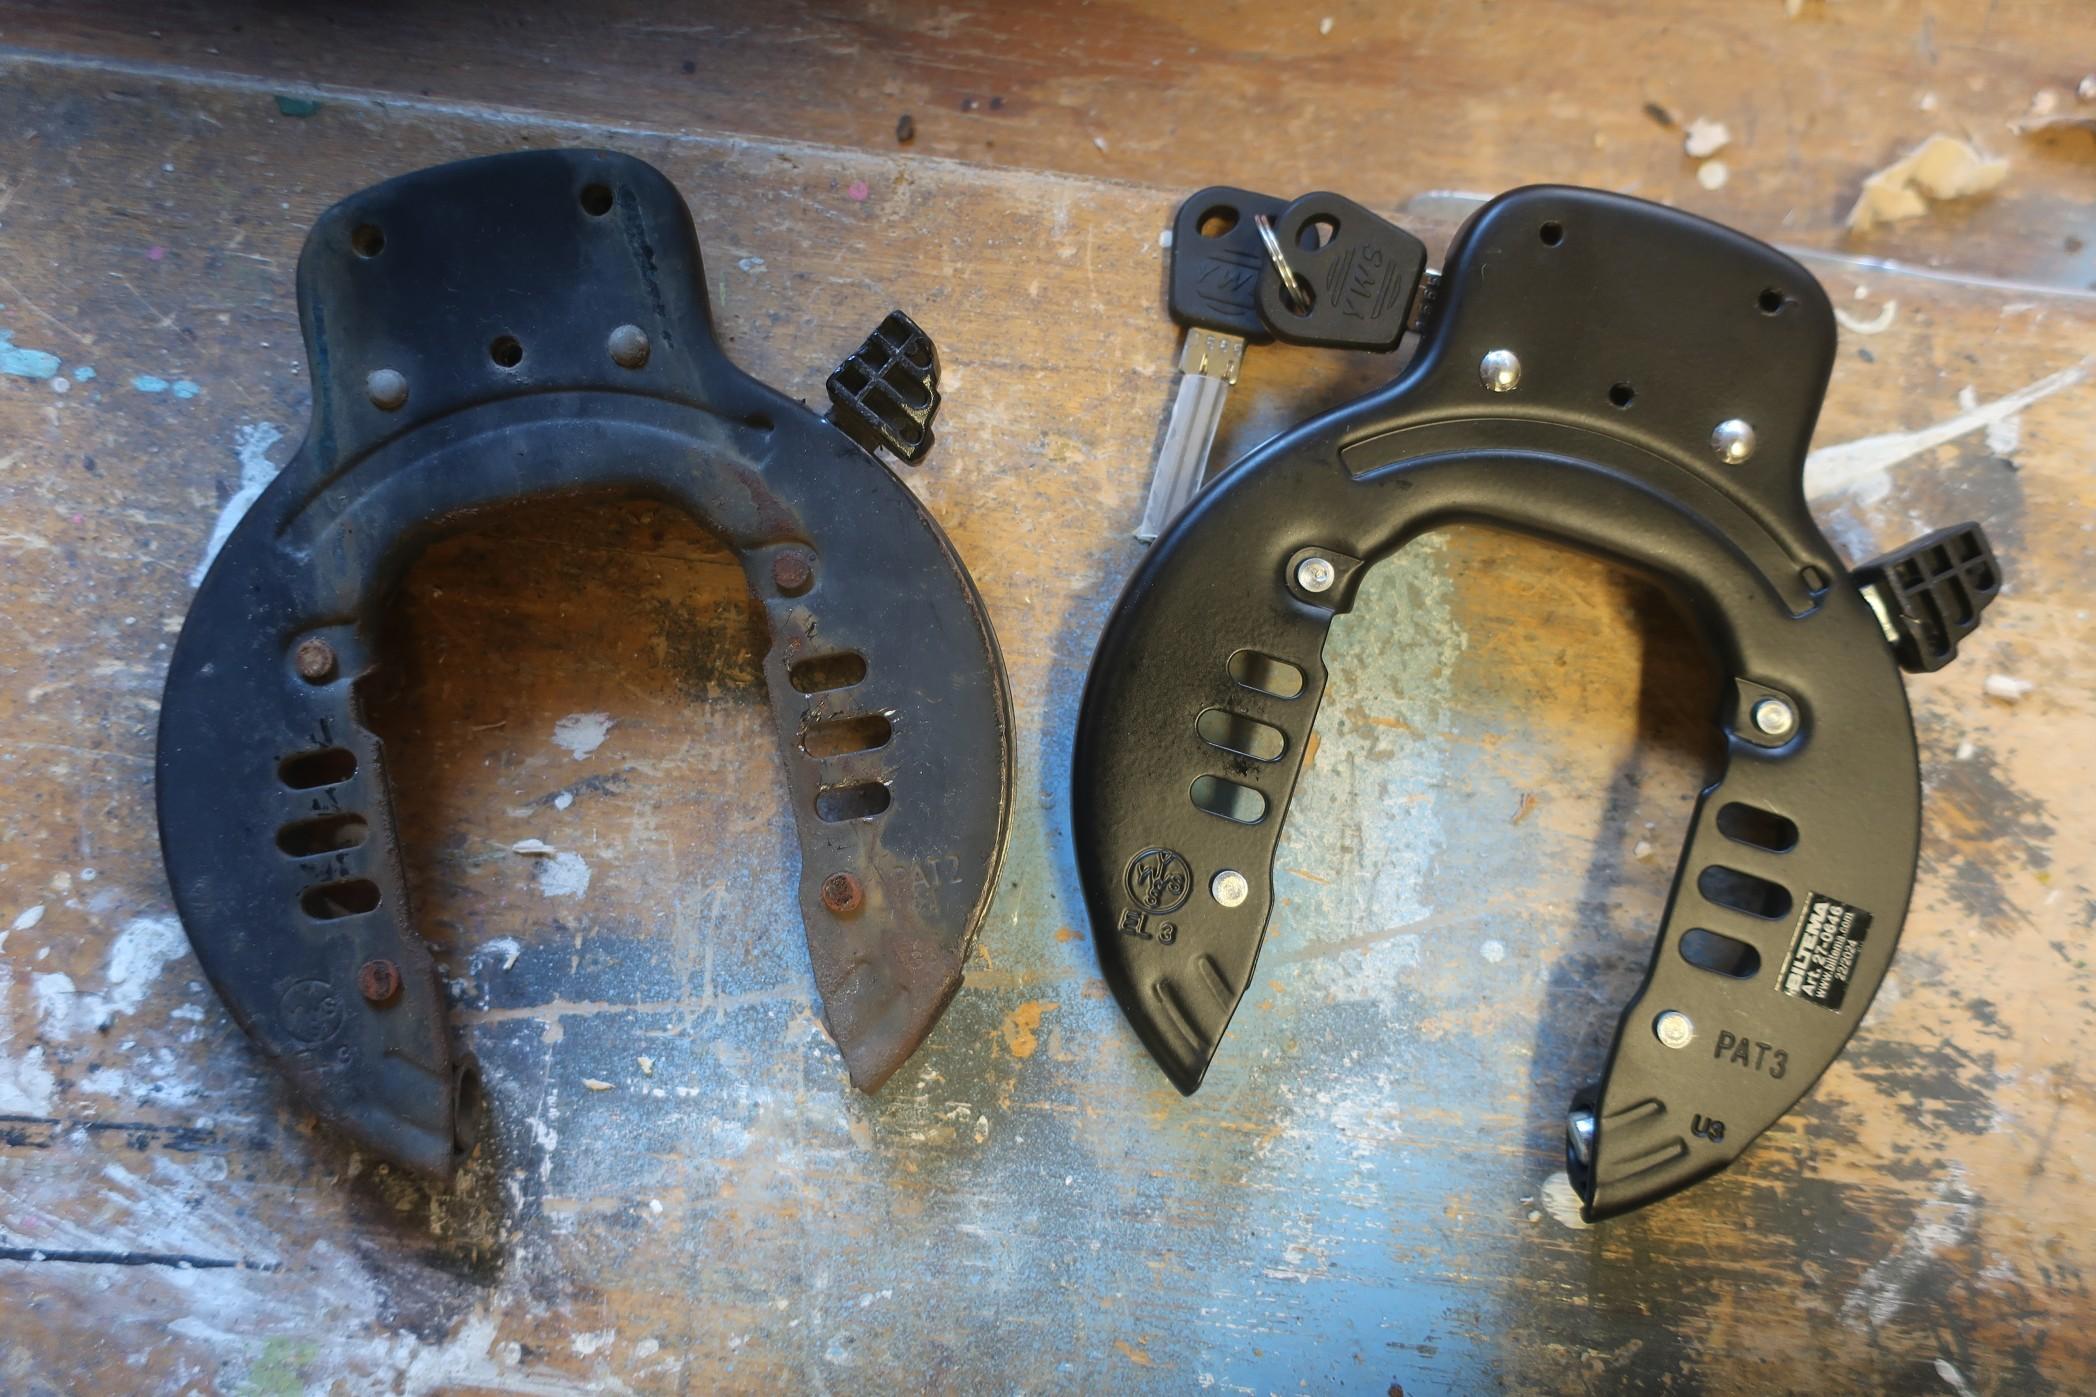
It's soooo incredibly satisfying to be able to buy exactly the same $15 bike lock ~13 years after having bought an identical model at a bike flea market.
Nothing changed, feels like exactly the same model with the same type of key. If it ain't broken, don't fix it. Thank you.
"There was the incident where illegal Israeli settlers in the West Bank — who are financed, armed, enabled, and otherwise supported in every possible way by the Israeli government — viciously attacked a Washington Post photojournalist, breaking her ribs and fracturing her vertebrae, and a day later attacked a group of European diplomats from Belgium, France, and Poland (countries that, unlike Israel, actually are US treaty allies).
The reaction was, well, muted. The Israeli government at first tried to cast doubt on the reports, accuse Palestinians of being the culprits, and even blame the diplomats. The US secretary of state said it was “not a good look.” The German government called it “troubling” and said it should “be criticized,” while the European Union called vaguely for “full accountability.” The Israeli government did arrest ten suspects and has now released nine of them from custody and into house arrest.
Given that merely bringing charges against a group of Israeli soldiers who gang-raped a Palestinian prisoner led to Israeli rioting, which then led to those charges being dropped and one of the rapists becoming a quasi-celebrity in the country, don’t hold your breath waiting for this accountability."
https://jacobin.com/2026/10/israel-gaza-iran-crimes-settlers
#Palestine #WestBank #IsraelTerroristState #Lebanon
LOL, Hassan Piker is on BBC now (Americast)
Also, in Finland
"STOP DATA CENTRES
ARKADIANKATU 6, HELSINKI
MON 26 OCTOBER 16:00-17:00
DEMONSTRATION
AGAINST GOOGLE
Organised by Luontoliitto's Policy Group"
«Earlier this year, we worked with Alpha-Omega to scan PHP with Anthropic's Claude Mythos. But since the Mythos scan, we have added other tools, including OpenAI's Daybreak Red for validating reports and exploits, alongside sanitizer builds and reproduction environments that match our CI on every platform PHP supports»
So the glorified parrots, with the "most frontier" models (cough cough), couldn't find jack shit of the issues with PHP.
🐍 🛢️ sales gimmicks.
RE: https://hachyderm.io/@e_nomem/117481033780060162
Nice little slipstream CVS announcement, well played GitLab 👏
While you were patching PHP, LiteLLM went and get compromised again.
https://ifin.network/t/litellm-compromised-again-credential-stealer-and-backdoor/919
that PHP fix is 13k lines
5k apparently of non-tests
that's all human written, right? I wouldn't want to speak out of turn about sprawling quick fix diffs
Digital Ocean just wrote this:
»Importantly, patches are only available for currently supported PHP versions (8.2 and later). If you are running an end-of-life PHP version (8.1 or earlier), no official patch will be available and you should plan an immediate upgrade to a supported version.«
+
»If you are on PHP 8.1 or earlier, upgrade to PHP 8.2+ so you can apply the patch. EOL versions will not receive patches.«
WTF no one is simply patching the old versions??? 🤦
PHP has been my main stack on and off for 20 years, sans a couple of gaps where I worked with other stacks. I've worked in operations, performed audits and implemented best practices and standards.
I don't think I would be working with computers if it hadn't been for PHP.
What is frustrating at this point where everyone who still holds a job in my corner of this industry is scrambling to update, audit, test and triage that absolutely nobody has reached out to me to ask for assistance.
Does anyone know how Al Jazeera is handling this PHP thing? (it's a Wordpress site)
Der er fundet en alvorlig sikkerhedsfejl[1] der påvirker Nextcloud, PrivateBin og webmail i Mailu (vores e-mailsystem). Derfor har vi midlertidigt lukket ned for disse services, indtil problemet er løst. Mail vil stadig blive leveret og modtaget – det kan bare ikke læses i webbrowseren.
LOL this PHP stuff and LLM shitshow... what a great business to be in... the gift that keeps on giving.