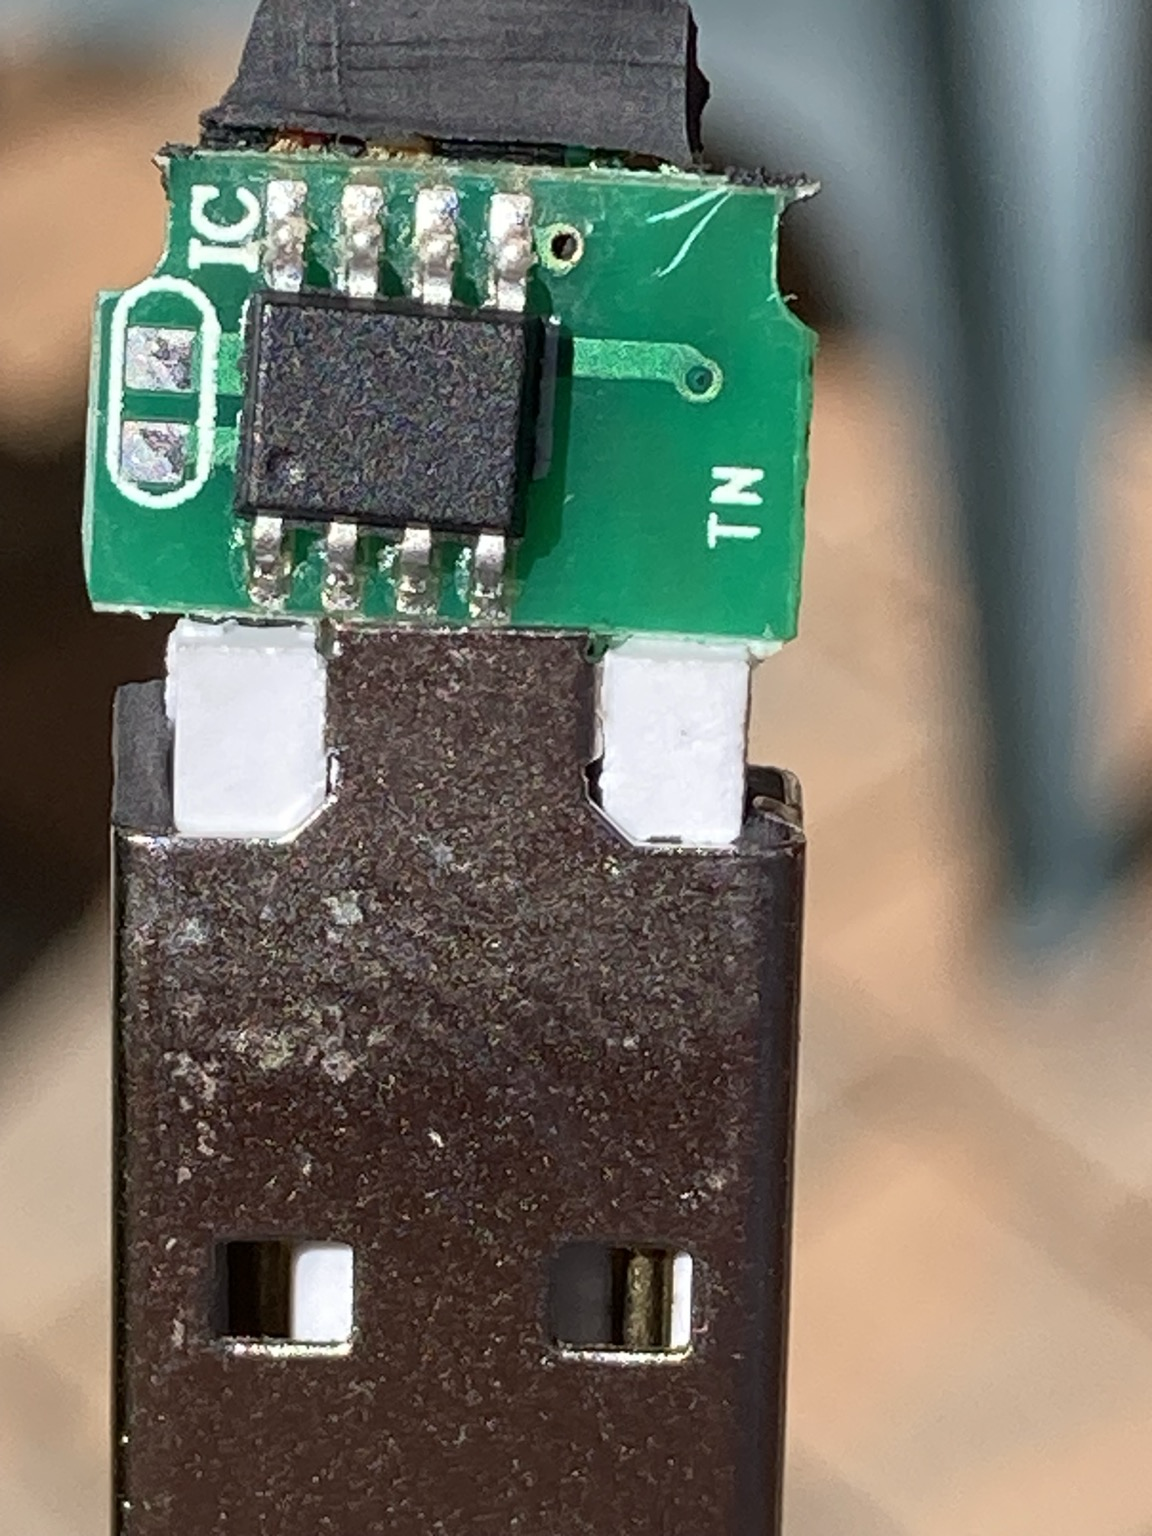
@lcars I've been trying for a long time to root my Wink Hub v2, most recently using the exploit that you developed for the USB Armory, updated with the correct entry point for the i.MX6UL, delivered over SDP/USB. Unfortunately, after much trying, I have reached a dead end: The device simply fails to do anything identifiable after the modified U-Boot is sent to the board.
Would you be prepared to assist in figuring out what I am doing wrong, given your deep understanding of both the exploit and the vulnerability?
I was able to read off the u-boot code from the original Wink 2 board by desoldering the NAND and reading it with a flash reader, and I have got to the point where I can send the u-boot binary back to the board using SDP, and have the EXEC action *NOT* fail with an invalid signature error. However, I have concluded it won't boot that way due to the CSF de-initializing the RAM that the CPU is trying to execute out of! To get this to work, I had to modify sdphost to NOT clear the CSF field prior to sending the binary, otherwise the signature would fail to validate.
This suggests to me that the u-boot image I am sending is intact, at least.
Do you have any suggestions for things I should try? Thanks for all your research and contributions!