People are cooking!
I really wonder how the reaction towards all of this will look like.
I embrace this 100%. Give this a year and a few motivated people and this stuff will be usable. That's at least my hot take.
People are cooking!
I really wonder how the reaction towards all of this will look like.
I embrace this 100%. Give this a year and a few motivated people and this stuff will be usable. That's at least my hot take.
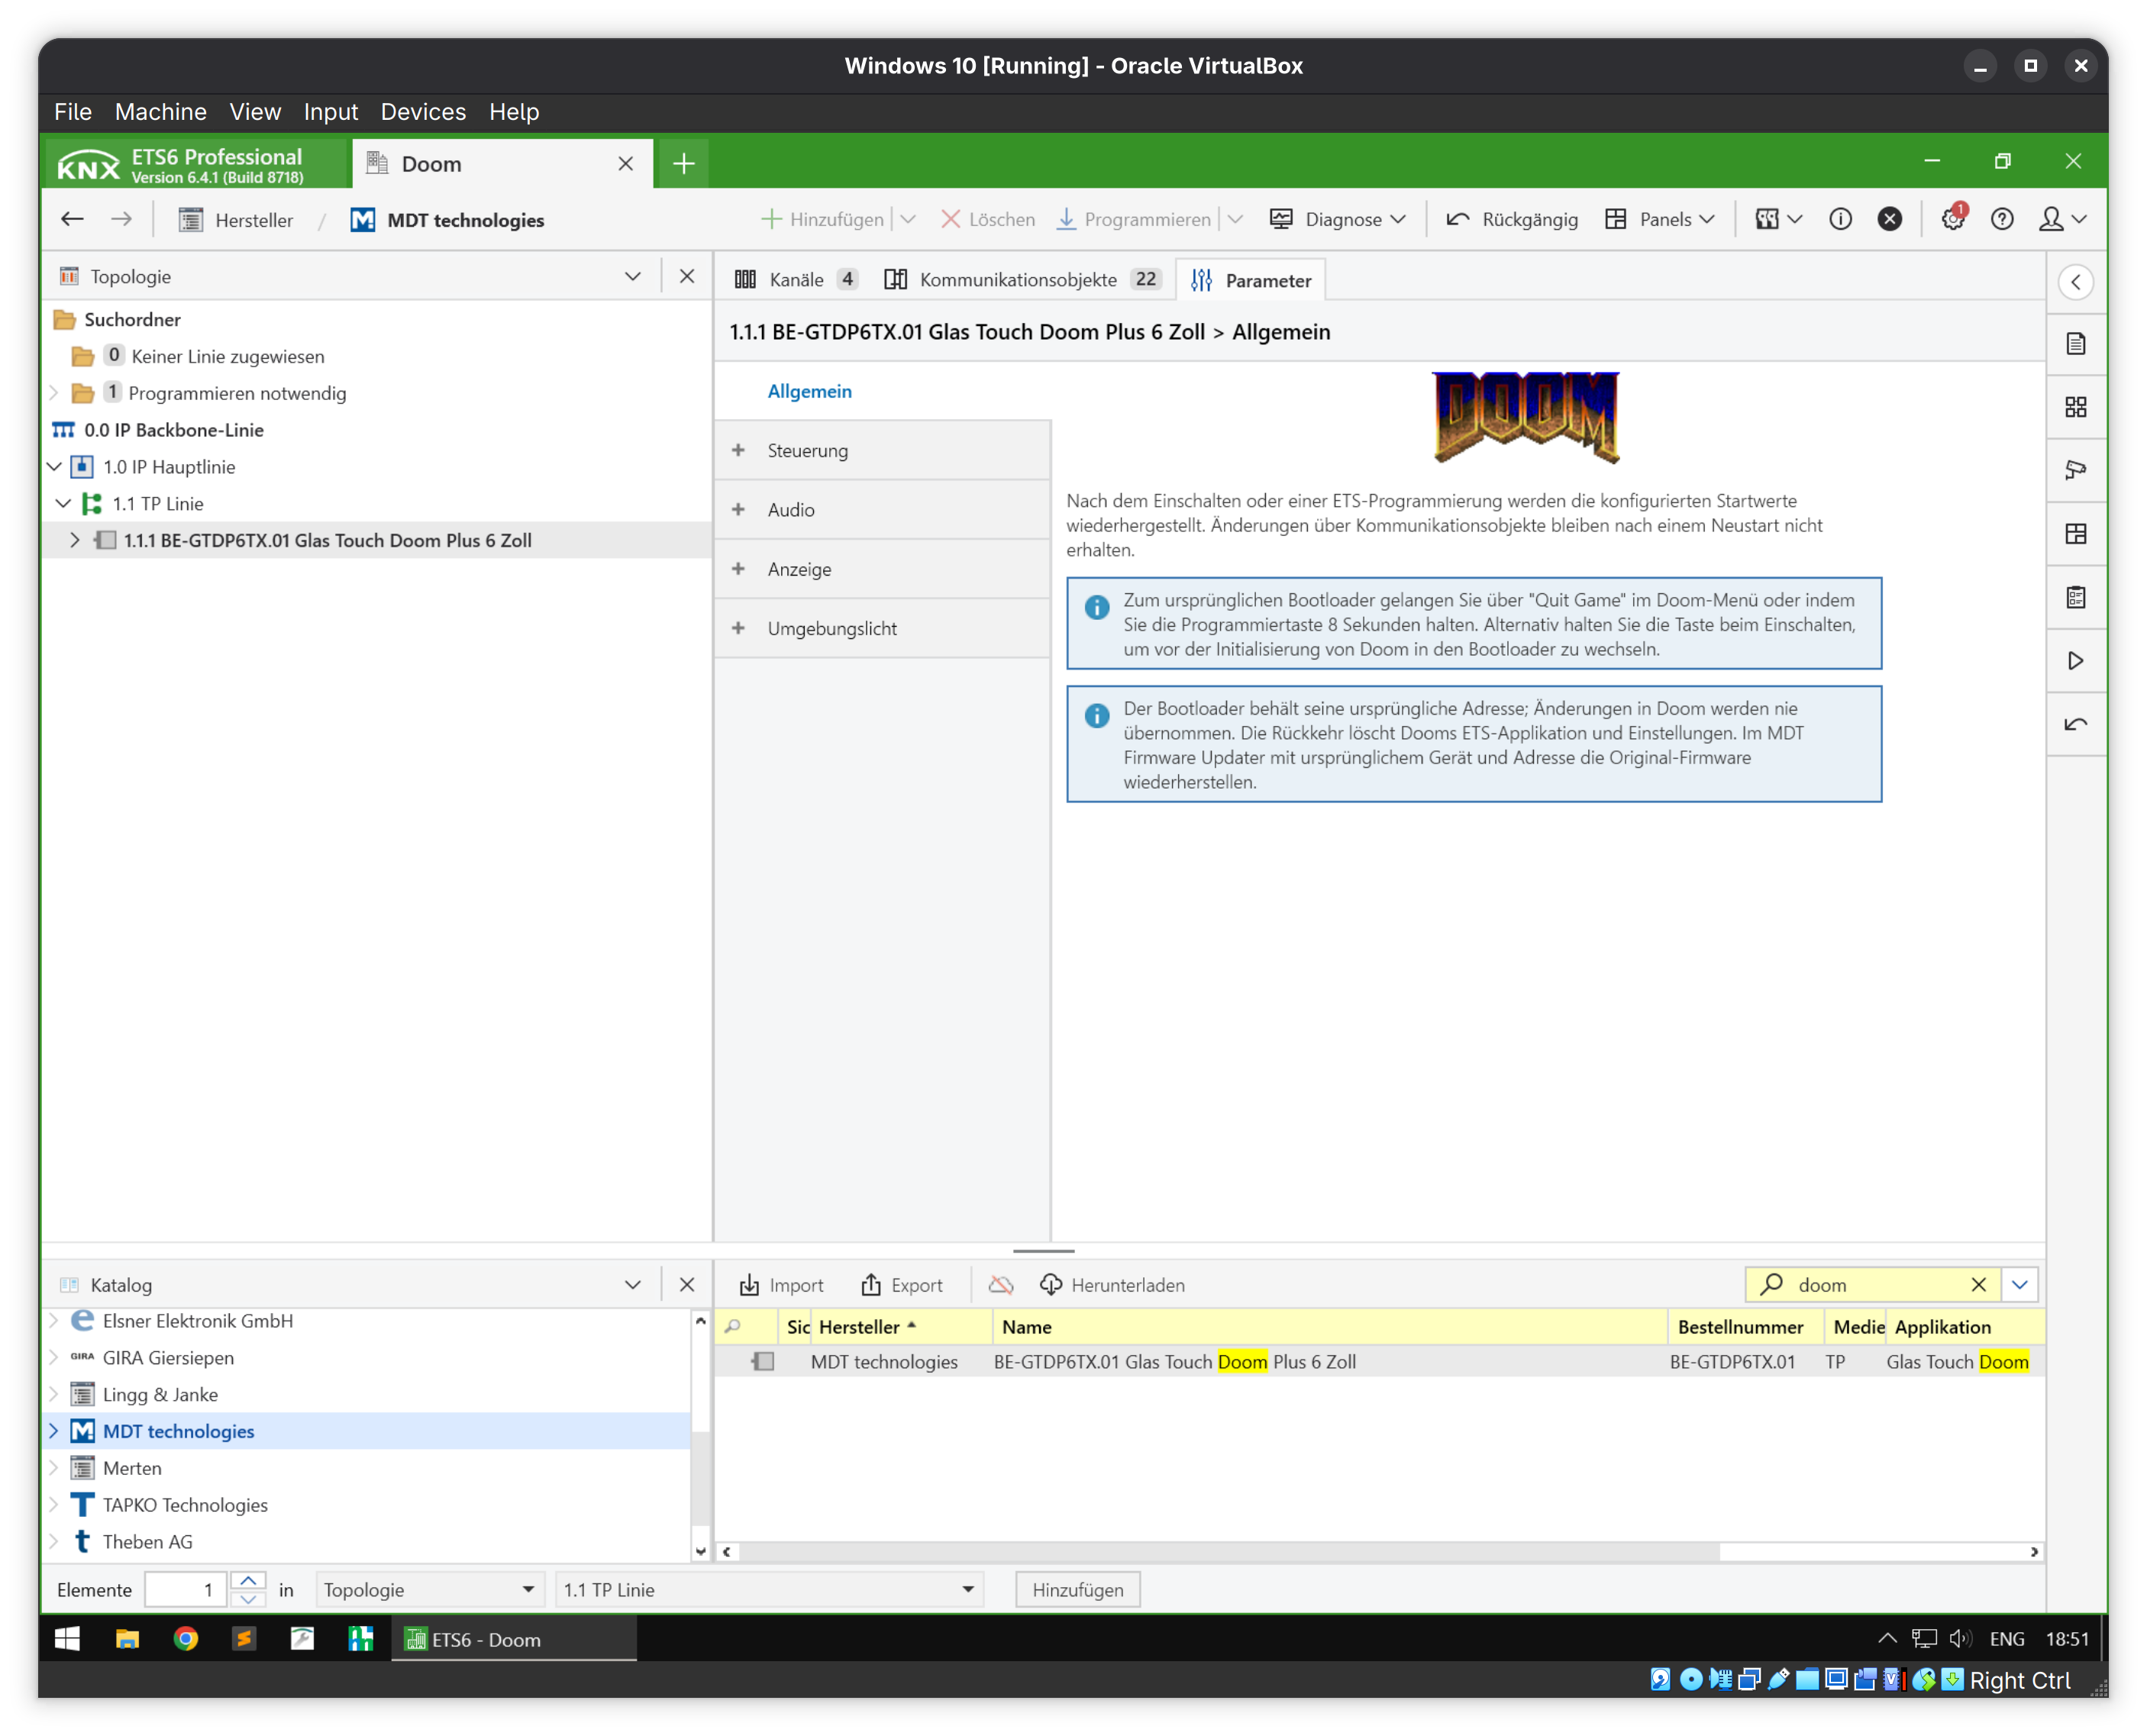
About a month ago, I finally finished my port of Doom to a MDT Glass Touch Smart Plus 6 inch KNX "light switch".
I had to massively overclock the SoC in there to overclock a single lane SPI bus towards the frame buffer IC that drives the enormous 1440x720 pixel screen at reasonable frame rates for it to be playable. The frame buffer has no hardware scaling, so we are copying a few lines around for vertical scaling using its pixel blitting engine.
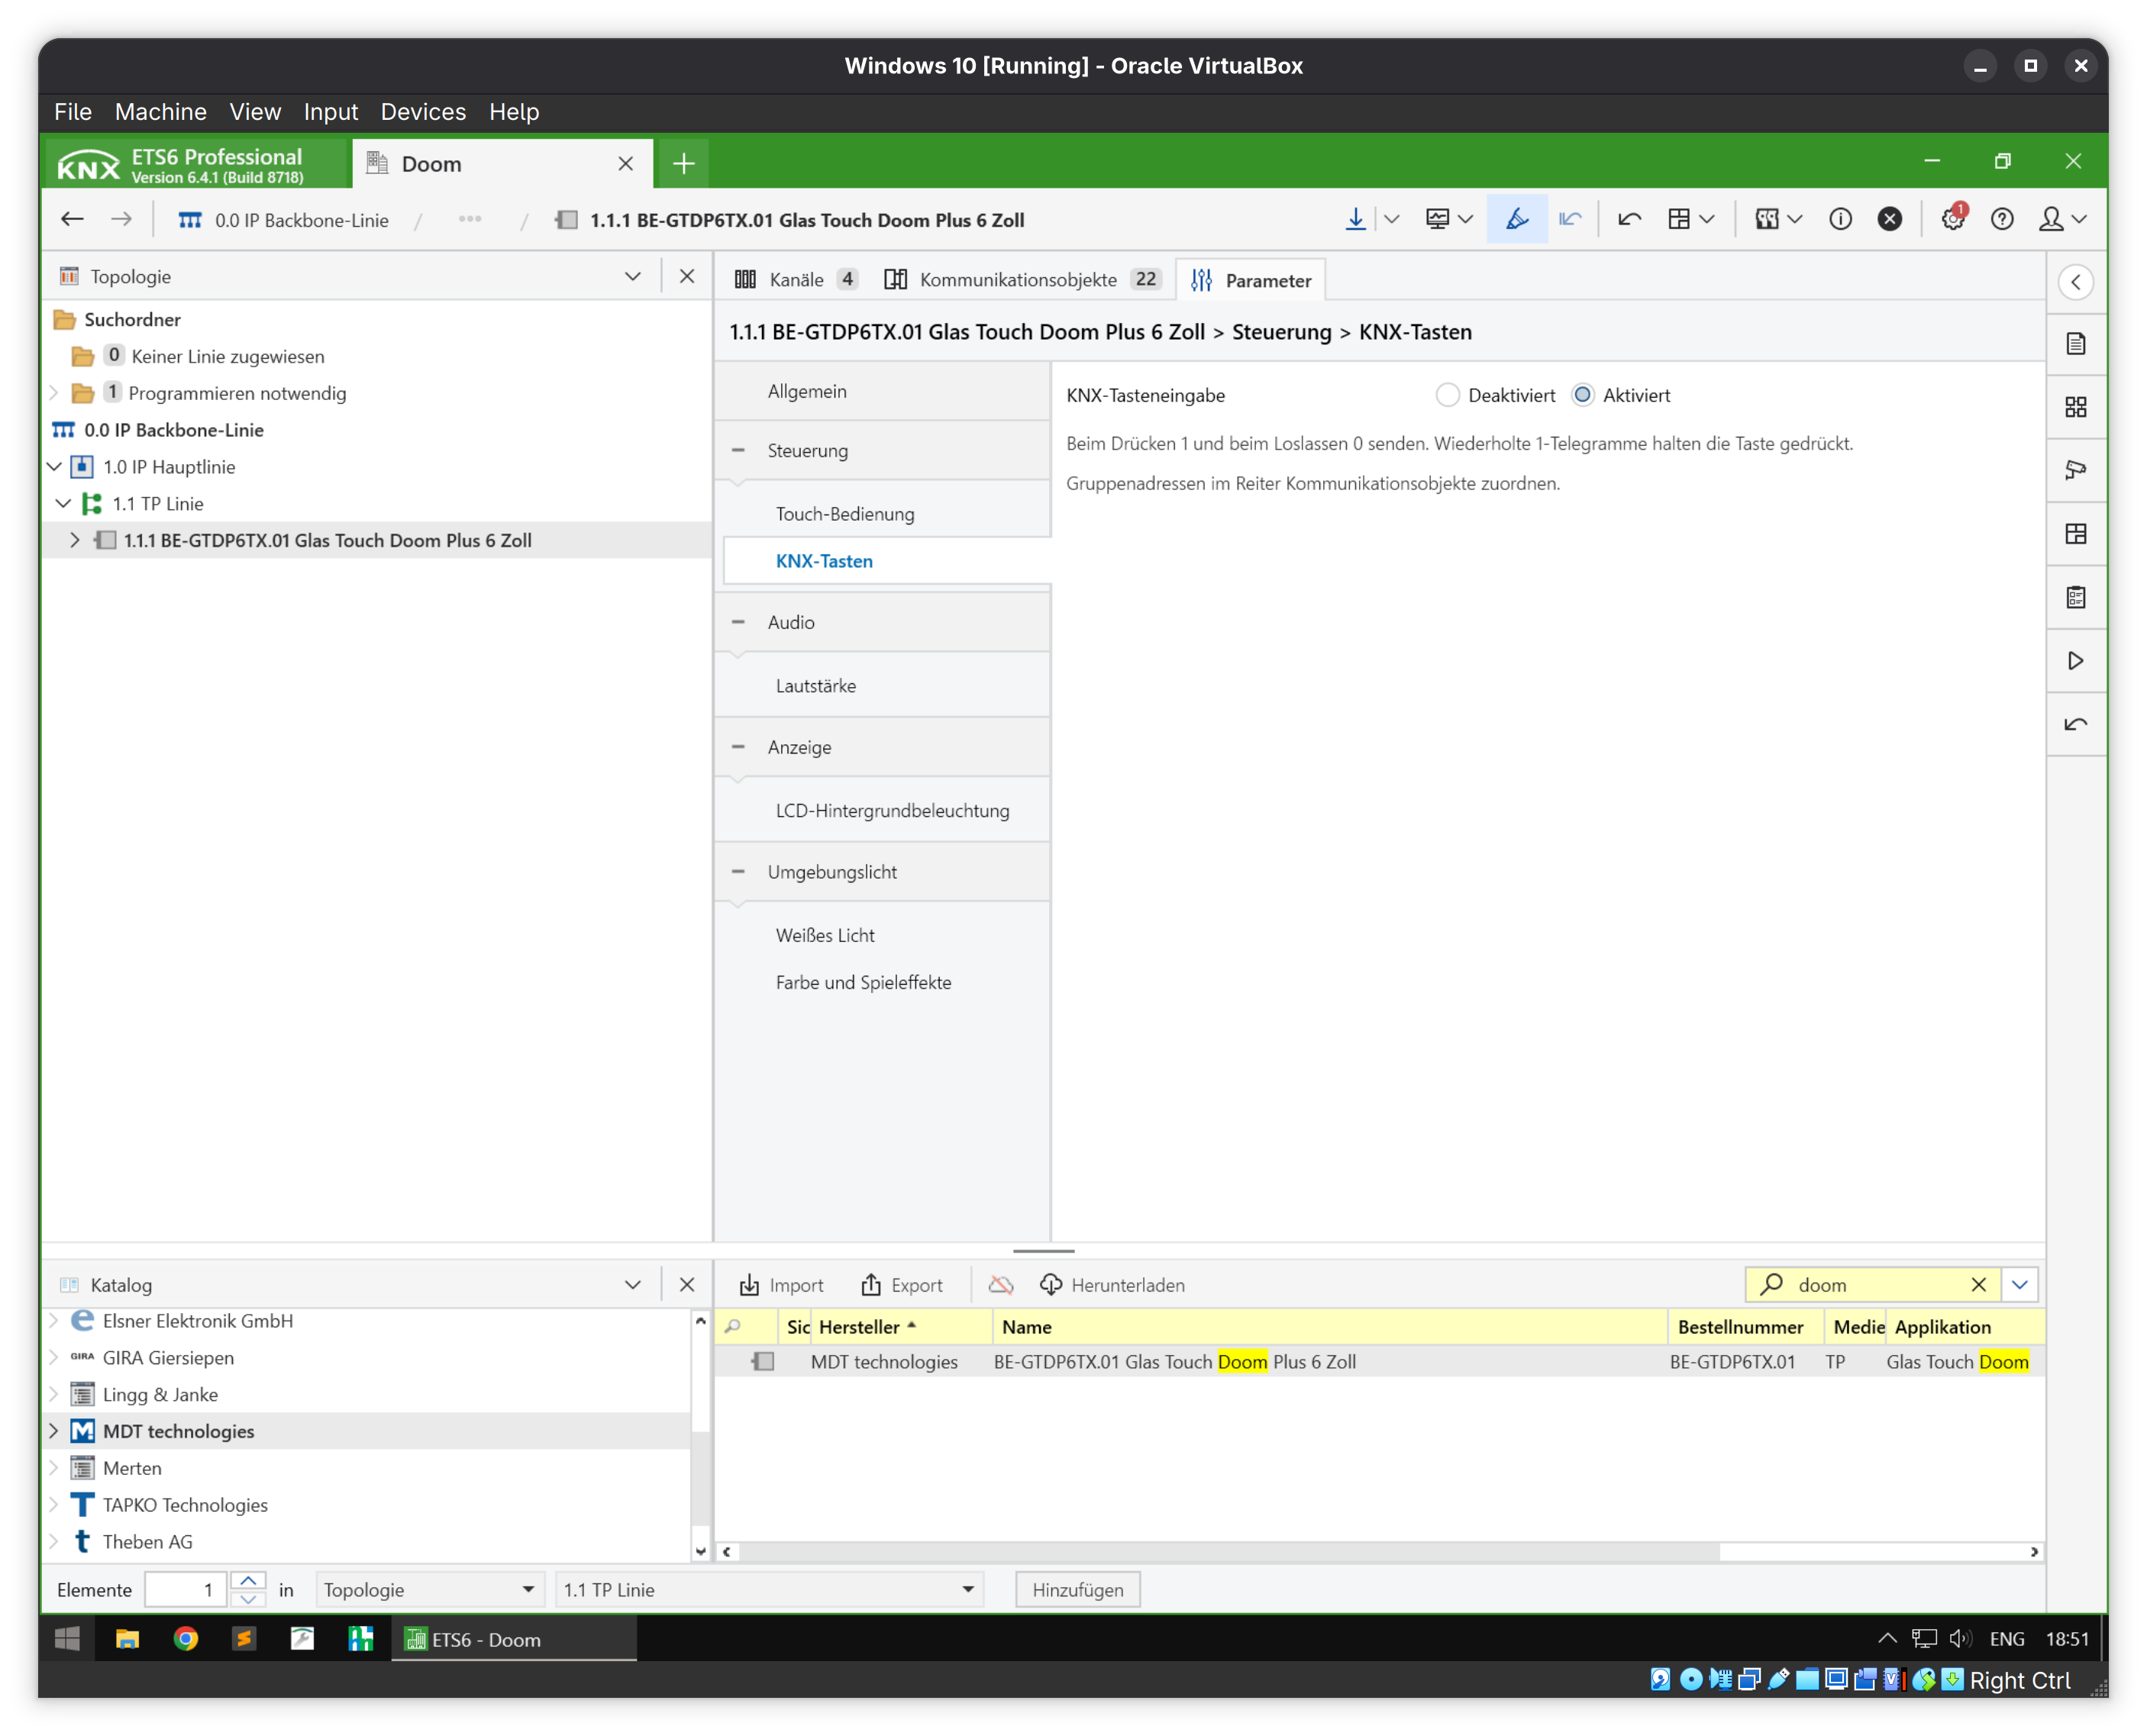
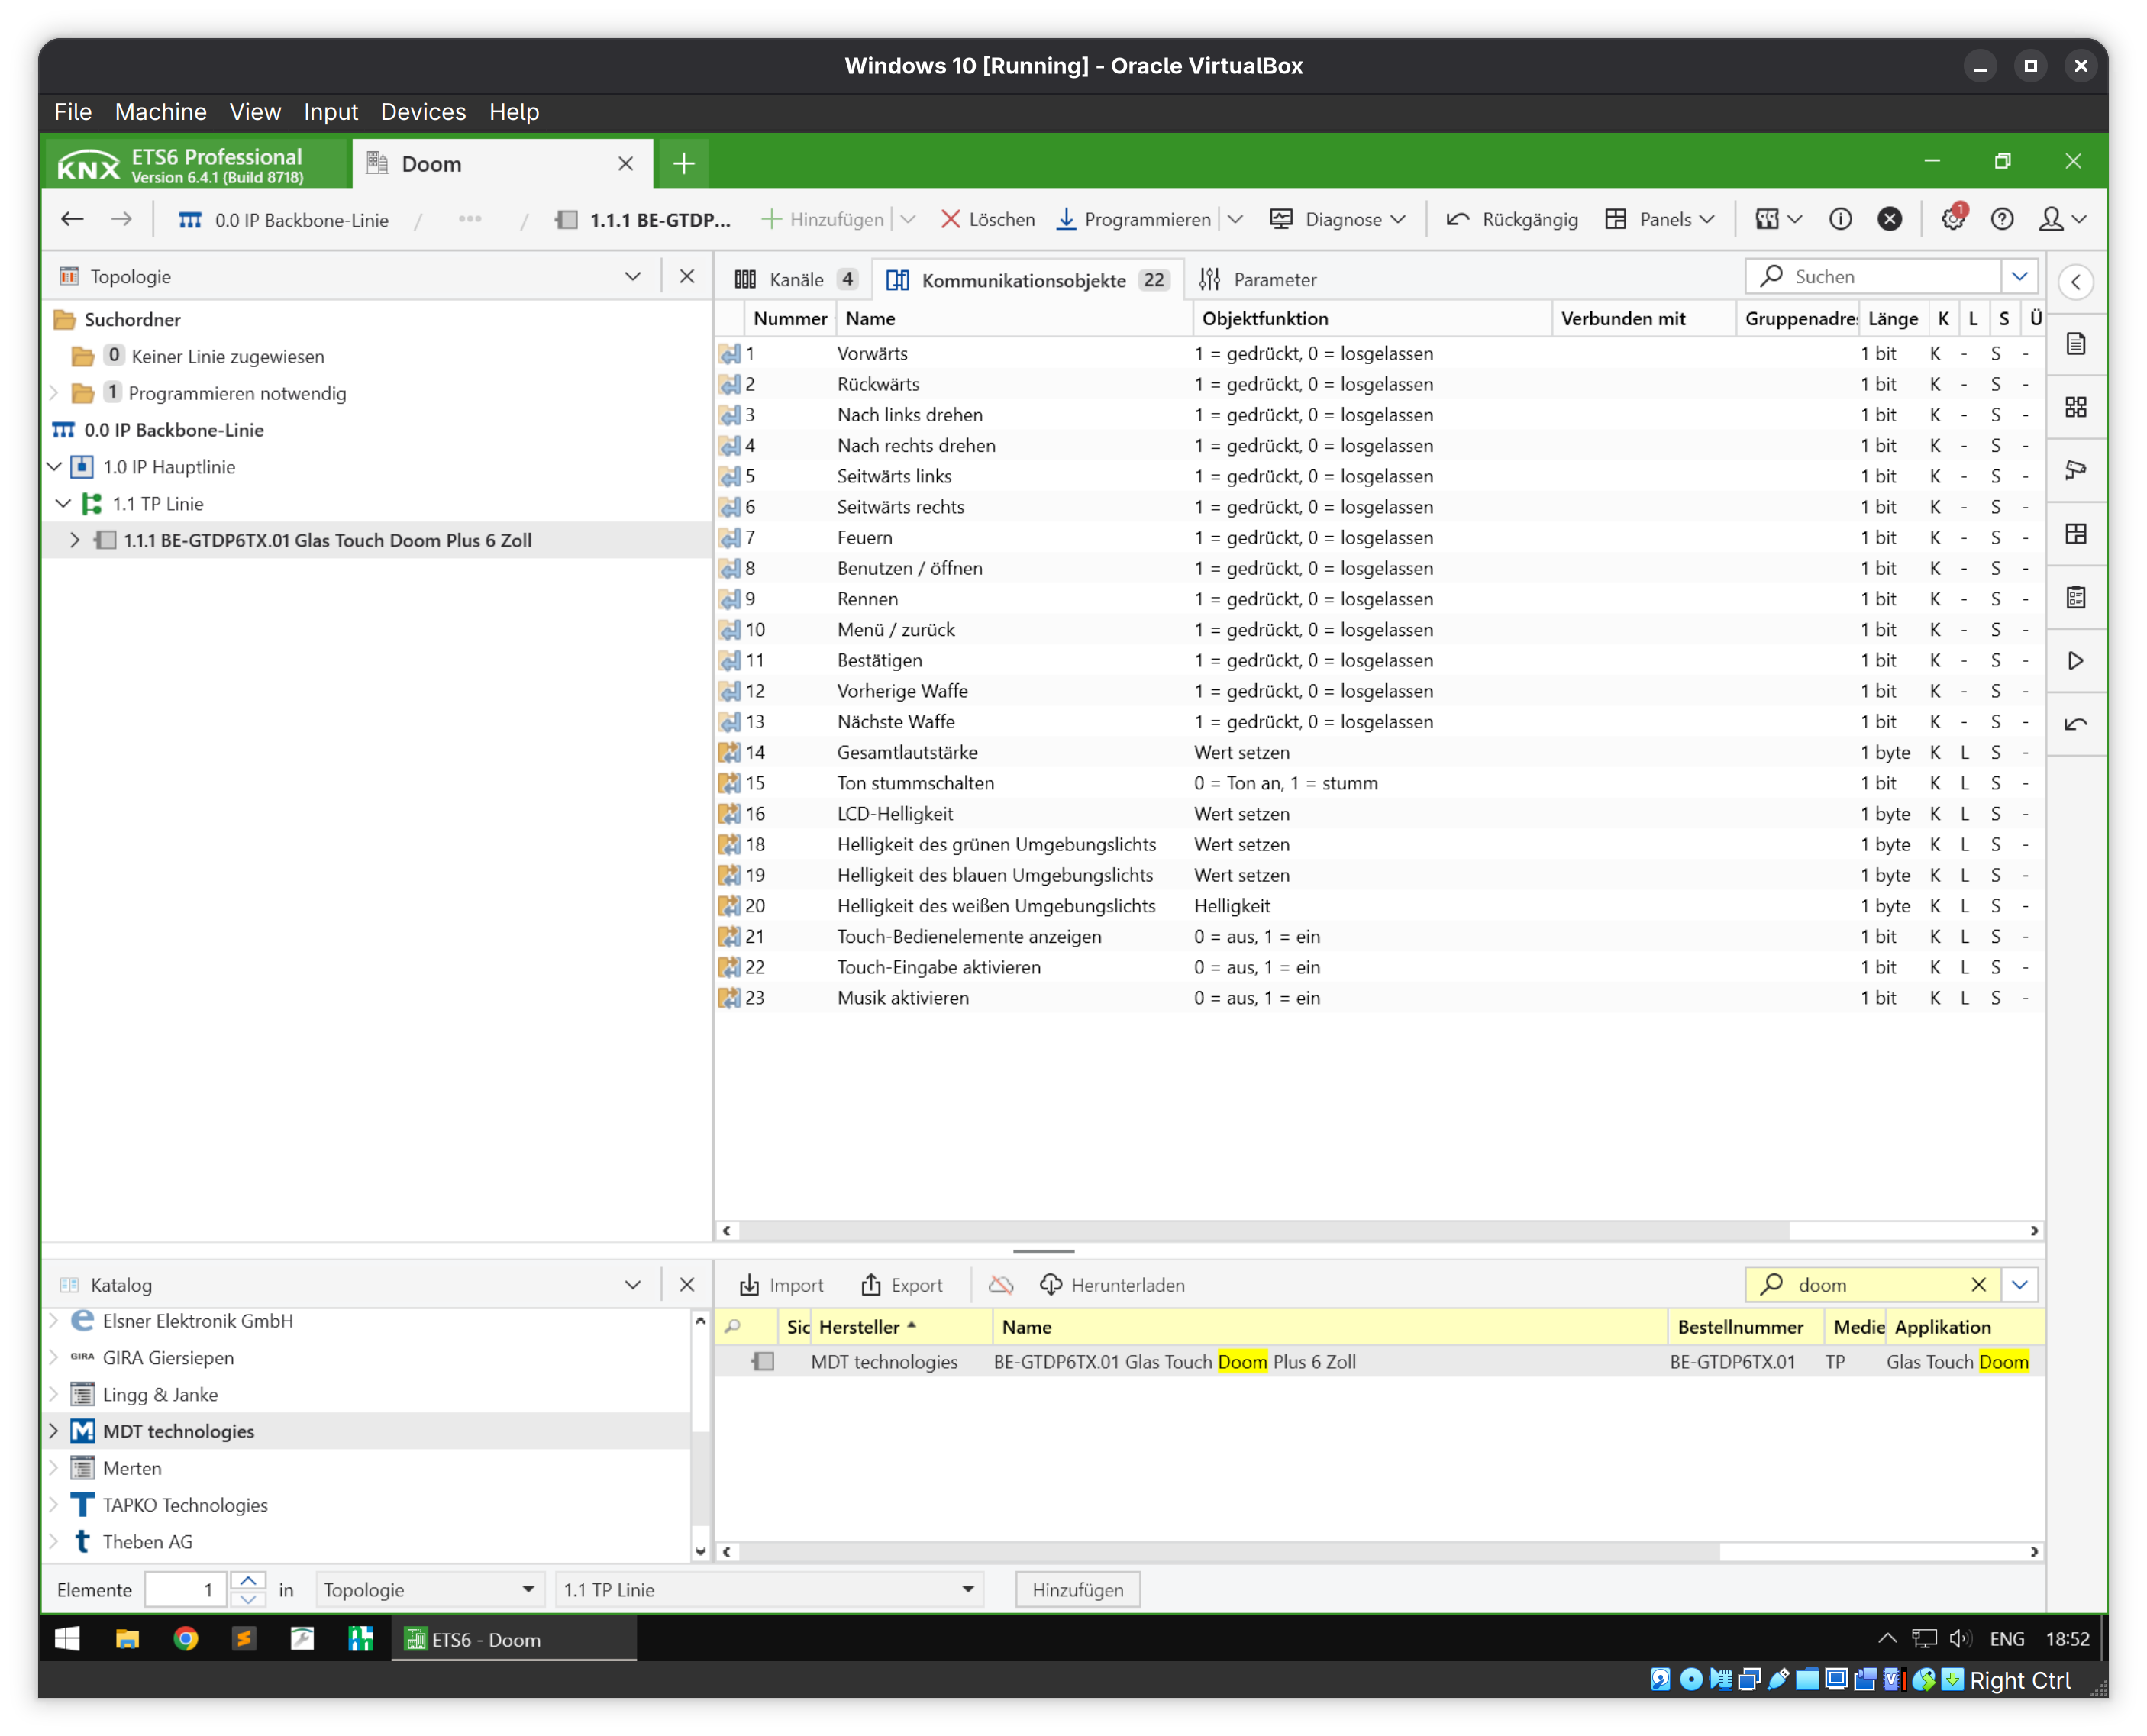
Since this thing is a KNX device, I also ported over my zweidraehte KNX stack and made this a real device. The "input device" I am using is a regular MDT push button lite that just sends button presses over the KNX bus to Doom to use it as a controller. The whole thing is configurable via the ETS and it has its own product database for this. You can not only control input via KNX but also volumes, LCD brightness and other stuff of the game.
Of course, sound and touch screen support is also there. The switch has an ambient RGBW LED light ring around its screen which lights up in red for a short moment if you get hit - it's just not in the video.
The port is based on rp2040-doom by kilograham that has a further optimized WAD/WHX format so everything fits in 2MiB of flash including the KNX stack.
The firmware itself is disguised as a proper MDT firmware update and can be loaded via their own firmware update utility over the KNX bus just like regular updates. Just a bit of trolling on the side.
I sent this over to my contact at MDT and they liked it. However, we are not sure if we should actually release it and how as there are open questions about licensing and potential leaks of IP etc. and I don't want to piss off MDT completely, so for now there's only the video.
Claude found the seeds used for ECDSA; interesting but no action required by anybody https://www.anthropic.com/research/ecdsa-curve-origins
Dumping Encrypted Viltrox Lens Firmware - two times https://blog.29b.net/dispatches/viltrox_re/
Two lenses, two different microcontrollers, two different readout bypass exploits, and two different e-mount implementations.
Wie ich mit LLMs rede, wenn sie nicht tun, was ich von ihnen will: https://www.youtube.com/watch?v=CwE4mk2fbow
Everyone needs to see this and also acknowledge why reverse engineering is a super power.
Credit to https://instagram.com/ayoships
Guy reverses the dark patterns of mobile apps and publishes it, absolutely love it!
Okay, after reading an installation tutorial, it seems that it touches the security sectors on the HDD and it also reflashes the SMC, so something wonky is going on.
The SMC has been used in the JTAG exploit to set up DMA transfers from NAND to RAM in the past. Just triggering the final read wasn't possible from the 8051 core, so that's why this trigger happened by writing the right registers over the GPU's JTAG port.
Maybe it's something similar, just that the trigger or destination address for a DMA READ comes from the race?
I'm kinda curious how the Race and DMA Attack in the Xbox 360 Peer Pressure exploit works. But there's neither a writeup, nor is it open source to read up on it. Sad.
I am too old to reverse engineer things from "the scene".
Panoramapotentiometer
https://www.youtube.com/watch?v=LMm4KXLllzI
A 19-year-old walked through Helsinki airport in April 2026 carrying two 2TB hard drives and a ticket to Japan.
He couldn’t make that flight.
Finnish police stopped him on an Interpol Red Notice, and by July, US prosecutors had unsealed a federal complaint identifying him as Peter Stokes,
an alleged member of the Scattered Spider hacking group, wanted over a May 2025 breach of a US luxury jewelry retailer that ended in an $8 million ransom demand.
No, we haven’t suddenly turned into a crime reporting publication,
but it was Microsoft that handed the FBI a way to trace Stokes’ Windows PC across VPNs, proxy servers, and three countries.
The tool is called a "Global Device Identifier", or GDID,
and outside a handful of enterprise documentation pages, most Windows users had never heard the term before this case made it public.
We went through the full 39-page complaint,
cross checked it against independent reverse engineering of how Windows generates and transmits this identifier,
and fact checked the technical claims since the story broke.
Here is everything you need to know about #GDID,
how it caught Stokes,
and what it means if you are one of the 1.6 billion people using Windows PCs
I'm living in a pretty much airtight KfW 55 house. More airtight than it needs to be for the energy savings classification.
I turned off the forced air circulation this morning because of construction work on our street and potential ingestion of exhausts. The excavator was working right next to our fresh air intake. I completely forgot to turn it on again later and just checked the CO2 level in my office: 1600ppm. Oops.
In all fairness, I don't think it's that high, because it's one of those weird eCO2 sensors that measures everything but actual CO2 and then does a bit of magic math to guess. But still, the air inside is complete trash after a day without circulation.
The fuck is Spider-Noir? I lost track of all the different Spodermin universes by now to be honest.
The solution: Download a random ass .pkg file from somewhere to install gstreamer. Then download a random ass .tar.xz containing a macOS App Bundle built by some rando on the Internet. The only thing missing is these two files being called setup.exe.
Before running both, tell gatekeeper to shut the fuck up and just let me run it.
Way better! Much security! Many user friendly. 🤡
Error: wine-stable: Cask 'wine-stable' has been disabled because it does not pass the macOS Gatekeeper check! It was disabled on 2026-09-01.
Yeah, fuck you too! Why is it, that proprietary operating systems constantly have to babysit and nag the user? Now what? Do I need to compile wine myself just to get it working on macOS?
I'm using this OS for 10 minutes and I'm already pissed at it.
"You will own nothing and be happy"
Companies: "Fuck yeah!"
People: using AI to reverse engineer every software under the sun
Companies: "No! Not like that!"
The best video I have ever seen about how LLMs actually work and how they have been developed (including relevant papers):
Yeah, the functions I call usually have at least 115 arguments as well!
https://github.com/OpenCourant/OpenCourant/blob/main/engine/source/airbag/fvbag0.F#L250-L298
OpenRadioss (the thing Siemens wiped off GitHub) is written in Fortran. The code looks wild. A real blast from the 80s. The only thing missing are the punch cards.
Hey Team, quick one before the weekend: