Oct 20, 2026, 3:57 PM
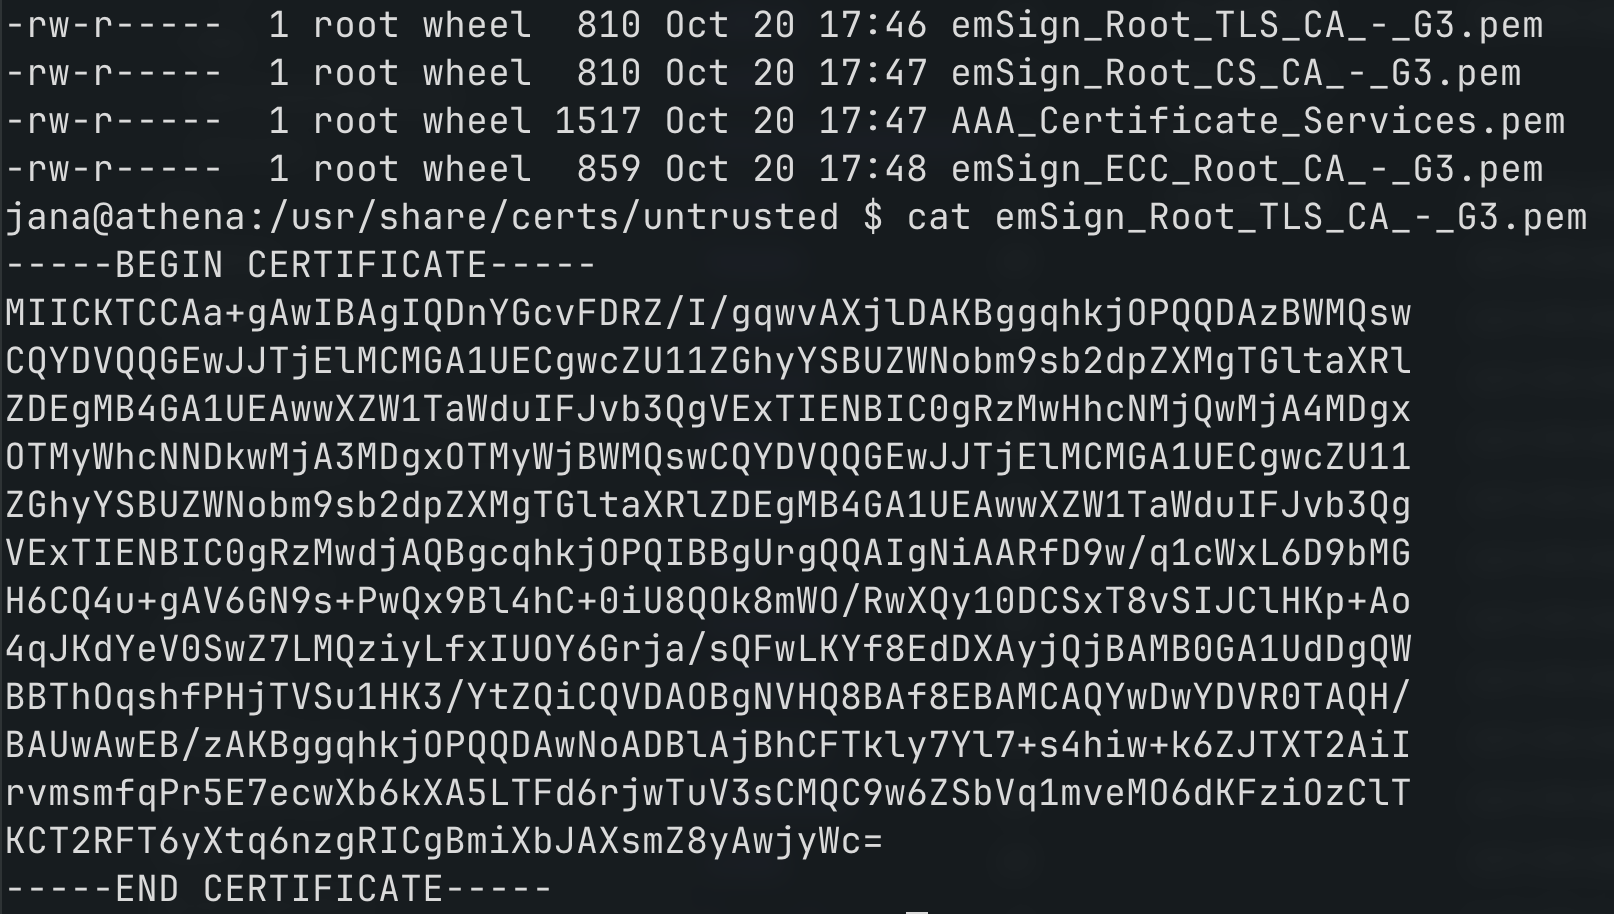
So if anyone on FreeBSD is wondering how to untrust the leaked CAs now:
- Go to
/usr/share/certs/untrusted - Create a new file for each root, with the cert info (Can be found here: https://emudhra.we-have-a-problem.com/roots.json)
- Run
certctl rehash
Same for jails, I copied the files into my Jail base release and ran a quick rehash in all of the.
EDIT: Patch is now available https://www.freebsd.org/security/advisories/FreeBSD-SA-26:73.caroot.asc