Login
You're viewing the functional.cafe public feed.
  • Nov 20, 2026, 4:32 AM

    so, fun fact about the Linux NFS client: if you enable sec=krb5p, expecting that to encrypt the data being written on the mount, it will actually do all the writes using krb5i, so they aren't encrypted.

    discovered by Linux being unable to write to a FreeBSD NFSv4 export that requires krb5p.
    💬 1🔄 1⭐ 0

Replies

  • Nov 20, 2026, 5:39 AM

    @lw Is there an issue with a ticket on the client or somesuch? Ought to be able to do krb5p.

    I saw a StackOverflow discussion that mention also saying -o sec=krb5p when mounting explicitly... What happens if you throw that in? I'd assume if it can't actually agree on a key to encrypt it'd fail outright, but this is a guess. I'd be curious to know if it does anything though.

    💬 1🔄 0⭐ 0
  • Nov 20, 2026, 5:43 AM

    @mason no ticket that i'm aware of.

    it's a little bit more complicated than my brief description suggested: essentially, it tries to negotiate SP4_MACH_CRED so it can use the machine credential instead of the user credential for certain operations (e.g., flushing data from the page cache after the user's ticket expires) and it uses krb5i for that.

    but for whatever reason, if the server allows SP4_MACH_CRED for WRITE ops, which FreeBSD does, Linux then uses it for *all* writes, even if it could use the user credential.

    💬 1🔄 0⭐ 0
  • 💬 1🔄 0⭐ 0
  • Nov 20, 2026, 7:50 AM

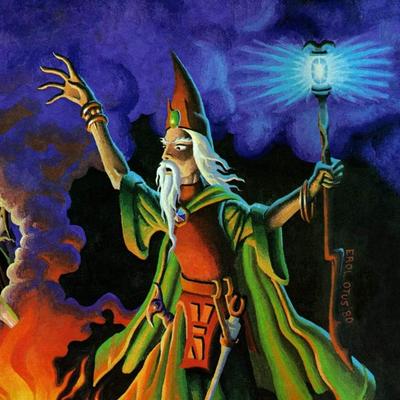
    @mason this is pretty trivial to reproduce because you can just see the data going over the wire in plaintext, but let me know if i can provide any other info.

    server is FreeBSD 15.1, client is Fedora 45 (7.3.3-300.fc45), the client mounts the filesystem with rw,sec=krb5p,nconnect=8,bg.

    Image attached toot
    💬 0🔄 0⭐ 0