Login
You're viewing the functional.cafe public feed.
  • Nov 15, 2026, 9:11 AM

    2030 is now a deadline in Europe and the USA.

    Late in October, the American NIST published the final version of NIST IR 8547, the report defining how to transition to post-quantum cryptography. Compared with the November 2024 draft, the report is now tied to Executive Order 14412 and OMB Memorandum M-26-15.

    By December 31, 2030, US federal agencies will be required to adopt post-quantum key establishment on their most sensitive systems, and by December 31, 2031, post-quantum signatures.
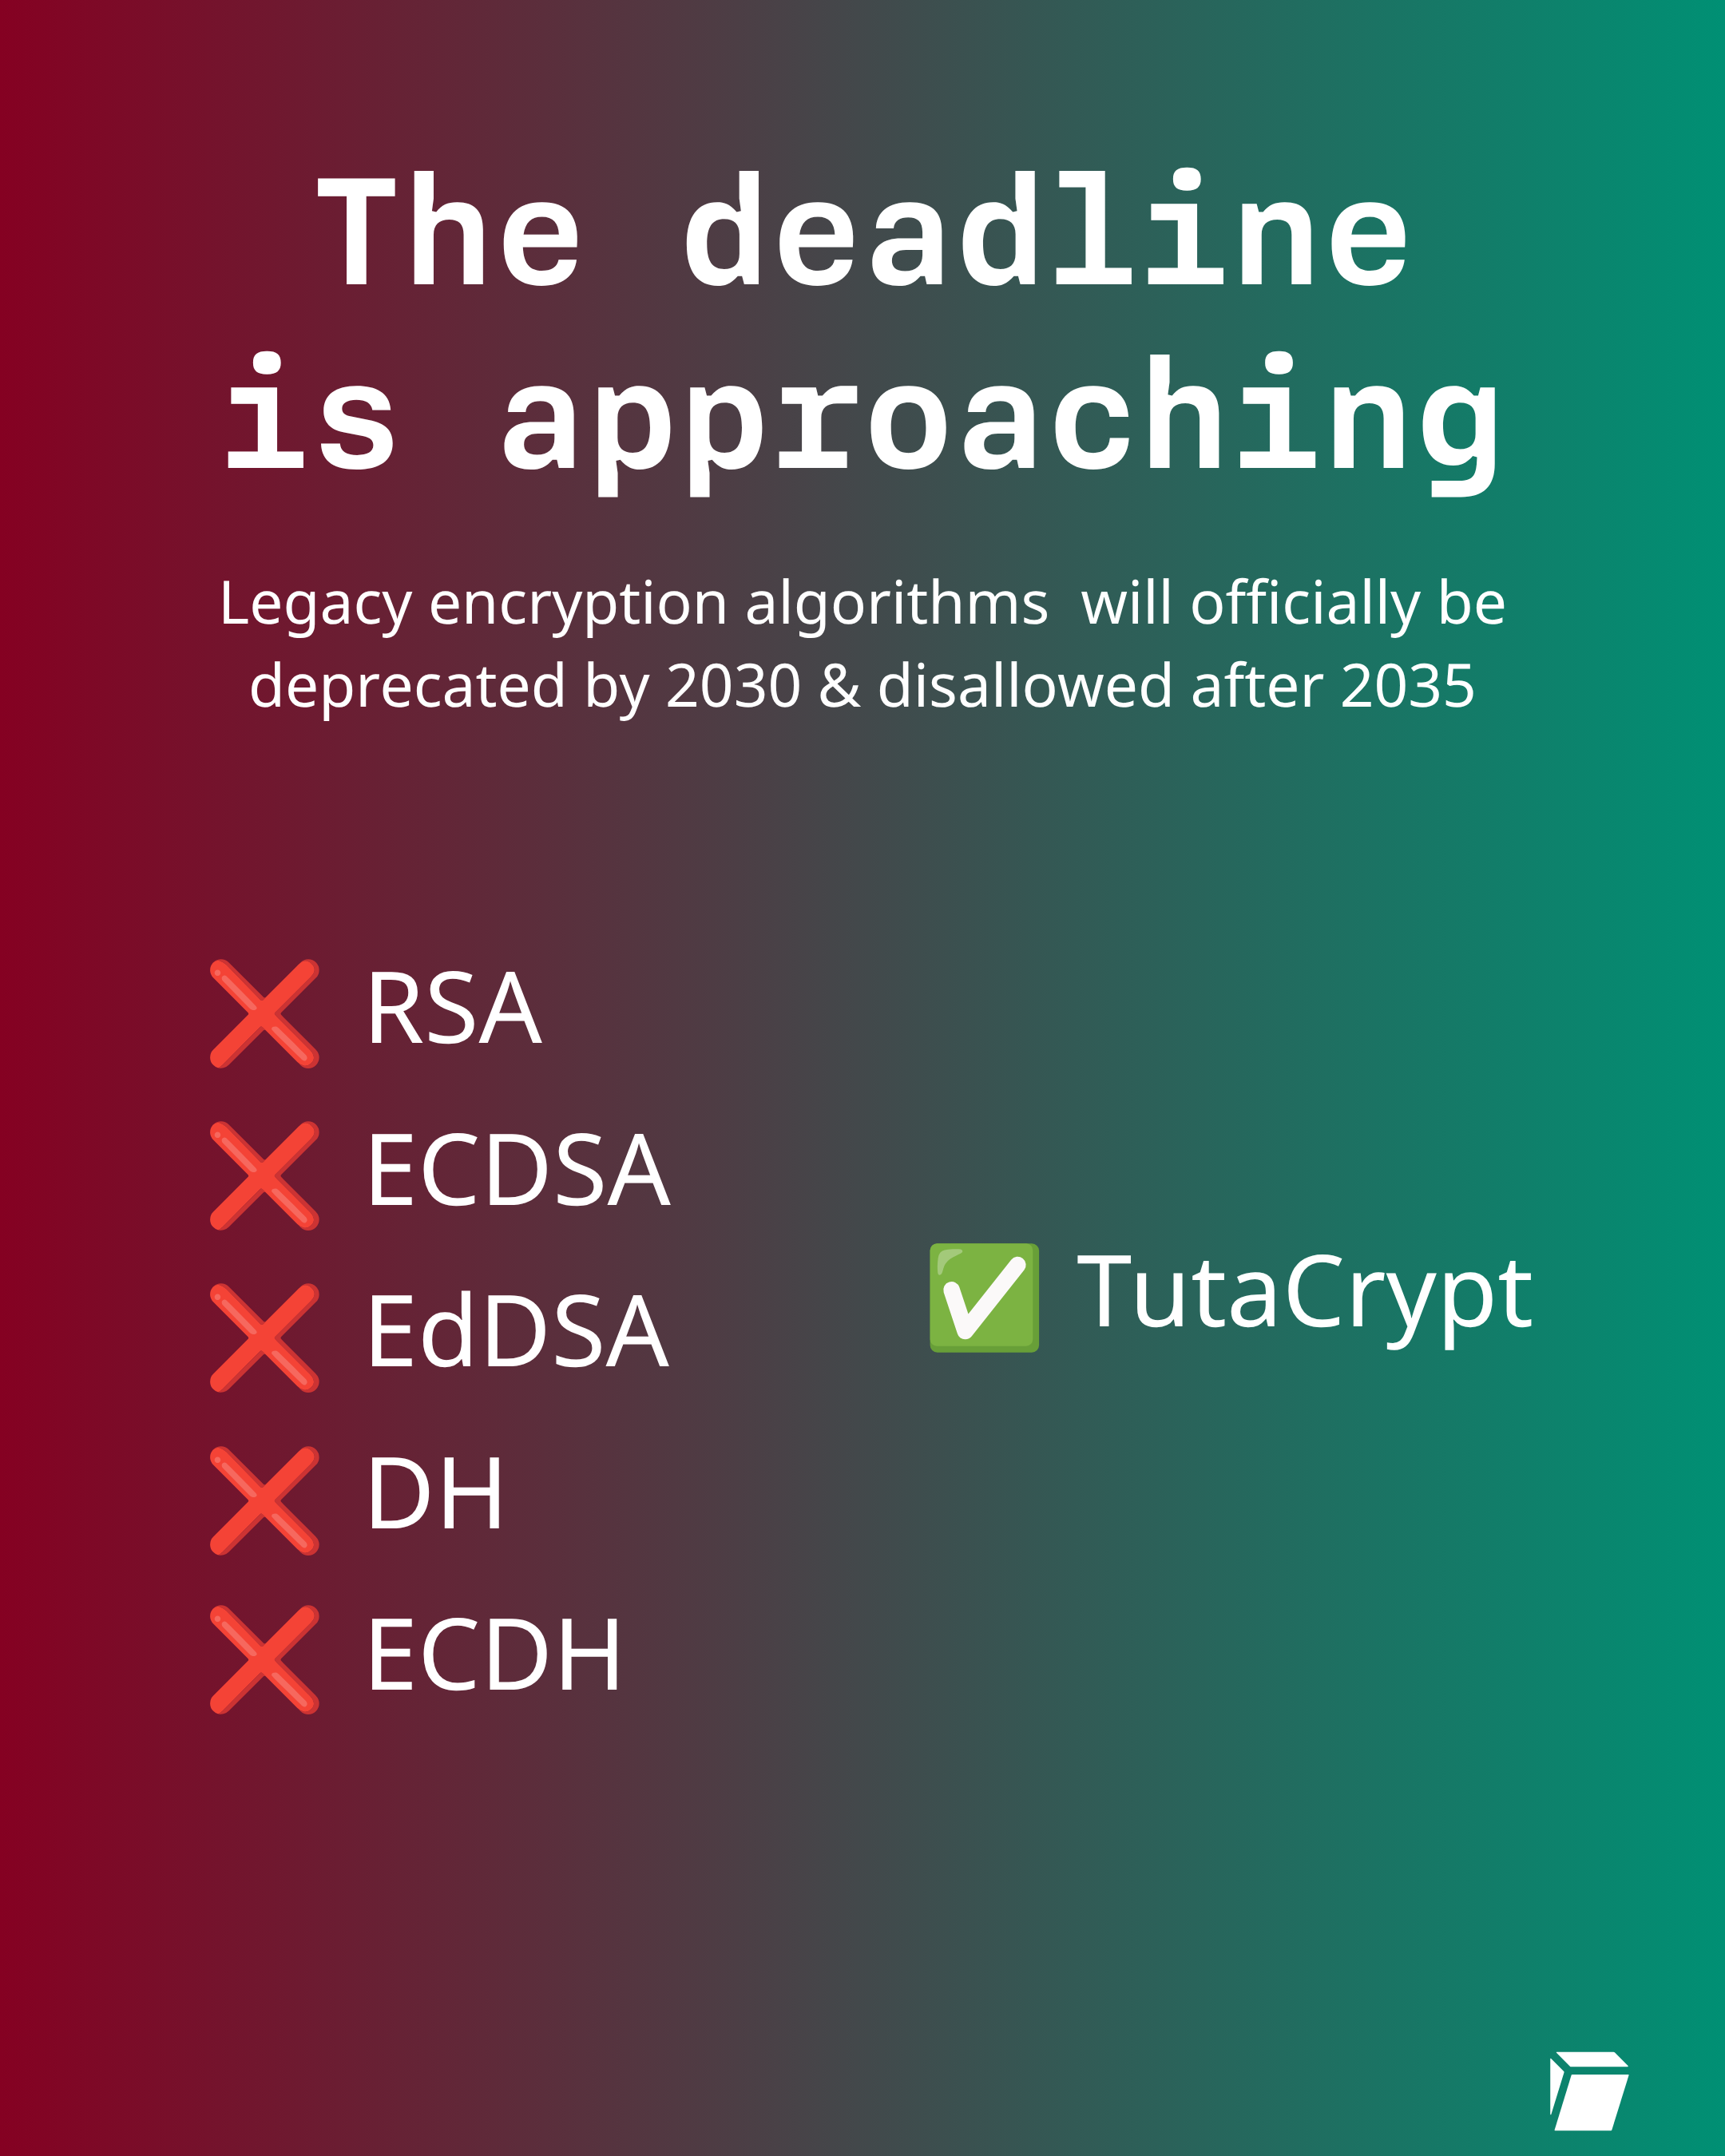
    The title of the image reads: The deadline is approaching. The subtitle reads: Legacy encryption algorithms will officially be deprecated by 2030 & disallowed after 2035. On the left are five red crosses next to the terms: RSA, ECDSA, EdDSA, DH and ECDH. On the right is one green ticked box next to: TutaCrypt.
    💬 1🔄 1⭐ 0

Replies

  • Nov 15, 2026, 9:13 AM

    Europe had already published similar plans.

    🔹 The NIS Cooperation Group recommends that Member States complete the transition of high-risk use cases by the end of 2030.

    🔹 In Germany, the renowned BSI security roadmap targets post-quantum cryptography for critical infrastructure by the same date.

    The final report also hardens NIST’s own schedule: all RSA and elliptic-curve algorithms are deprecated after 2030 and disallowed after 2035, regardless of key size.

    💬 1🔄 1⭐ 0
  • Nov 15, 2026, 9:13 AM

    For European organizations, the US obligations are not binding, but they will be felt. Many of the libraries, HSMs and network products used in Europe follow NIST standards and FIPS 140 validation, and vendor roadmaps will align with the federal deadlines.

    So, 2030 is now the benchmark against which post-quantum migration plans will be measured, no matter where an organization is based.

    We at Tuta are ready for this change! Read more on TutaCrypt ⤵️

    tuta.com/blog/post-quantum-cry

    💬 1🔄 3⭐ 7
  • 💬 0🔄 3⭐ 2