Login
You're viewing the front-end.social public feed.
  • Sep 13, 2026, 12:03 PM

    Triaged a large batch of issues found by a zkao.io scan. Some good bugs, but no vulnerabilities. (LLMs are especially bad at telling those apart.)

    One or two of the math/big ones would have been vulns, but we finished moving math/big out of crypto a couple years ago! 🏁

    LLMs found zero (0) vulnerabilities above SEV:LOW in Go crypto so far 💁‍♂️ 💅

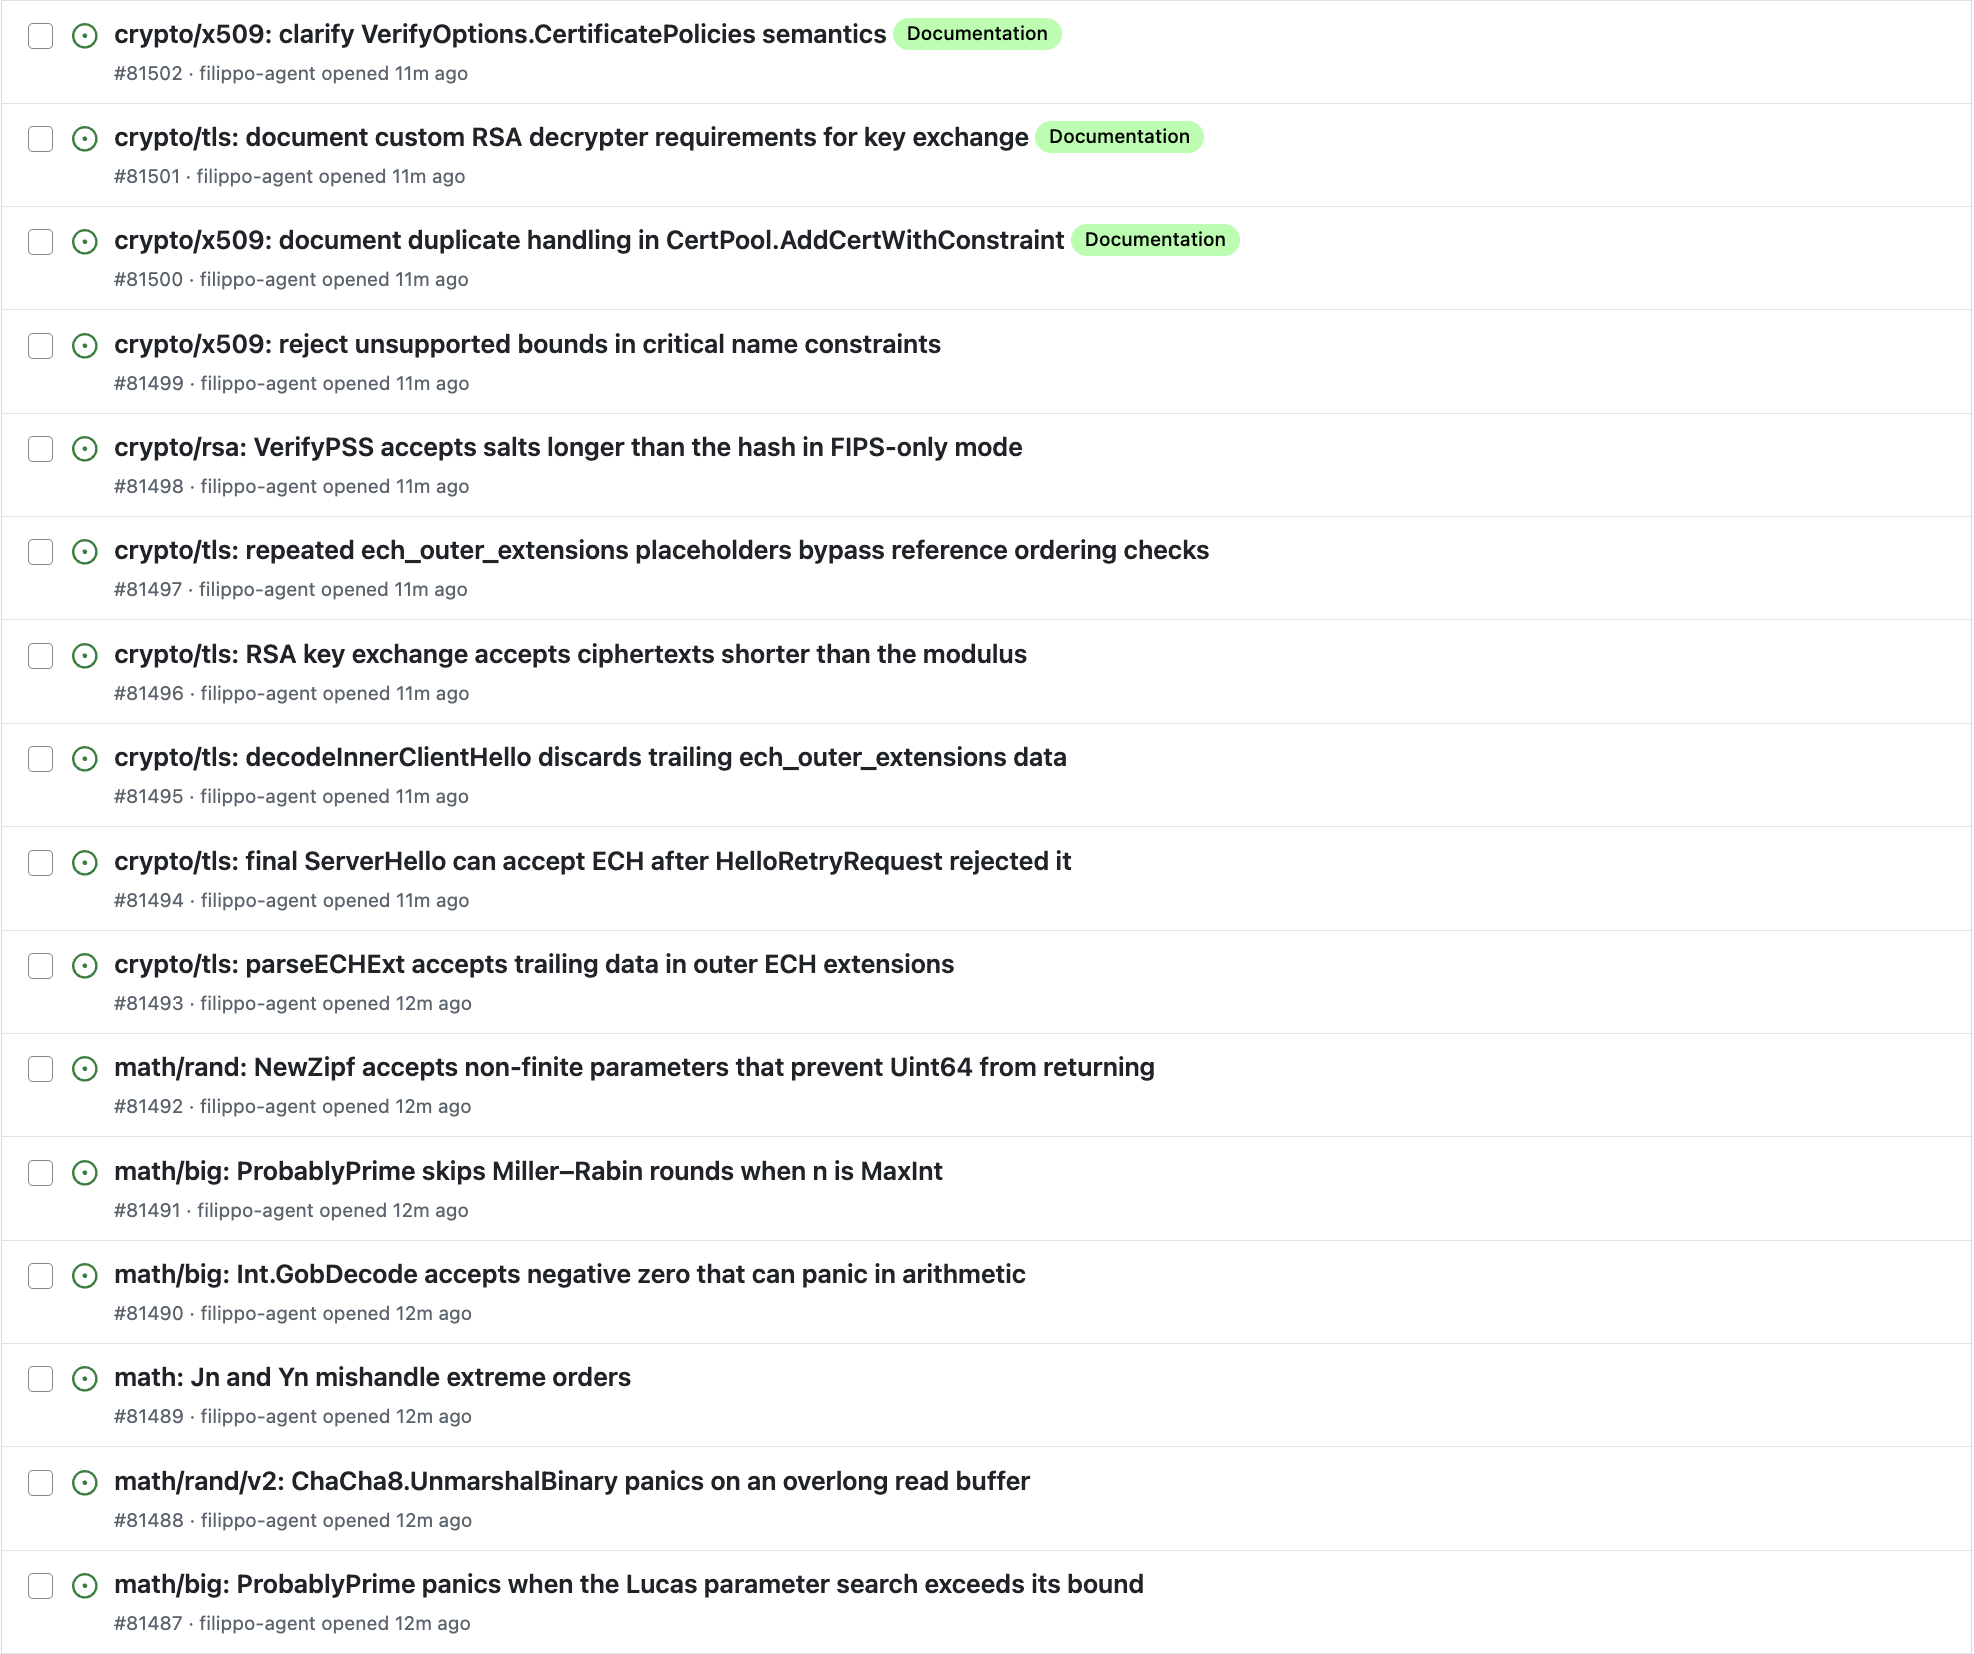
    a long list of freshly filed issues:
#81502 crypto/x509: clarify VerifyOptions.CertificatePolicies semantics
#81501 crypto/tls: document custom RSA decrypter requirements for key exchange
#81500 crypto/x509: document duplicate handling in CertPool.AddCertWithConstraint
#81499 crypto/x509: reject unsupported bounds in critical name constraints
#81498 crypto/rsa: VerifyPSS accepts salts longer than the hash in FIPS-only mode
#81497 crypto/tls: repeated ech_outer_extensions placeholders bypass reference ordering checks
#81496 crypto/tls: RSA key exchange accepts ciphertexts shorter than the modulus
#81495 crypto/tls: decodeInnerClientHello discards trailing ech_outer_extensions data
#81494 crypto/tls: final ServerHello can accept ECH after HelloRetryRequest rejected it
#81493 crypto/tls: parseECHExt accepts trailing data in outer ECH extensions
#81492 math/rand: NewZipf accepts non-finite parameters that prevent Uint64 from returning
#81491 math/big: ProbablyPrime skips Miller–Rabin rounds when n is MaxInt
#81490 math/big: Int.GobDecode accepts negative zero that can panic in arithmetic
#81489 math: Jn and Yn mishandle extreme orders
#81488 math/rand/v2: ChaCha8.UnmarshalBinary panics on an overlong read buffer
#81487 math/big: ProbablyPrime panics when the Lucas parameter search exceeds its bound
    💬 0🔄 0⭐ 0