Dekkiadekkia
7/16/2025I'm not naming any names while I play around with it.
When I'm done or the thing is offline I will.
I'm not naming any names while I play around with it.
When I'm done or the thing is offline I will.
They're using a PhisKit to do the heavy lifting.
The email-address of the author is still in there and I found a Portuguese security website talking about similar scams targeting other banks.
They won't let me open debug tools with the normal shortcut.
Had to open them beforehand and then navigate there.
I wonder how well the phishers protect their infrastructure.
The webhoster I contacted on linkedin responded earlier today btw.
Told me they'll look into it and let me know.
Since the inbetween-URL is already in their list, I sent them a request to add the destination domain too.
This time I got a Google Save Browsing When clicking the link.
I didn't even know Firefox hat that.
The WordPress site is offline now.
So they changed to a different vendor and sent out another phishing mail using that one.
Let's see if anything happens.
I'm going to bed now.
Webhosters without abuse contact.
Lovely.
Their only contact-form has mandatory fields like budget. There's no way I'm filling that out.
But they have LinkedIn. Guess I'll contact them there?
Ok, messaged them.
Time to look at wordpress.
There's also an empty WordPress site between the college-website and the phishing-site, but I've yet to look at that one.
Now If one hovers over the link in the email, they see a URL that contains the word bank (because the college has bank in its name)
which probably will make people click on it more likely.
So I gotta contact them as well.
The more interesting thing is that they use the website of a seemingly legitimate online college (which is something different in Germany than it is in the US) as a jump host to the actual phishing site.
I don't want to post the link, but its like <domain.xyz>/login?service=<anotherDomain.xyz>&gateway=true
which then forwards you to <anotherDomain.xyz> when accessing the site.
I contacted the nameserver-hoster and the domain registrar, hoping to get it taken down.
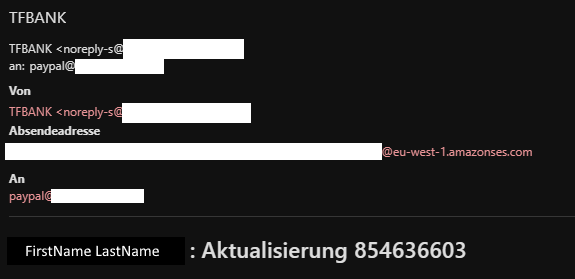
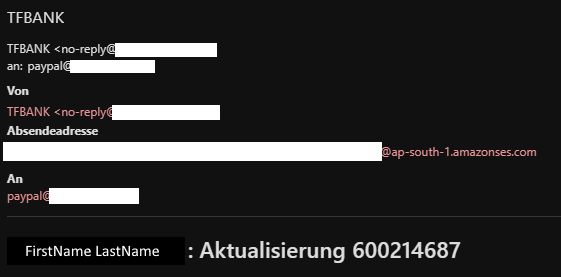
Someone got hold of emails used with PayPal and sends a bunch of #Phishing mails claiming to be the Austrian Bank tfbank.
There's a link that goes to a fake site with a login field to steal bank credentials.
I've got an idea: #Blockchain #AI for #BigData processing.
I don't know what that would be, but those three buzzwords together gotta make any investor cum right away.
Just broke off a nail while opening a MacBook.
Putting rubber which turns into glue over time around the display is absolutely one of the decisions Apple ever made.
They finally let me check out as a guest.
Thank you oh ever so gracious Fairphone for letting me give you 40€ for a fucking battery.
I'd love to contact them about this but until someone gets around to read my mail they probably will have fixed it.