Adrian —dangerously-skip-permissions Sanabriasawaba@infosec.exchange
10/20/2026RE: https://infosec.exchange/@sawaba/117451837863770138
Yeah, that's my thought as well 😅
RE: https://infosec.exchange/@sawaba/117451837863770138
Yeah, that's my thought as well 😅
POLL: Will AI coding cause a net decrease or increase in tech debt?
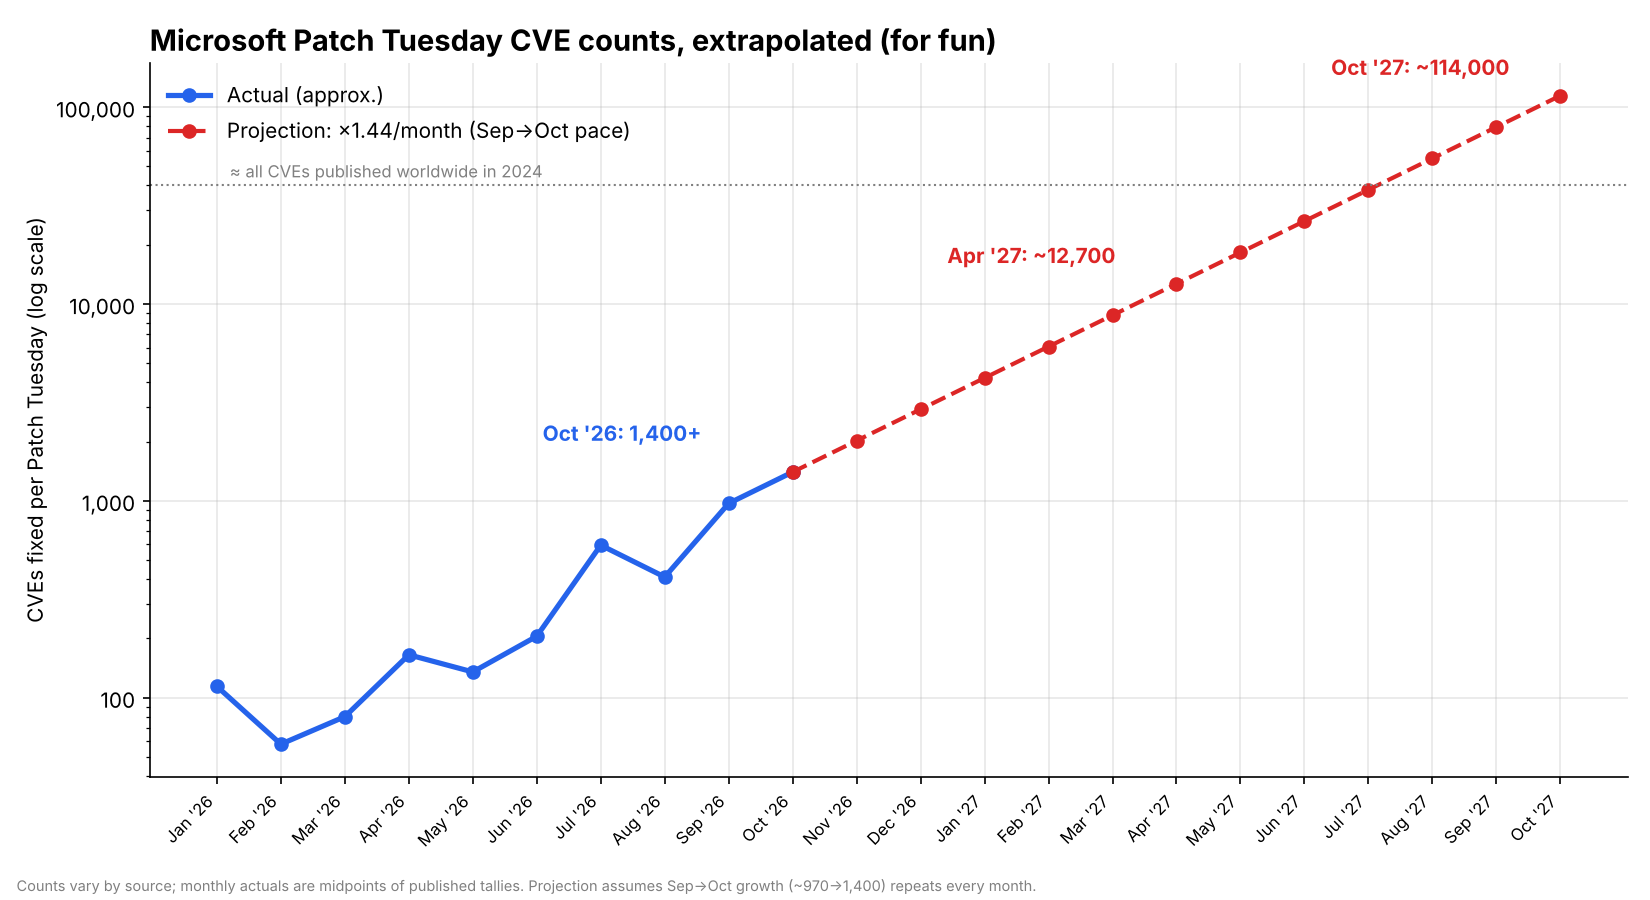
(e.g. Microsoft's 1400+ patch Tuesday this week)
If we analyzed Microsoft Patch Tuesday using the same assumptions industry analysts use with market growth
So I encountered some interesting fraud today and wanted to get some feedback on how it might have happened and advice on what to do next.
The Rocket Money app is the MVP in this story, as it notified me of a large transaction as suspicious less than an hour after it occurred.
A $600 Ubiquiti order that I had supposedly just placed.
As much as I'd like to, I did not order $600 of Ubiquiti stuff today at 4:13pm.
I checked my email, and sure enough, there was an order for an 8-port switch, made from MY Ubiquiti account, with MY primary card that I buy stuff like this with.
Except it was bound for an address I didn't recognize in Madisonville, TN.
I quickly logged into my Ubiquiti account and cancelled the order. Since the charge was still pending, it immediately disappeared and returned the funds to my account.
Crisis averted, but HOW DID THIS HAPPEN?
I reset passwords, logged off sessions, and did all the other things in the Ubiquiti app, but I have no saved payments in the Ubiquiti account - how did they hit my card then?
I keep looking and notice something else interesting - a Link verification code at 4:13pm - the same time as the Ubiquiti order. That answers the question of how my card was accessed.
This code went to my Google Voice number, so no SIM-swapping would have gave someone access to this code. They were somehow able to create the order without the code.
So now I'm going into Link (Stripe's consumer-facing app that makes it super easy to buy stuff) and deleting all my payment options. The only login option was passkey.
I also froze my card, since I'm still unable to figure out how someone was able to create this order in my Ubiquiti account via Link, with my card, but send it to a different address.
I started looking for breaches and this is writeup on compromised Stripe API keys from Hudson Rock my current best guess as to how this fraud happened: https://www.infostealers.com/article/analyzing-stripe-breach-confirmed-vendor-exposure-and-claims-of-20000-compromised-apis/
I currently have no other theories. What have I missed? Does this sound plausible? I'm not sure compromised Stripe APIs can explain the Link piece of the puzzle.
Random intrusive thought: why was scary spice scary? I never understood that.
All the other Spice girls’ names were descriptive of how they looked or dressed. Did Mel B have a history of chunkla tossing?
There are many more that I missed the day of the event and look forward to checking out now that they're all published!
https://www.youtube.com/@BSidesKnoxville
Follow @bsidesknoxville here and on YouTube!
My friend Stephen Hilt, a researcher at Trend, always has some interesting research to share. Words of the Wicked: How Language Divides and Unites Cybercriminals gives a rare look into how language influences groups and communities of cybercriminals.
Friend and repeat BSides Knoxville speaker Chris Craig delighted me with his presentation, titled Stacking the Deck.
It was not only chock full of useful, actionable information on how to use AI for offensive security and how he builds harnesses, but was also highly successful in using a deck-building game metaphor.
Not only was the metaphor fun, Chris decided that instead of using AI-generated images for his slides, he'd draw them himself, which was chef's kiss for me.
I wish more people put this level of thought and love into the talks they give.
My friend and mentor, @wendynather, keynoted the event and also sat front row for my talk - always lovely to have support in the front row!
Her keynote, Brother can you spare a token explores how AI affects the security poverty line.
BSides Knoxville just released this year's videos and I'm excited to share not just my talk, but some of the others I enjoyed the day of the event and have been wanting to share!
My talk, Rebuilding security strategy from breach lessons, shares some of the most interesting insights I've gleaned from studying breaches over the past decade.
https://youtu.be/nyXP7lRwhPA?t=96
thread continues
@taviso except this Cisco vuln is due to SQL injection! Something that everyone knew how to fix over TWENTY years ago.
@taviso it was over a decade ago, here's the link if you want to feel super old and tired along with me
https://projectzero.google/2016/06/how-to-compromise-enterprise-endpoint.html
Remember when @taviso discovered you could compromise Symantec's secure email gateway with an email, because their AV engine was using a 7 year old, vulnerable unpacker?
I remember, and it makes me feel tired and old
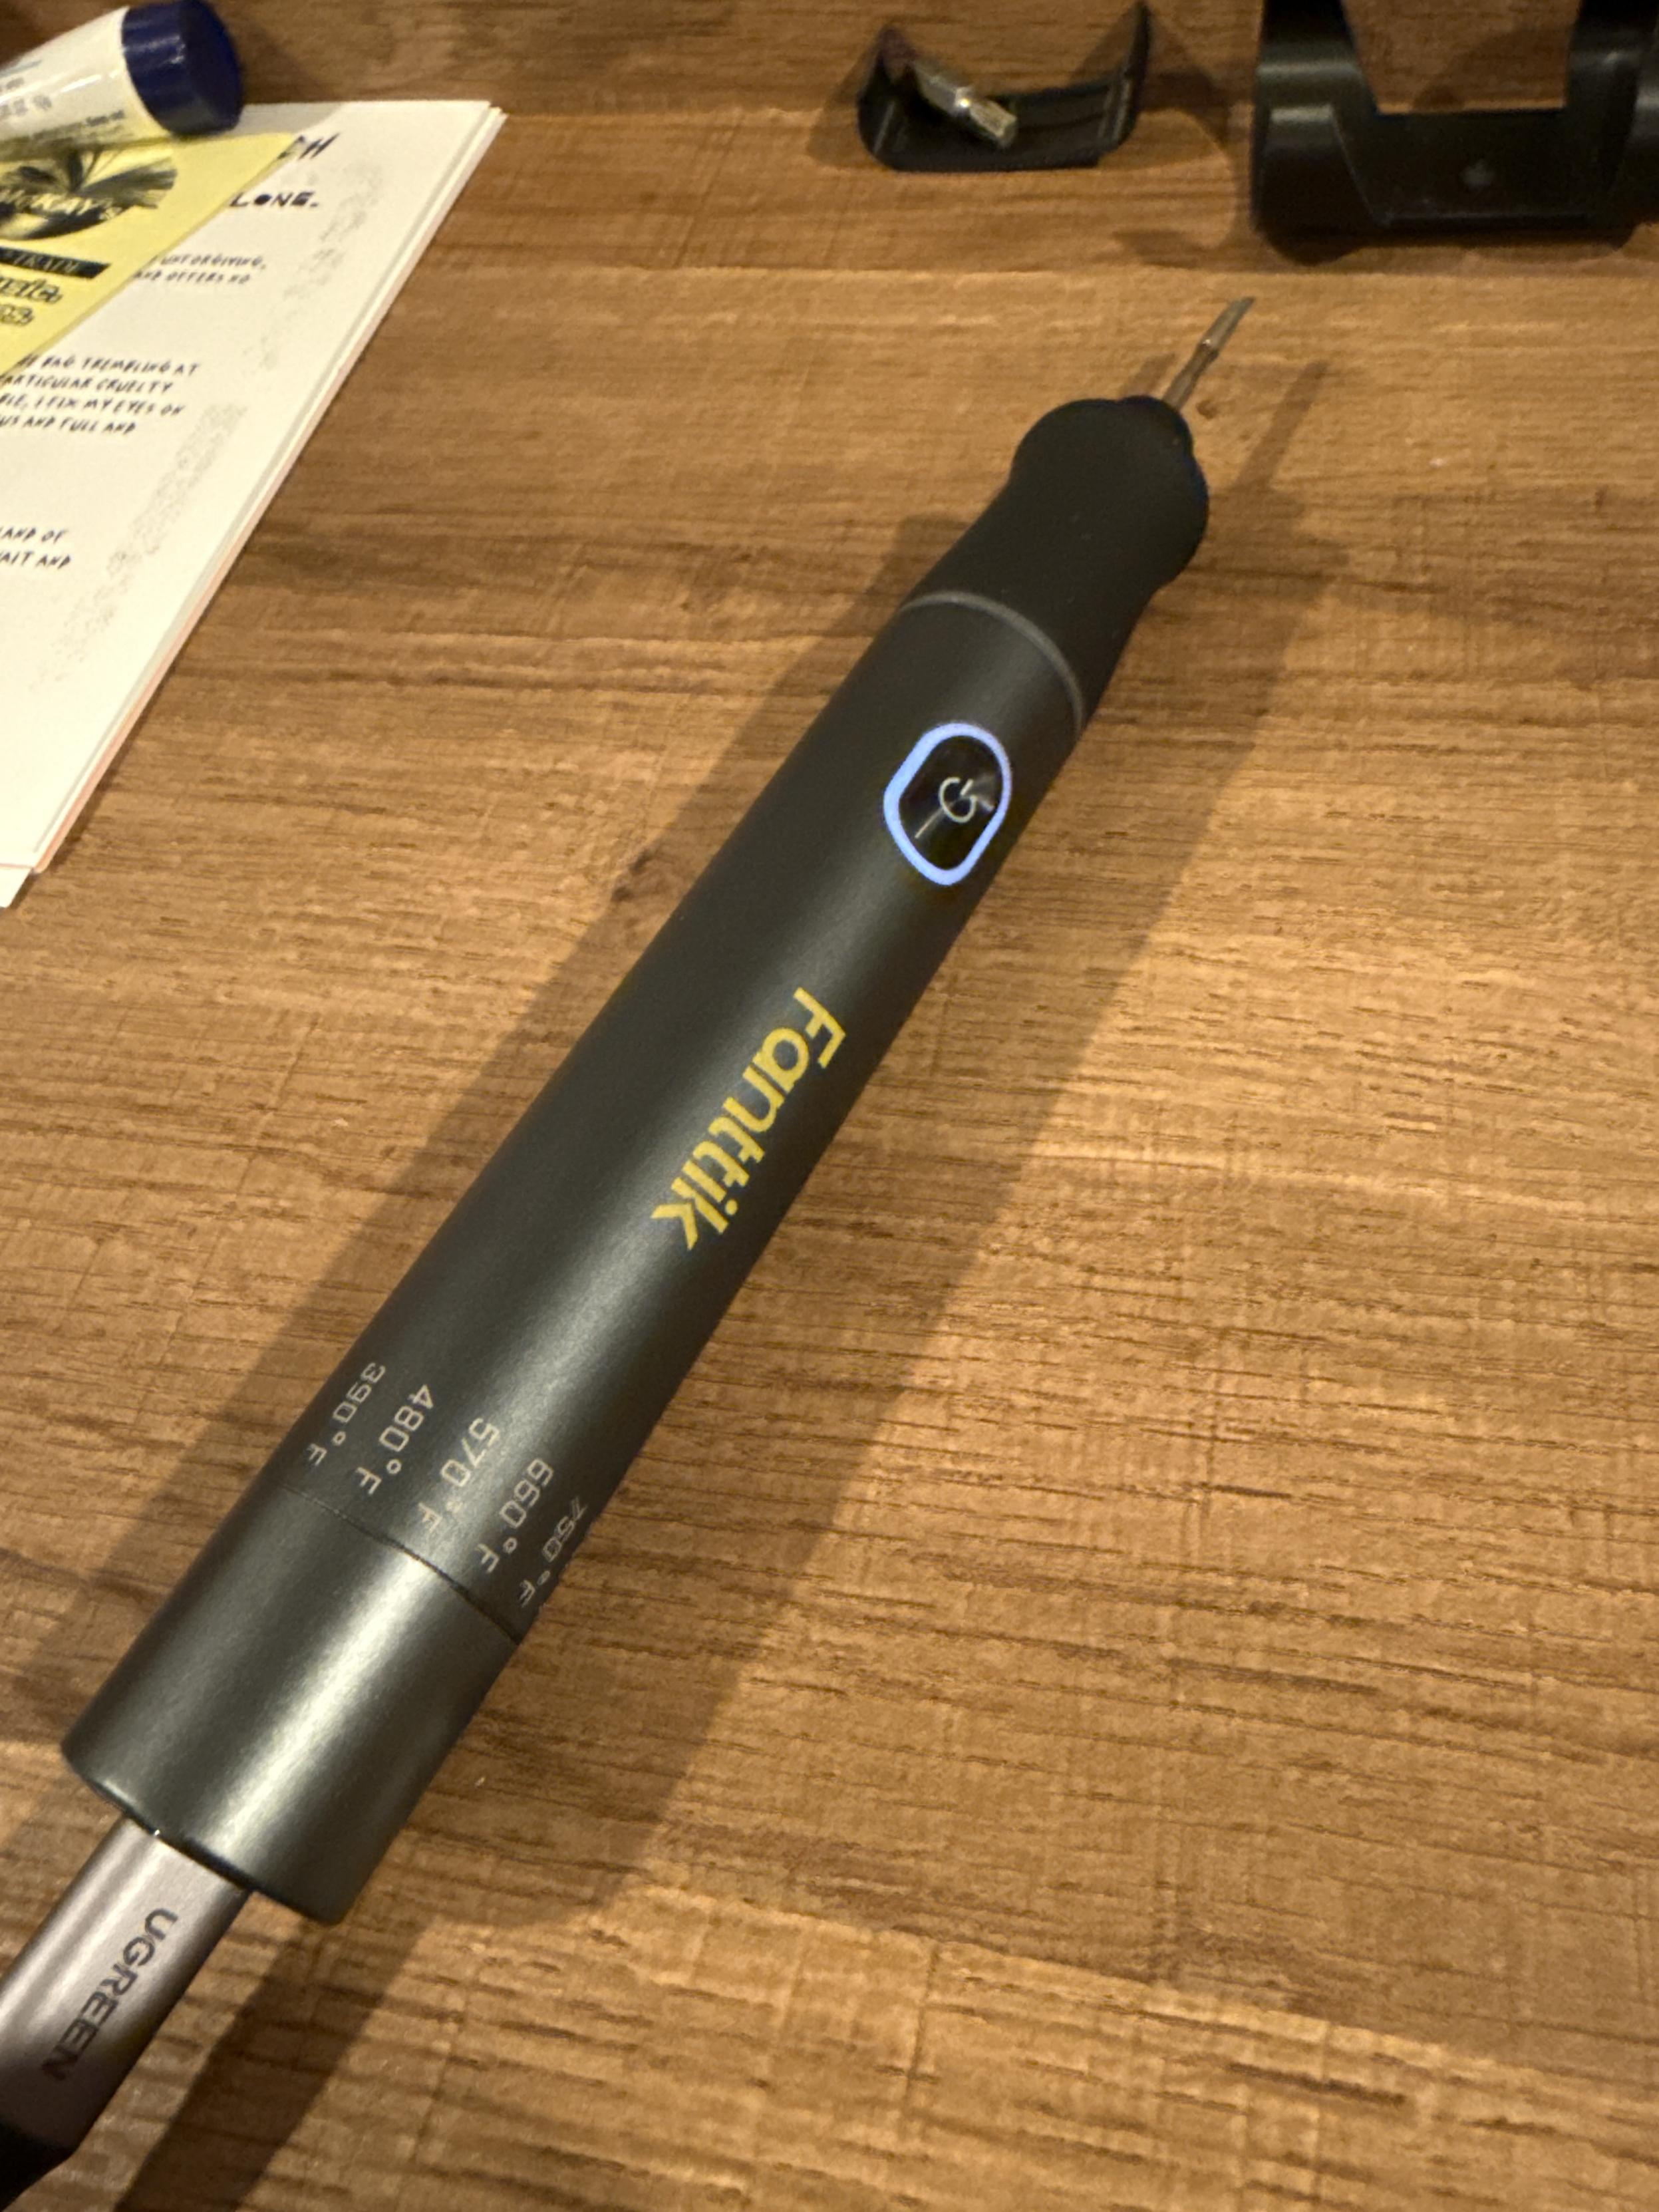
And of course, my portable soldering iron’s battery is dead
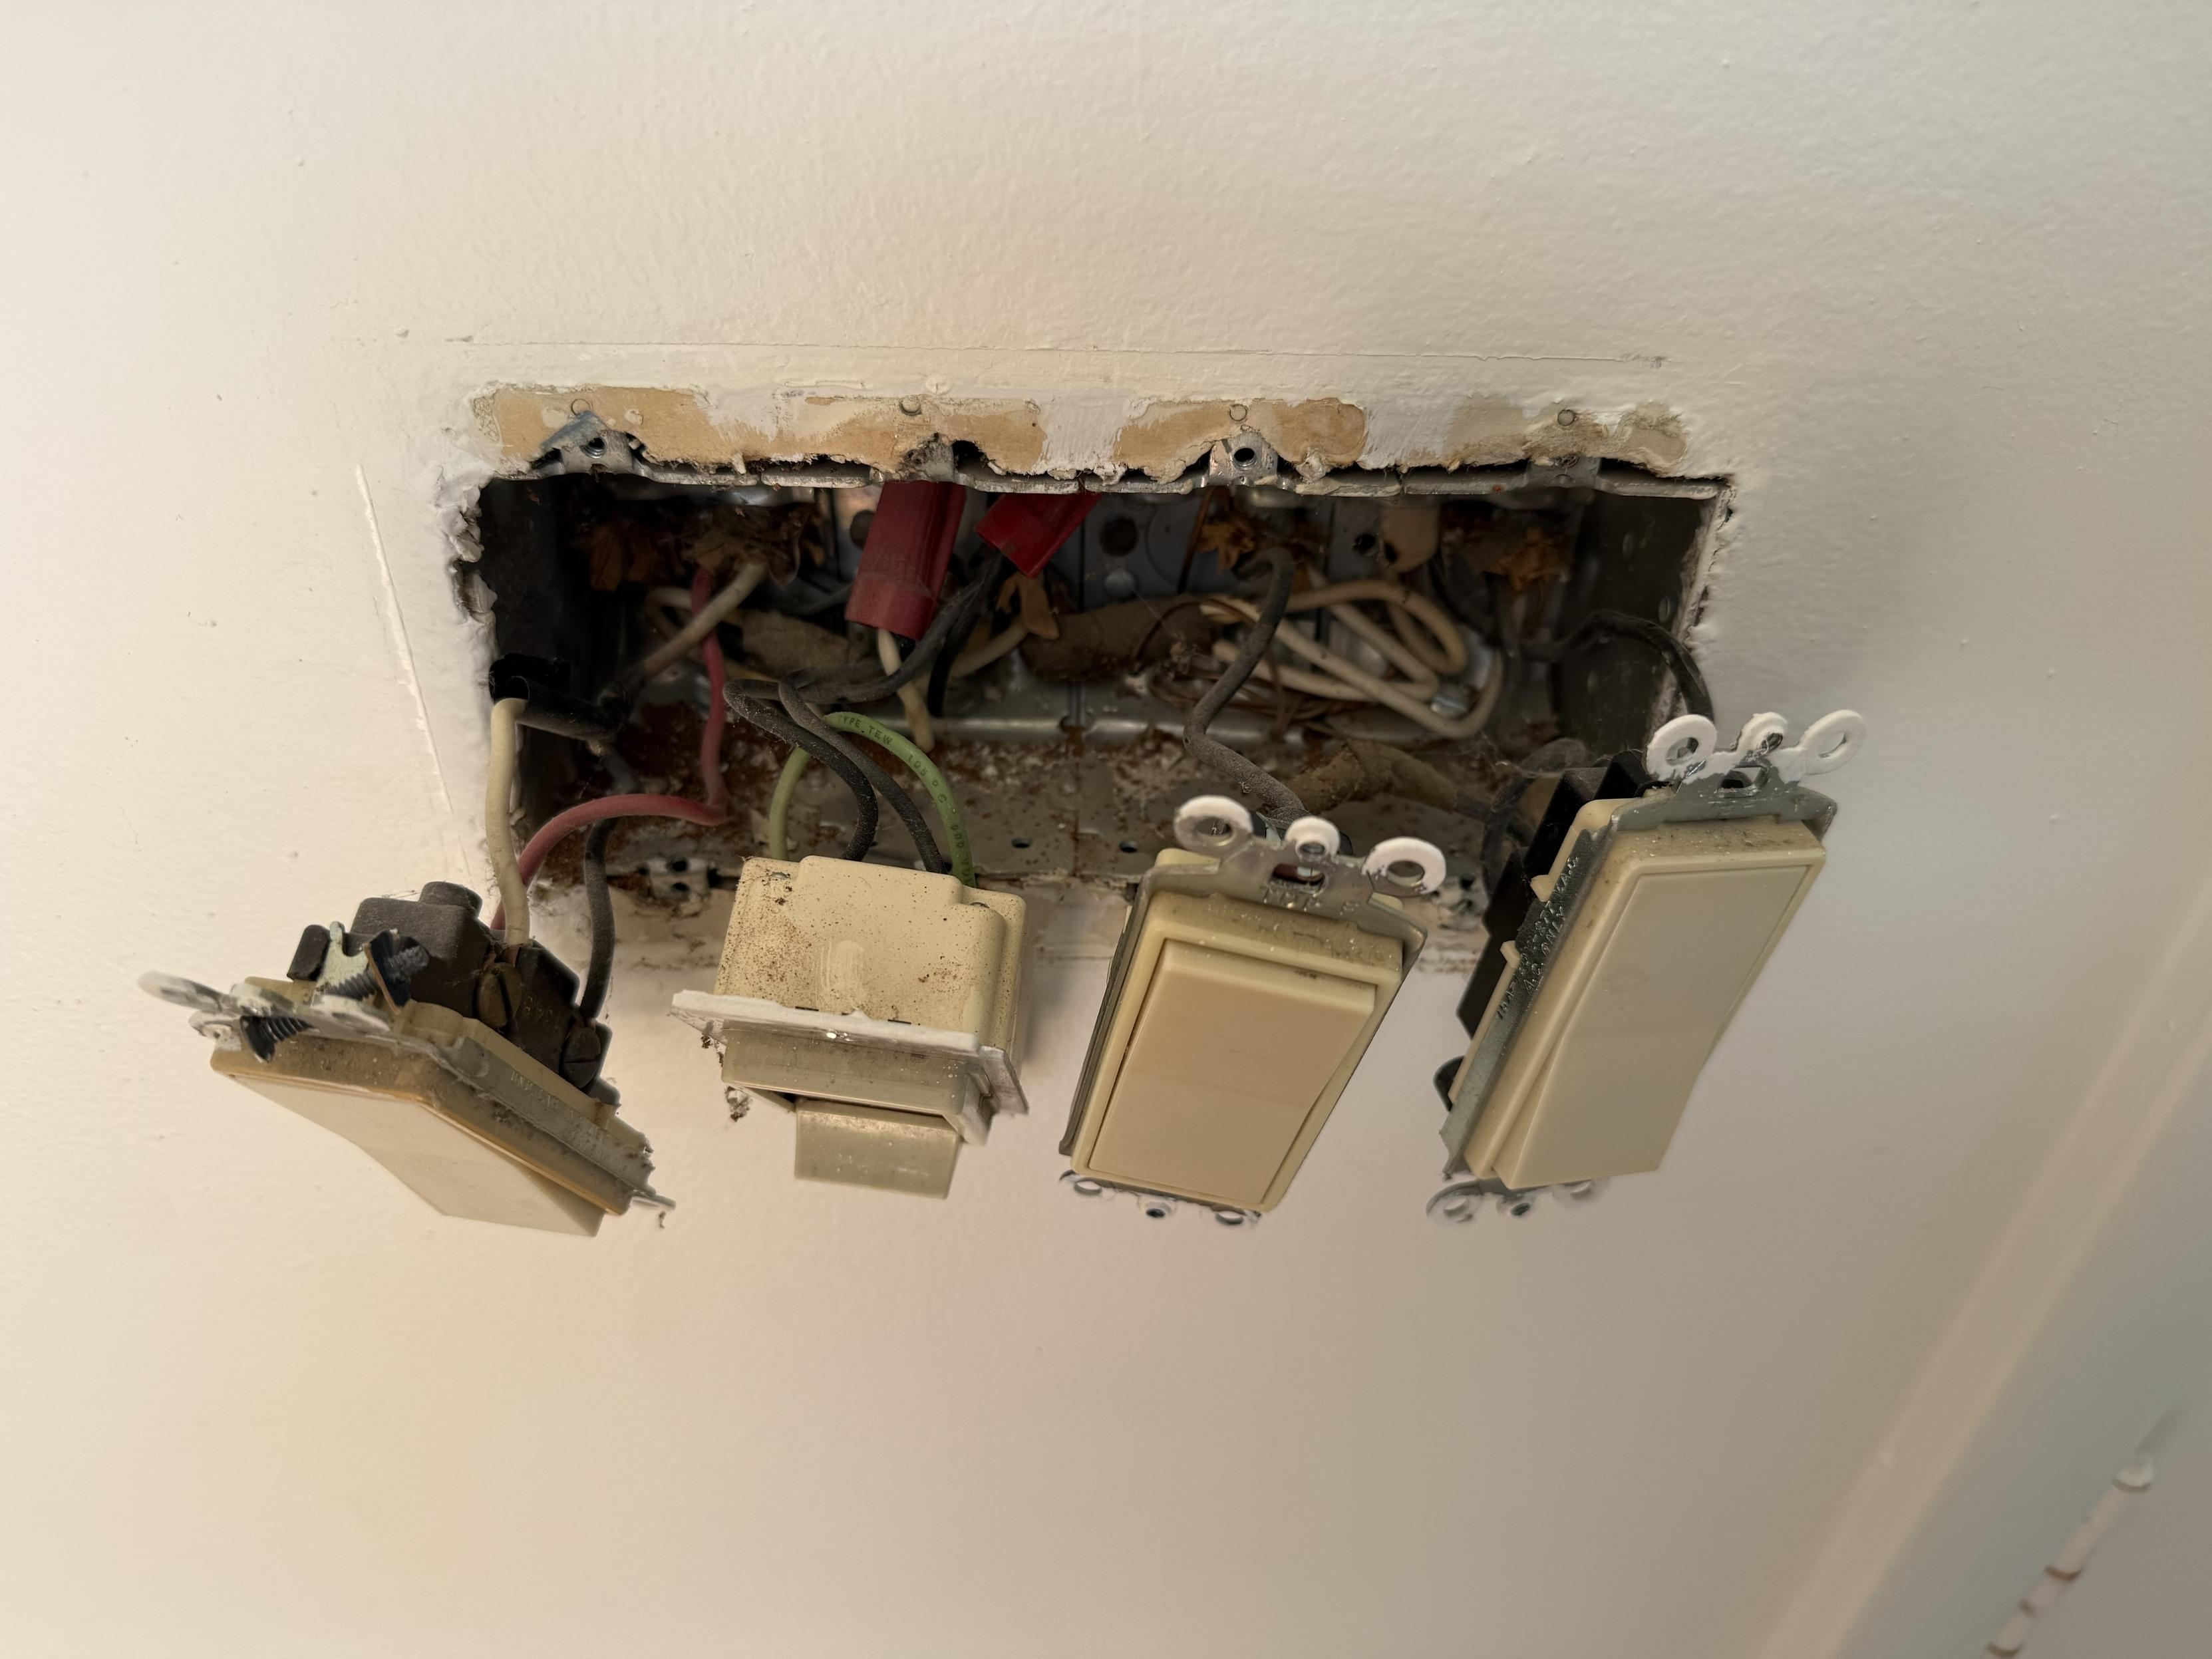
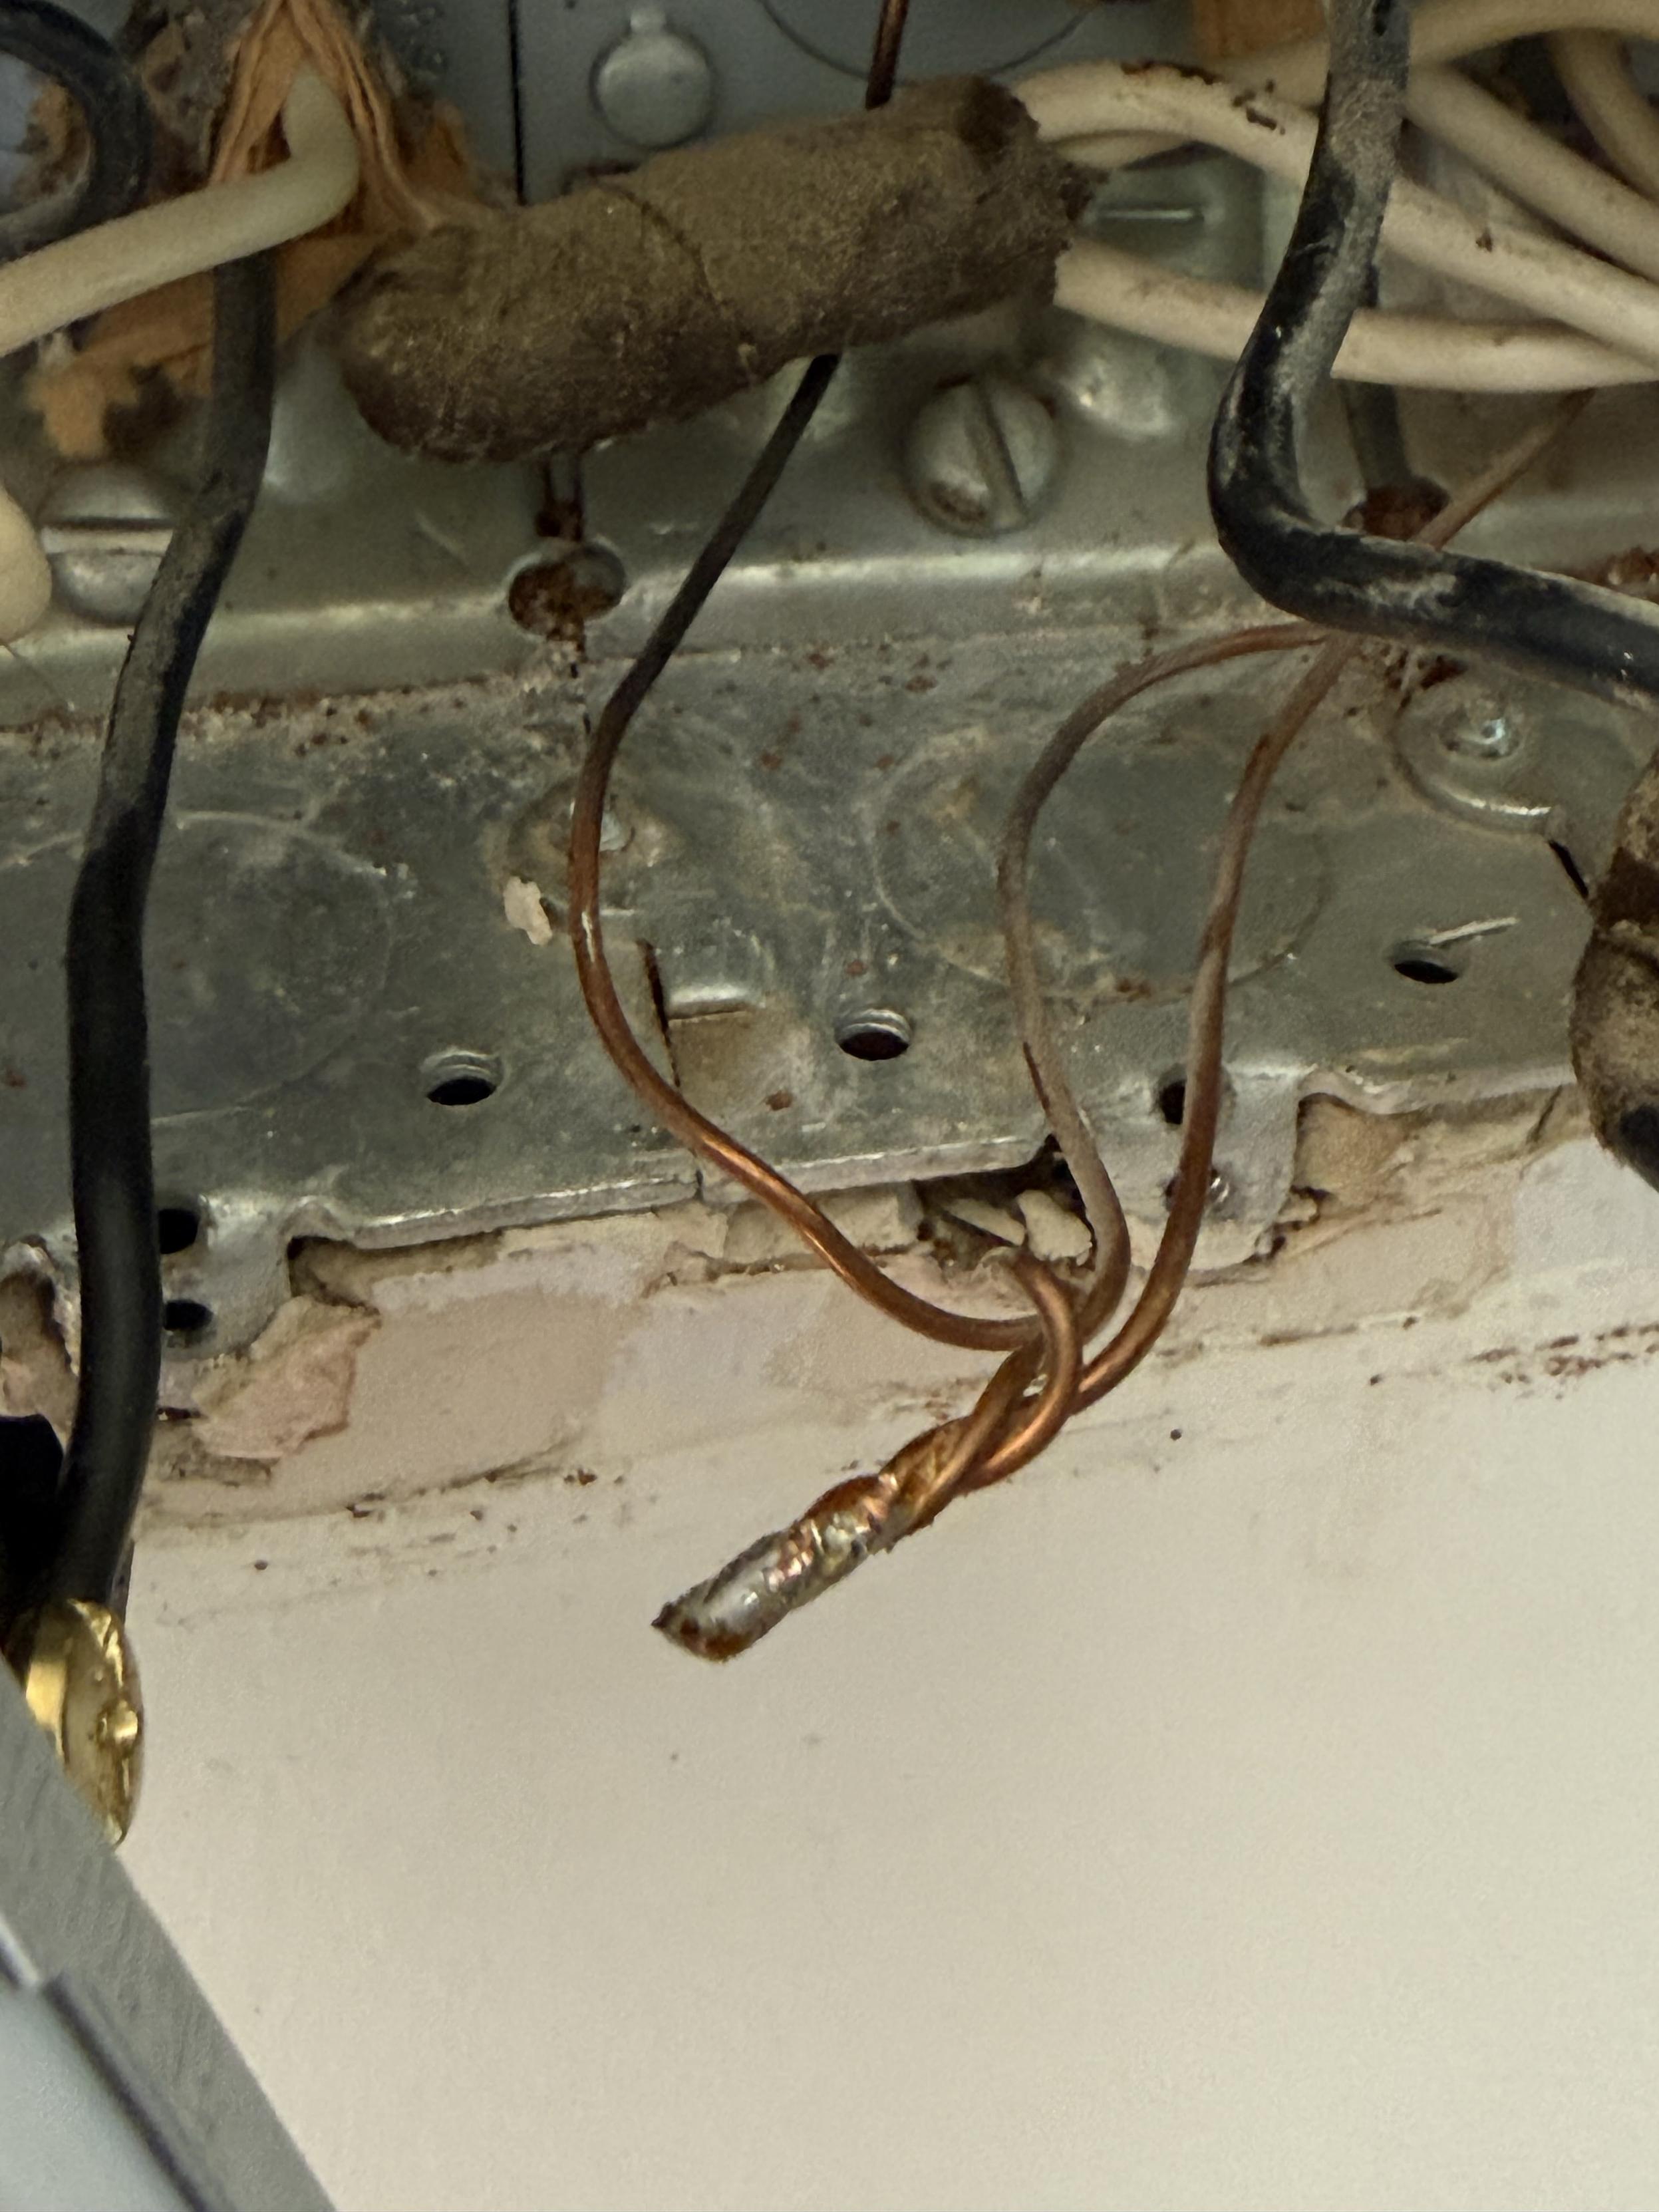
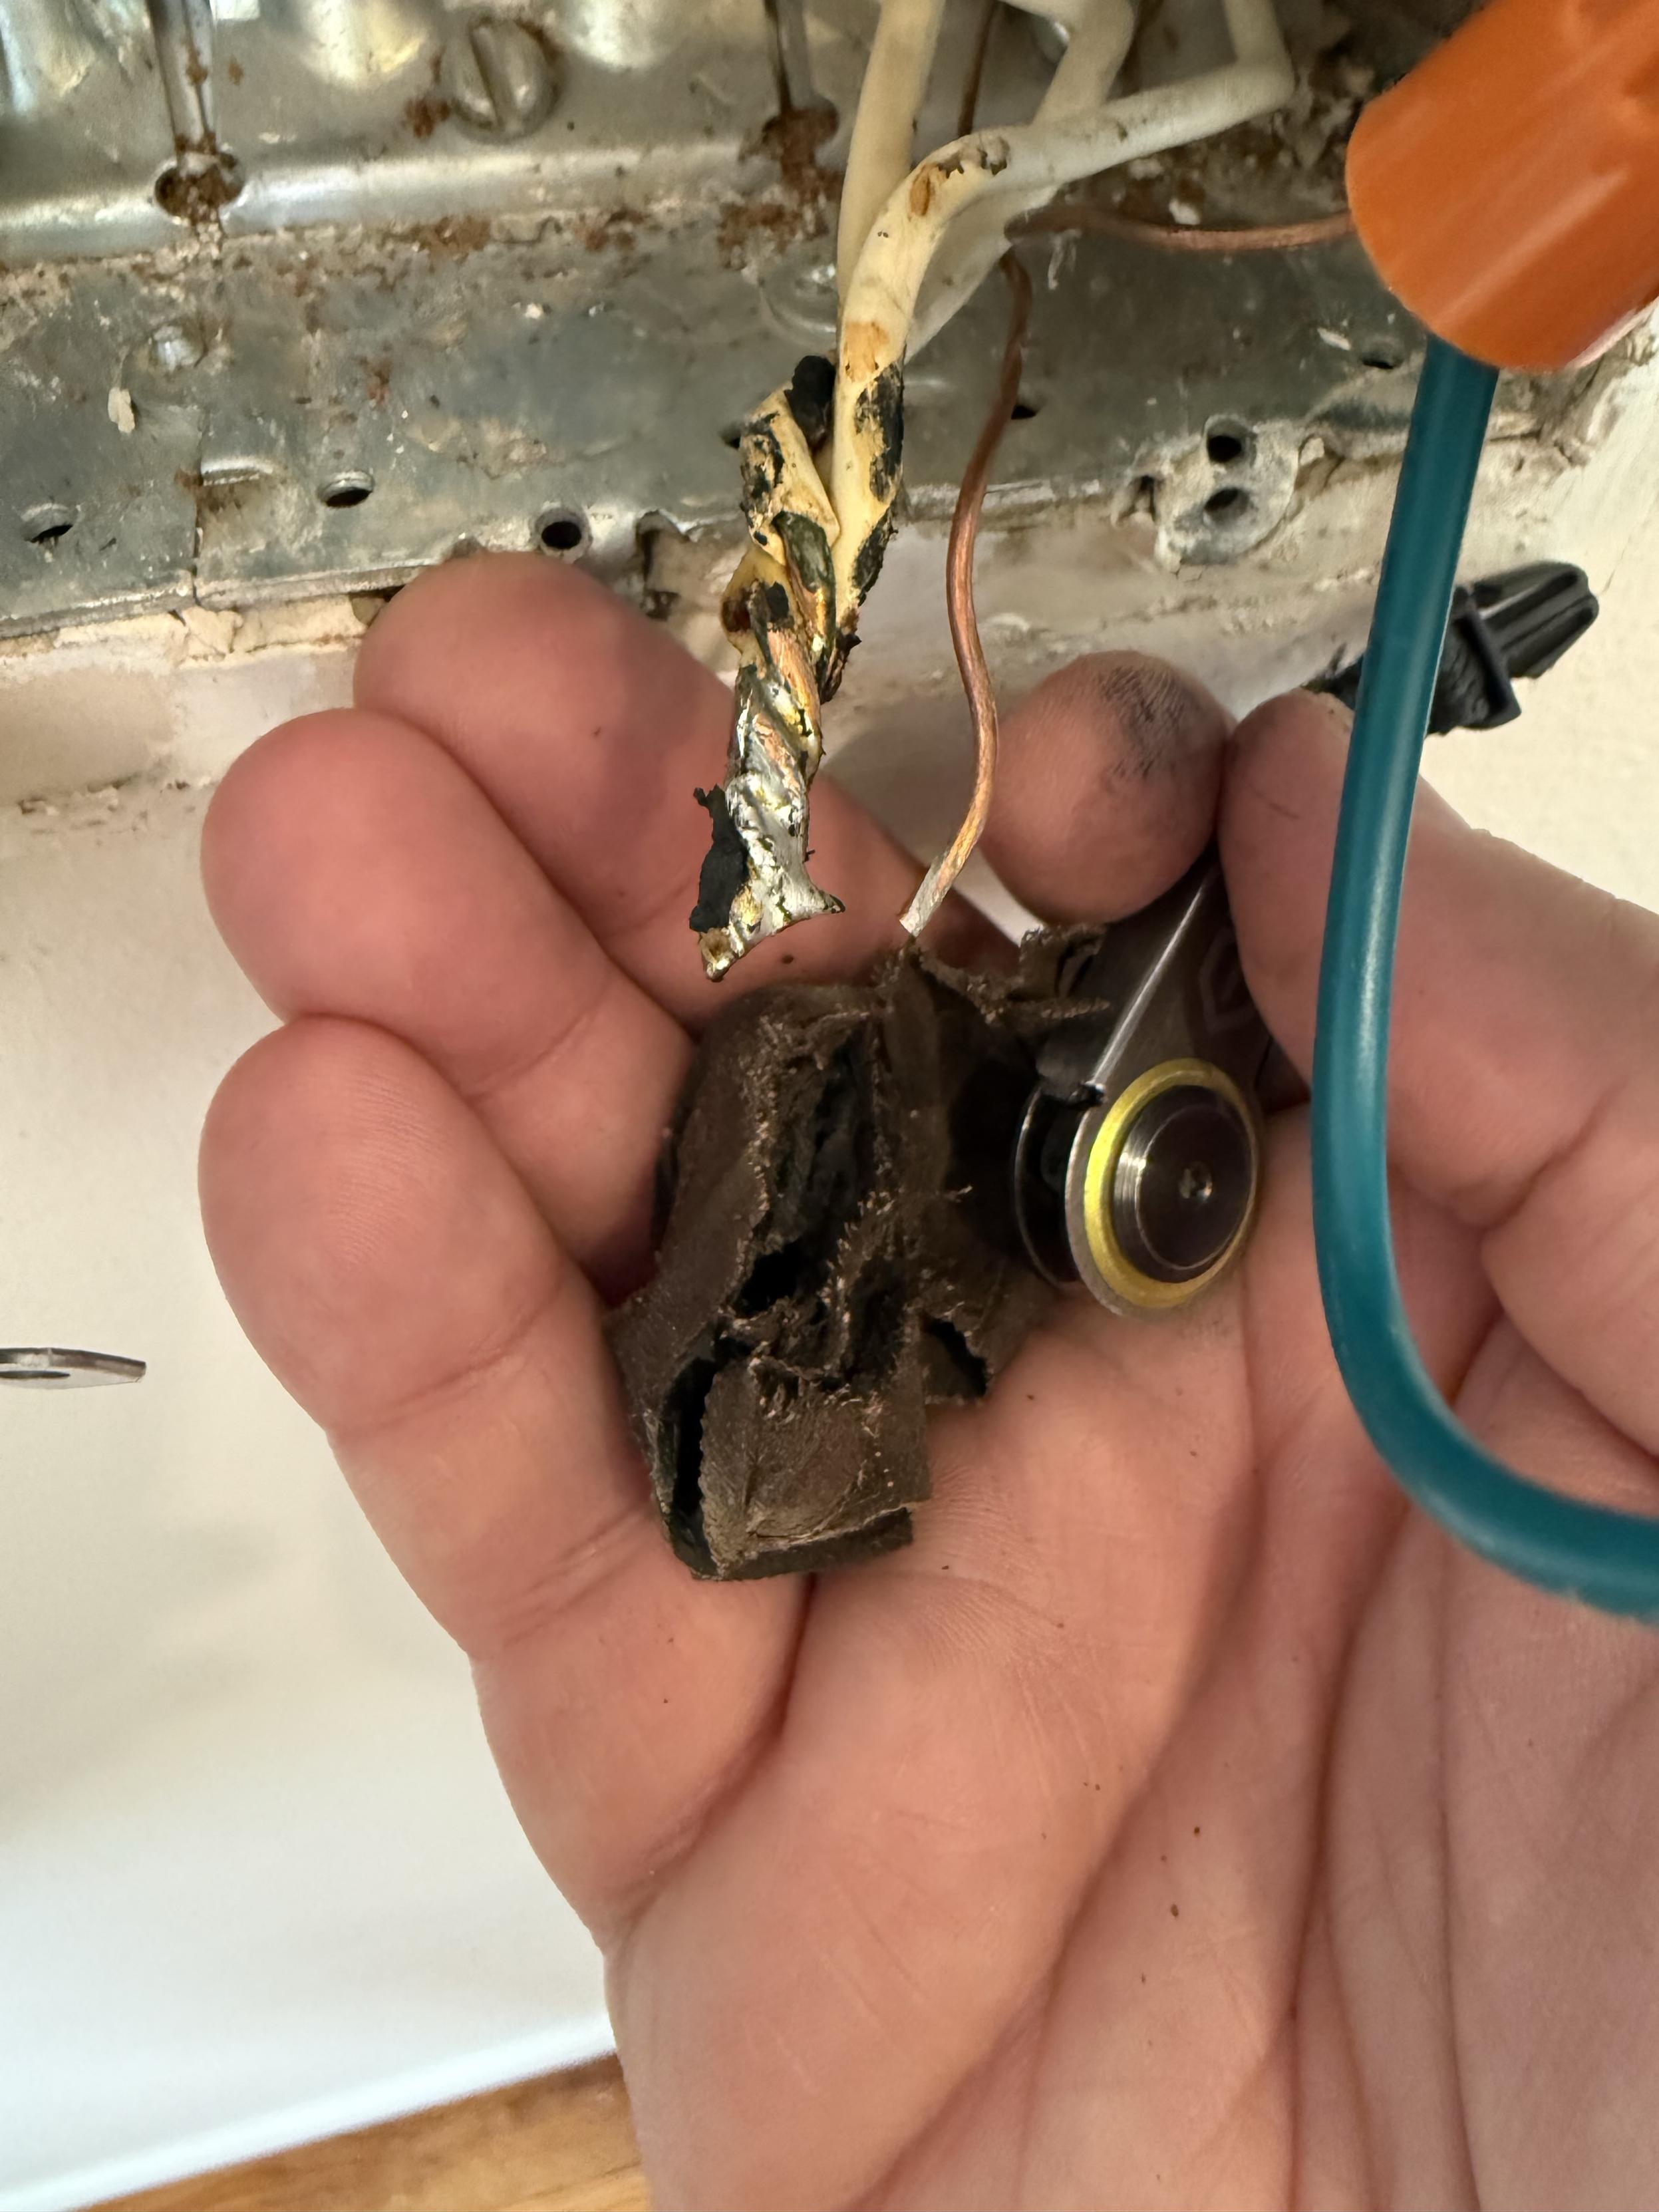
This wiring project is killing me. I don’t know how old this work is, but who both says “fuck grounding things” and then SOLDERS the unused wires together???
This is very “I don’t know the person that will have to deal with this next, but fuck them” energy
RE: https://cyberplace.social/@GossiTheDog/117082934696297430
You could cross your fingers that attackers have hard drives too small to extract the 153GB RAR and can't afford larger drives because AI made storage expensive
but I wouldn't count on it
My thoughts on 1Password’s latest research https://www.defendersinitiative.com/p/reviewing-initial-research-on-using
WTAF is the image on this blog post???
Who in corporate marketing thought this was a good image to use?
RE: https://infosec.exchange/@jerry/116912680840905478
This is more IT asbestos (re: Progress ShareFile)
Don't patch this stuff, permanently replace it
https://www.defendersinitiative.com/p/the-asbestos-of-it-why-old-protocols
For anyone interested, I've shared the slides from my @bsidesknoxville talk https://hosted-files.sched.co/bsidesknoxville2026/d2/Beautiful.ai%20-%20Rebuilding%20Security%20Strategy%20from%20Breach%20Lessons%20ALT.pdf