Login
You're viewing the 101010.pl public feed.
  • Sep 29, 2026, 1:33 AM

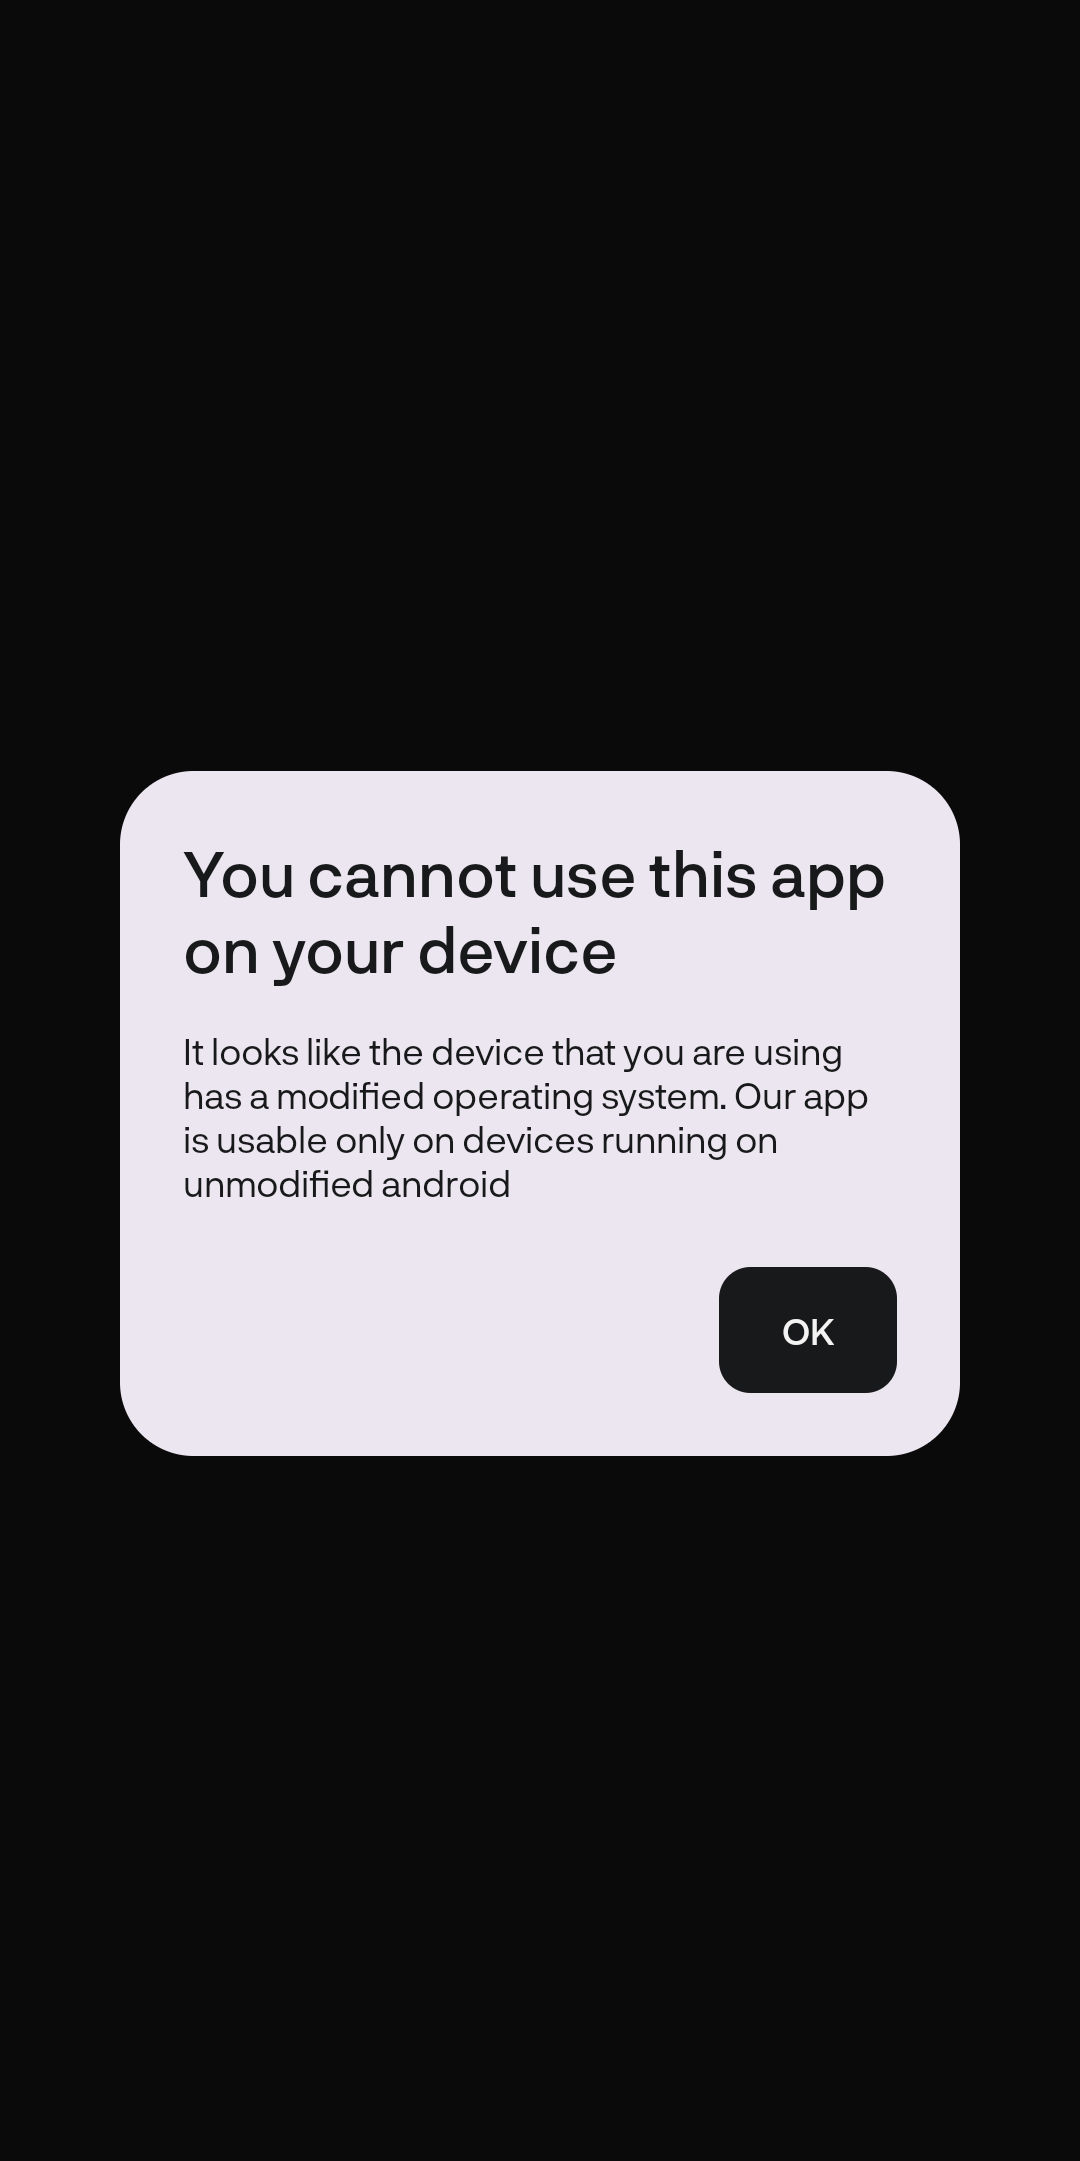
    I used to use #grapheneos to access Microsoft teams. Recent updates, has made it recognise device as rooted and I can no longer use it. I am seeing so many apps adopting this, makes me worried about future of alternative OS. Governments doesn't care about #grapheneos users to push for regulations.
    Pain points:
    1. Play integrity adoption
    2. Checking whether phone is using alternative OS
    3. Every app can know what other apps are installed and if it doesn't like the neighbor app it stops working
    💬 1🔄 0⭐ 2

Replies

  • Sep 29, 2026, 5:01 AM

    The solution could be @GrapheneOS could somehow introduce a feature where apps will just get to know that it's not a modded os. I would pay to have this feature.

    💬 0🔄 0⭐ 0
  • Sep 29, 2026, 10:25 AM

    @abhiyantrik It can be resolved by disabling secure spawning on a per-app basis for the impacted Microsoft apps. It's due to incorrect anti-tampering checks by the apps.

    We can likely resolve it by masking more of the under the hood differences caused by secure spawning. There aren't any known cases of secure spawning breaking correctly written apps anymore, but there are still cases of apps with incorrect anti-tampering code checking strange implementation details and refusing to run with it.

    💬 3🔄 1⭐ 0
  • 💬 1🔄 0⭐ 0
  • Sep 29, 2026, 11:00 AM

    @abhiyantrik Try the overall per-app exploit protection compatibility mode for the app. You can then narrow it down to a specific toggle or set of toggles from there if it ends up solving it. The overall per-app exploit protection compatibility mode sets all of the toggles below to the compatibility mode.

    💬 1🔄 0⭐ 0
  • Sep 29, 2026, 11:37 AM

    @GrapheneOS tried everything still no luck. Is there any way does the app know that it's a modded os? Can we patch that?

    💬 1🔄 0⭐ 0
  • Sep 29, 2026, 1:28 PM

    @abhiyantrik It isn't a modded OS. It's a different OS also based on AOSP. There's no way to fully hide that it's a different OS since there are many differences and it isn't based on the stock OS. There are many ways apps can detect it including from added privacy and security features. Resolving these deliberate compatibility issues mostly needs to be done by app developers. We can work around it ourselves but do not have the time to reverse engineer and work around each case of it.

    💬 1🔄 0⭐ 0
  • 💬 0🔄 0⭐ 0
  • Sep 29, 2026, 3:48 PM

    @GrapheneOS Surprised to hear you can disable secure spawning for individual applications now (and not only system wide). Is this a recent addition?

    💬 1🔄 0⭐ 0
  • Sep 29, 2026, 8:20 PM

    @lstngr It was nearly fully reimplemented in the 2026071100 release to provide better app compatibility and to make it possible to disable it at the same time as hardened_malloc. Being able to disable it at the same time as hardened_malloc enabled making it into one of the per-app exploit protection compatibility mode toggles. We also worked around a bunch of app compatibility issues caused by anti-tampering code. Can see a bunch of those changes in the release notes for subsequent releases.

    💬 0🔄 0⭐ 0
  • Dustinpretend_radar_engineer@mastodon.social
    Sep 30, 2026, 4:18 PM

    @GrapheneOS @abhiyantrik that was super helpful! I ran into this exact issue with Teams a while back. I also had to disable secure spawning for the Intune "Company Portal" app. Now I'll get Teams notifications at home again, a bit conflicted on that part 🫠

    💬 0🔄 0⭐ 0