In less than eight years; on 2034-06-16 the epoch number will start with 20340616 - matching the current date. Starting at 09:06:40 UTC, lasting 100 seconds.
For those who celebrate.
The next time that happens is 850 years later.
In less than eight years; on 2034-06-16 the epoch number will start with 20340616 - matching the current date. Starting at 09:06:40 UTC, lasting 100 seconds.
For those who celebrate.
The next time that happens is 850 years later.
Actual #curl rewrites in #rust (not by me)
https://daniel.haxx.se/blog/2026/11/17/actual-curl-rewrites-in-rust/
Apparently it takes about 8,600 USD to rewrite #curl in rust using Claude: https://claude.ai/artifact/K4BoWt35HQz1xWZBR3bMRD
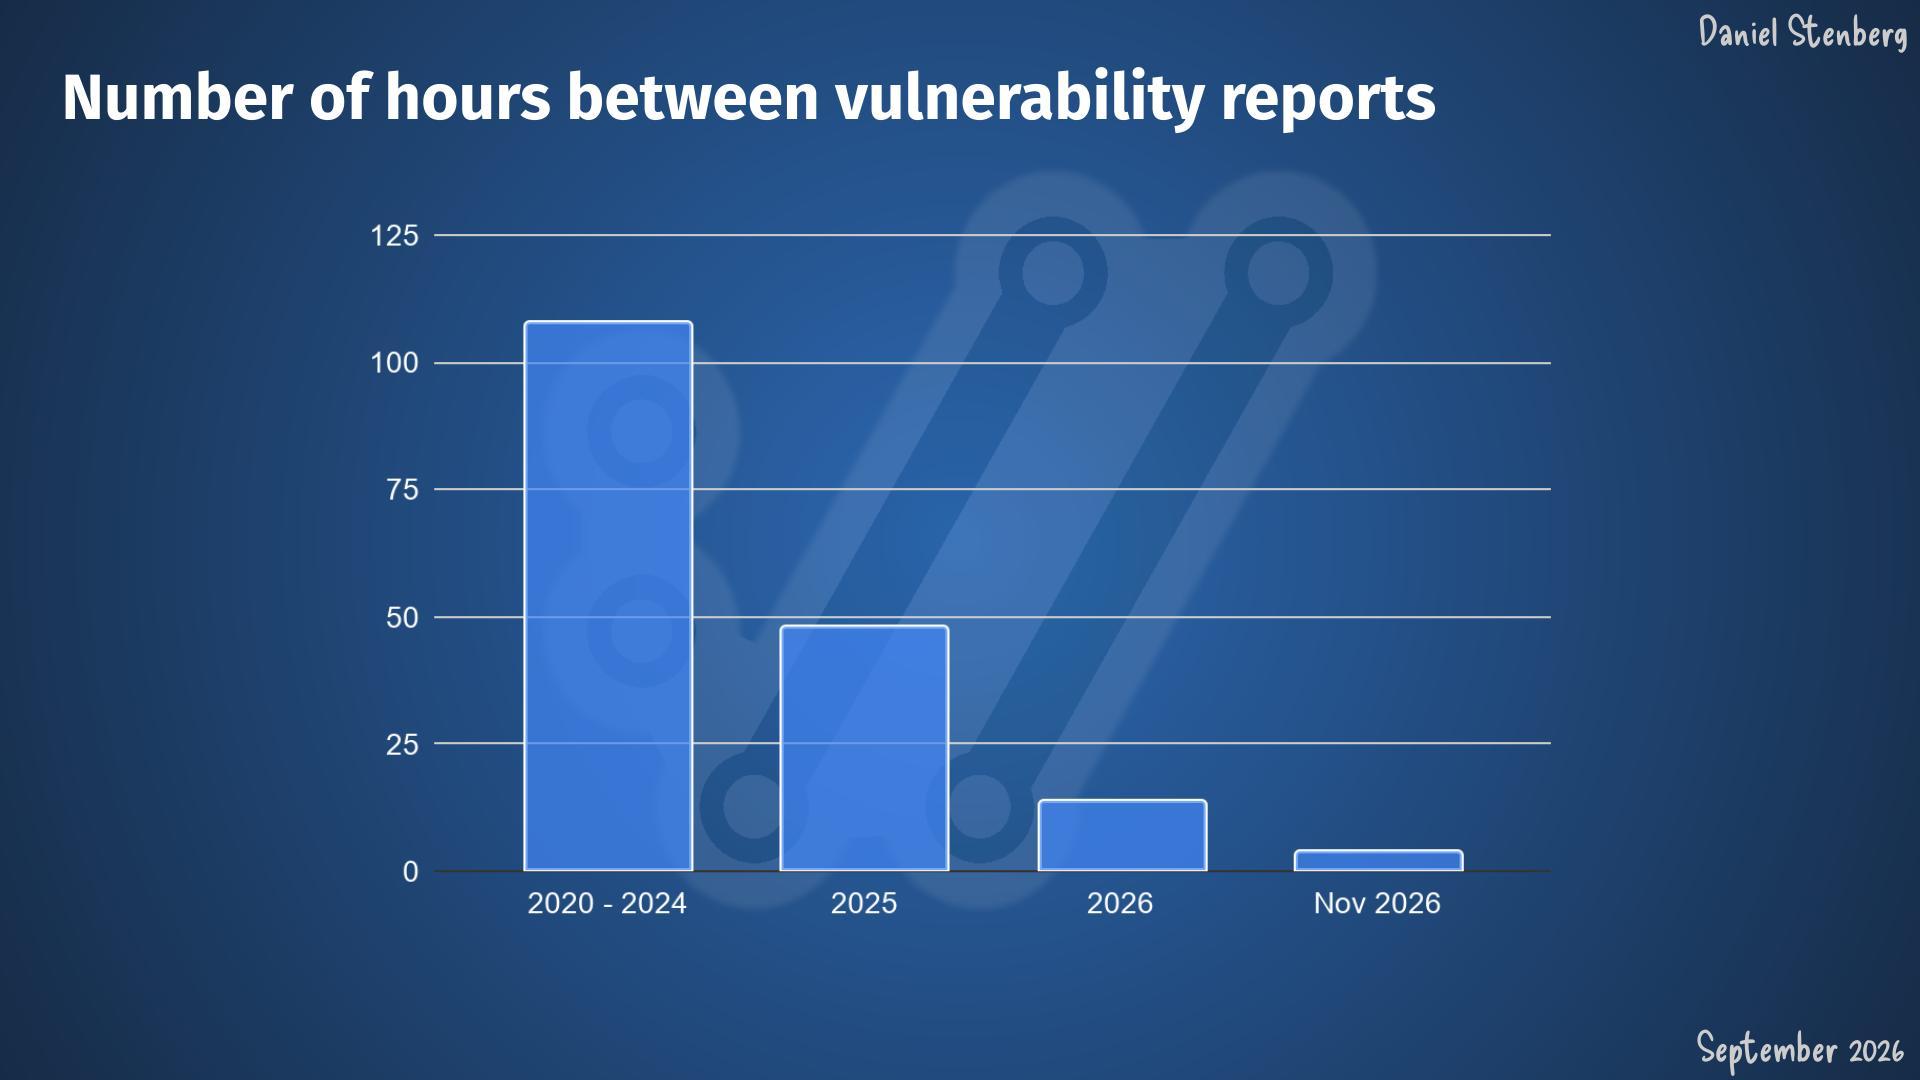
Over the last two weeks, we (#curl) have received one vuln report every 7 hours.
"Completely fixing complex vulnerabilities without creating new ones or breaking functionality is where today’s AI systems are weakest."
their backlog was at 14,000 CVE requests the other day...
The CVE system breaks down further as GitHub is lagging behind so badly now that projects move on and publish their vulns without CVEs, leaving those to (perhaps) get backfilled in a future.
I hope you can excuse me for the 4,500 words, but man, thirty years!!
30 years of Internet transfers with curl
https://daniel.haxx.se/blog/2026/11/11/30-years-of-internet-transfers-with-curl/
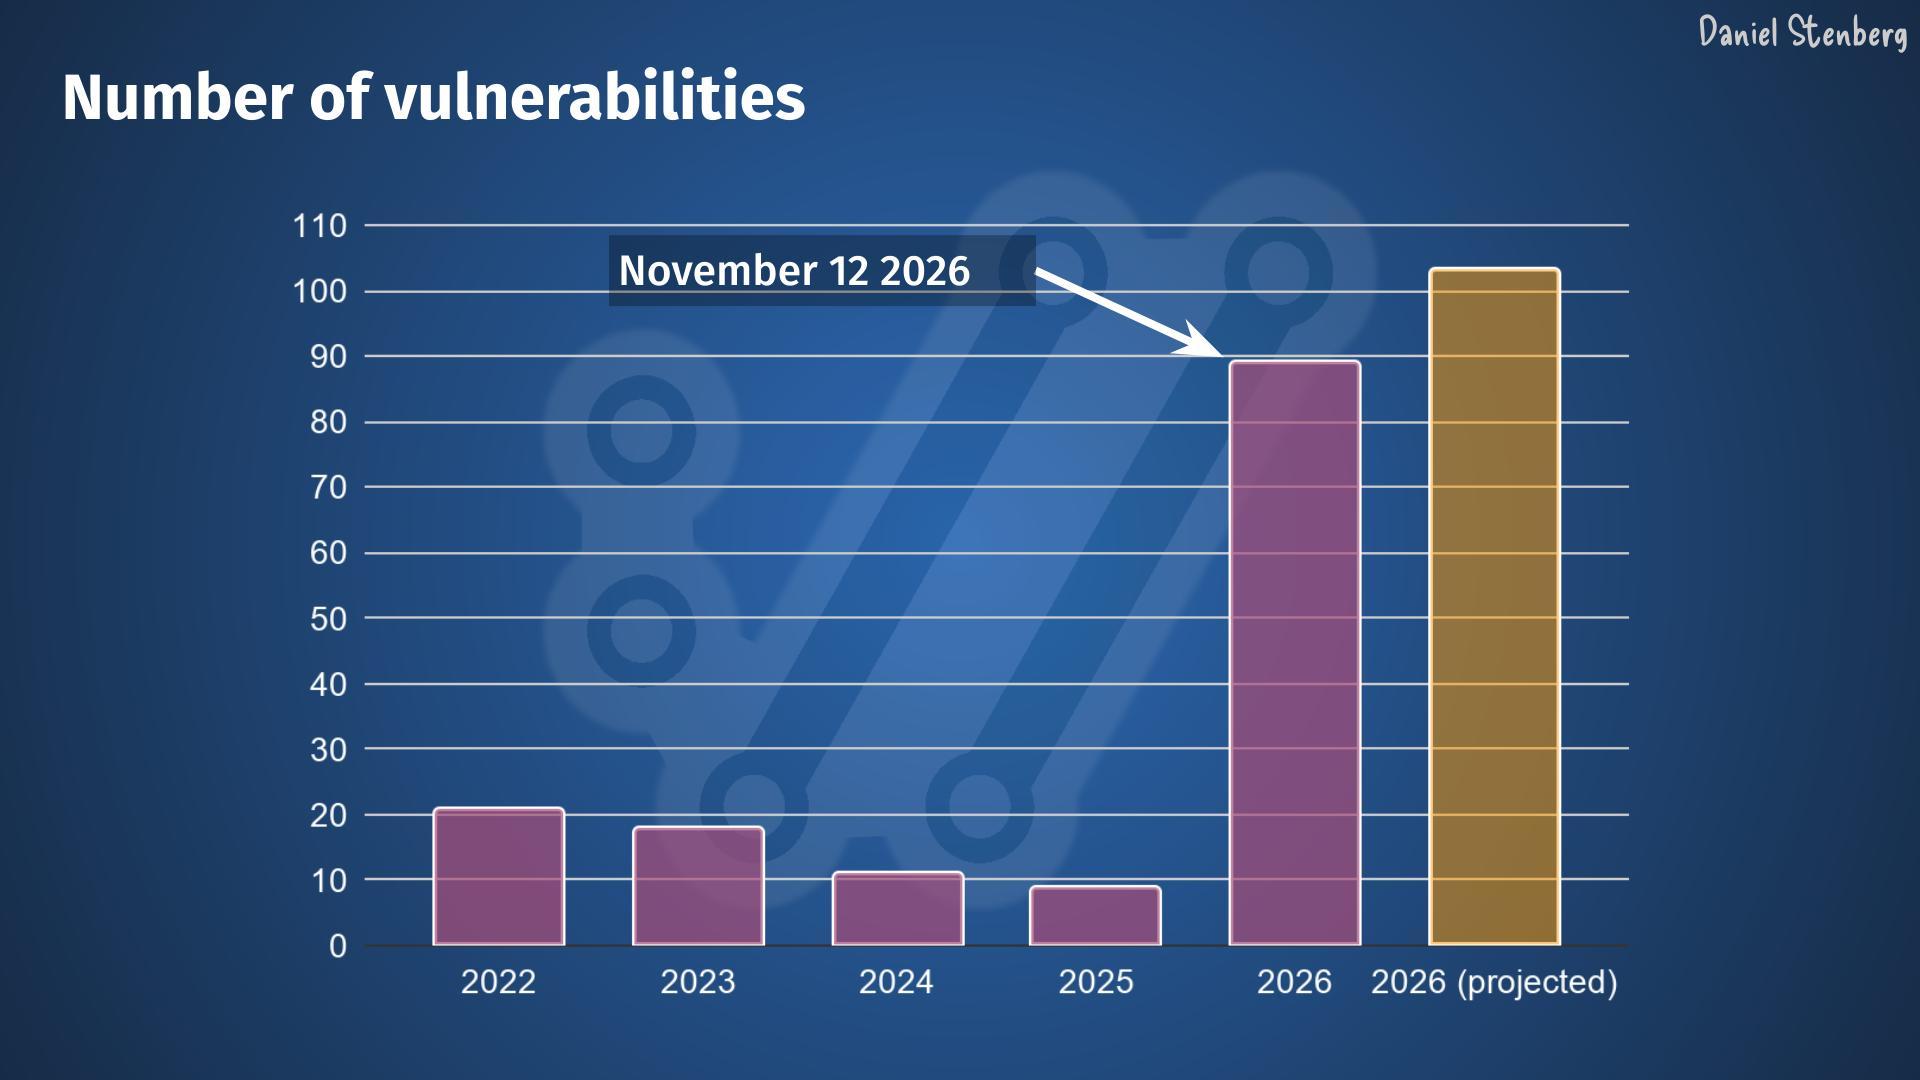
out of Anthropic's latest 45 findings in #curl, we are at 7 confirmed LOW. 37 "just a bug" and one completely false.
for those who follow: yeah, we're gradually raising the bar for what we accept as LOW severity #curl vulnerabilities.
"curl took a bold move by deciding to publish low and medium vulnerabilities findings publicly as issues for full transparency and we encourage other open source maintainers to follow their lead."
🪅
https://www.vulncheck.com/blog/anthropic-glasswing-november-update
here are the 45 findings Anthropic reported to #curl last week: https://github.com/curl/curl/issues?q=is%3Aissue+ANT-2026
don't forget to order yourself a cake for Wednesday to properly partake in the #curl 30 years celebrations
The trillion dollar monsters are all focusing on *finding* issues at high speed in large volumes. Hardly any of them care about *fixing* these problems with any sense of quality.
yesterday the #curl project got an email from a person announcing their grand new project to security audit a range of Open Source projects. Got a fancy project name and all. Asked for permission.
Two hours later the same person emailed us again, announcing that he shuts down this effort blaming "widespread failure affecting Codex".
We never got to respond. Moving on.
High volume AI vulnerability reports with Daniel Stenberg
https://youtu.be/mmYFHkkCAV8?is=pg-6EurWSlxBN7a1
"How curl was accidentally Turing-complete for nine months"